
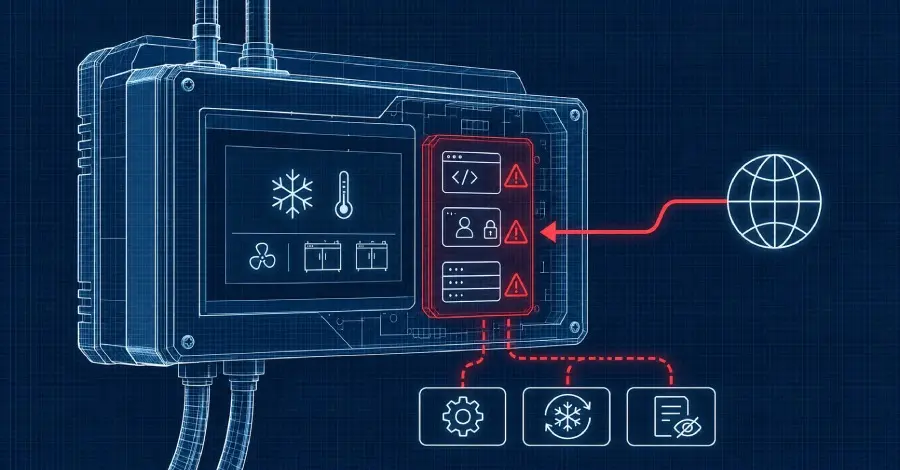
A series of severe security vulnerabilities discovered in widely used industrial refrigeration controllers has prompted urgent warnings from national cybersecurity agencies across Europe. The flaws, found in the Danfoss AK-SM800A series, could allow remote, unauthenticated attackers to seize full control of the systems, potentially leading to the destruction of temperature-sensitive inventory and significant operational disruptions in supermarkets and food storage facilities.
The vulnerabilities were identified by Midnight Blue, a specialized security consultancy based in the Netherlands. According to the firm’s research, the flaws are present in the management interface of the AK-SM800A, a device designed to monitor and regulate refrigeration and freezing units. The researchers have sounded the alarm because, as of this week, no official patch has been released to address these specific issues. Furthermore, the latest firmware update provided by the manufacturer, version 5.4.0, reportedly fails to mitigate the risks.
The discovery has triggered a coordinated response from government cybersecurity bodies in Belgium, Ireland, and Germany. These agencies have taken the unusual step of advising all operators of Danfoss AK-SM800A controllers to immediately remove their management interfaces from the public internet. The consensus among these authorities is that traditional security measures, such as updating firmware or enabling enhanced login protections, are currently insufficient to protect against a targeted exploit of these newly discovered bugs.
A Growing Pattern of Cyberattacks on Cold Storage
The timing of this discovery is particularly concerning given the recent wave of cyberattacks targeting European infrastructure. Starting on October 11, supermarket chains in France reported mysterious malfunctions in their cooling systems. These incidents, which researchers and government agencies have linked to unauthorized access of refrigeration controllers, caused unwanted defrost cycles that ruined massive quantities of perishable stock.
A second wave of similar attacks was observed across Europe just last week, suggesting that threat actors are actively seeking out and exploiting vulnerable industrial control systems (ICS) within the food supply chain. While the German Federal Office for Information Security (BSI) confirmed that the AK-SM800A was involved in previous incidents where refrigeration units were tampered with across multiple countries, it noted that there is currently no direct evidence linking the six newly discovered flaws to those specific historical attacks. However, the potential for these flaws to be utilized in future campaigns remains a primary concern for national security experts.
The vulnerabilities are not merely theoretical. Midnight Blue researcher Carlo Meijer reportedly discovered the six flaws in less than an hour of manual review using firmware that is publicly available for download from the vendor’s website. This ease of discovery highlights a significant security gap in the architecture of the controllers, which are relied upon by maintenance firms to manage store environments remotely.

Technical Breakdown: Root Access and "Strict Mode" Failures
The technical details provided by Midnight Blue paint a troubling picture of the device’s security posture. Five of the six vulnerabilities reside within web request handlers that do not require any form of authentication. Crucially, these handlers operate within a program that runs with root privileges—the highest level of access on the system. By exploiting one of these flaws, an attacker could execute arbitrary code with root authority, effectively gaining total control over the controller’s functions.
 Cybersecurity Basics & Security News
Google Intelligence Report Warns of Paradigm Shift as Threat Actors Deploy Autonomous Agentic AI Frameworks
In a comprehensive assessment that underscores a fundamental transformation in the digital...
 Cybersecurity Basics & Security News
The Evolution of the Vulnerability Gap: Defending Against the Rise of Mythos-Class AI Attacks
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities...
 Cybersecurity Basics & Security News
The Silent Proliferation: Enterprise Security Grapples with the Rise of Invisible AI Agents
As the enterprise landscape prepares for the full-scale integration of artificial intelligence,...







