
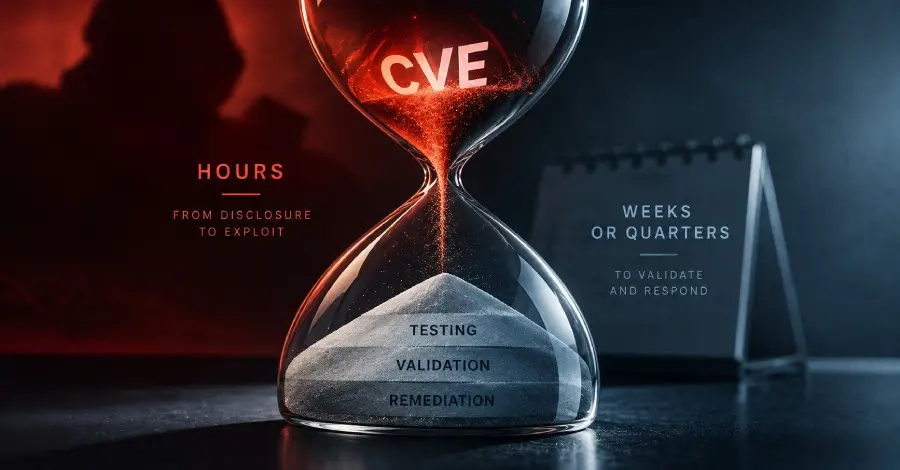
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities and Exposures (CVE) entry is a routine, yet often stressful, occurrence for security operations centers worldwide. For years, the workflow has remained largely the same: a vulnerability is disclosed, automated scanners identify its presence within the network, and security teams scramble to assess the damage based on the Common Vulnerability Scoring System (CVSS). When a score hits the "critical" or "high" range, the pressure to patch intensifies. However, as the digital threat landscape enters a new era defined by "Mythos-class" artificial intelligence, this traditional approach is proving increasingly inadequate. The fundamental question facing defenders today is no longer whether a vulnerability exists, but whether it can be weaponized within their specific environment before they have the chance to respond.
The emergence of Mythos-class AI represents a significant leap in the capabilities of adversarial technology. These advanced AI systems are designed to compress the time between the public disclosure of a vulnerability and the development of a functional, weaponized exploit. In the past, this window—often referred to as the "time to exploit"—could span weeks or even months, giving organizations a fighting chance to test and deploy patches. Today, that window is shrinking toward near-instantaneity. While many enterprise security programs still operate on validation cycles that occur weekly, monthly, or even quarterly, the reality of the modern threat environment is that the gap between a disclosed flaw and a compromised system is now measured in hours, or even minutes.
The Limits of Severity-Based Prioritization
For many years, the CVSS score has served as the primary North Star for vulnerability management. It provides a standardized way to measure the theoretical risk posed by a software flaw. Yet, a high severity score is essentially a measure of potential, not a confirmation of reality. It tells a security team that a vulnerability could be devastating if exploited, but it offers no insight into whether the specific configurations, network segmentations, or existing security controls of a particular organization would actually allow an attacker to succeed.
This disconnect has led to a state of perpetual "alert fatigue" within security operations centers. Teams are often buried under a mountain of high-severity findings, many of which may be "reachable" but not "exploitable" due to the specific nuances of their environment. Prioritizing remediation based solely on a score leads to a reactive posture where resources are spread thin, often focusing on vulnerabilities that pose little actual risk while missing lower-scored flaws that could be leveraged as part of a sophisticated attack chain.
The challenge is compounded by the speed of Mythos-class AI. These AI models are capable of analyzing code at a scale and velocity that human researchers cannot match. They can identify bypasses for existing security measures and generate exploit code tailored to specific architectural patterns almost as soon as a CVE is published. When the adversary is using machine-speed tools to find a way in, a defensive strategy that relies on manual validation or infrequent scanning is fundamentally mismatched. The dangerous gap that exists today is no longer just a technical one; it is a temporal one.
Bridging the Validation Gap with Real-Time Evidence
To combat the acceleration of threats, security leaders are beginning to shift their focus from simple vulnerability identification to continuous security validation. The goal is to move away from theoretical risk and toward evidence-based defense. This requires a validation loop that can provide immediate answers to the most critical questions: Is this vulnerability accessible from the public internet? Do our current endpoint protections or firewalls block the known techniques associated with this flaw? If an attacker were to exploit this, what would their next move be?
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....
 Cybersecurity Basics & Security News
Beyond Policy Intent: Why Identity Visibility Has Become the Critical Frontier in Modern Cybersecurity
In the current landscape of enterprise security, the traditional perimeter has not...
 Cybersecurity Basics & Security News
Advanced Wazza Phishing Kit Leverages Multi-Stage Routing and Device Code Tactics to Target Critical Global Sectors
The landscape of email-based threats is undergoing a fundamental transformation. Phishing kits,...






