
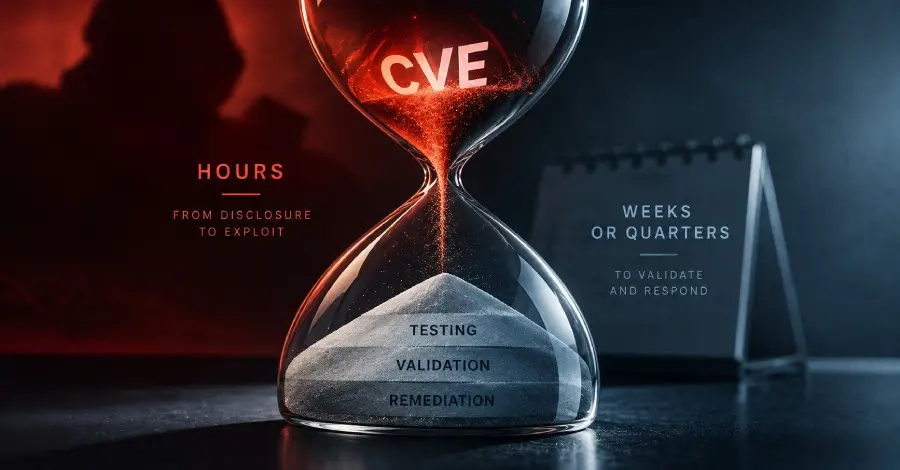
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities and Exposures (CVE) entry is a routine, yet often stressful, occurrence for security operations centers worldwide. For years, the workflow has remained largely the same: a vulnerability is disclosed, automated scanners identify its presence within the network, and security teams scramble to assess the damage based on the Common Vulnerability Scoring System (CVSS). When a score hits the "critical" or "high" range, the pressure to patch intensifies. However, as the digital threat landscape enters a new era defined by "Mythos-class" artificial intelligence, this traditional approach is proving increasingly inadequate. The fundamental question facing defenders today is no longer whether a vulnerability exists, but whether it can be weaponized within their specific environment before they have the chance to respond.
The emergence of Mythos-class AI represents a significant leap in the capabilities of adversarial technology. These advanced AI systems are designed to compress the time between the public disclosure of a vulnerability and the development of a functional, weaponized exploit. In the past, this window—often referred to as the "time to exploit"—could span weeks or even months, giving organizations a fighting chance to test and deploy patches. Today, that window is shrinking toward near-instantaneity. While many enterprise security programs still operate on validation cycles that occur weekly, monthly, or even quarterly, the reality of the modern threat environment is that the gap between a disclosed flaw and a compromised system is now measured in hours, or even minutes.
The Limits of Severity-Based Prioritization
For many years, the CVSS score has served as the primary North Star for vulnerability management. It provides a standardized way to measure the theoretical risk posed by a software flaw. Yet, a high severity score is essentially a measure of potential, not a confirmation of reality. It tells a security team that a vulnerability could be devastating if exploited, but it offers no insight into whether the specific configurations, network segmentations, or existing security controls of a particular organization would actually allow an attacker to succeed.
This disconnect has led to a state of perpetual "alert fatigue" within security operations centers. Teams are often buried under a mountain of high-severity findings, many of which may be "reachable" but not "exploitable" due to the specific nuances of their environment. Prioritizing remediation based solely on a score leads to a reactive posture where resources are spread thin, often focusing on vulnerabilities that pose little actual risk while missing lower-scored flaws that could be leveraged as part of a sophisticated attack chain.
The challenge is compounded by the speed of Mythos-class AI. These AI models are capable of analyzing code at a scale and velocity that human researchers cannot match. They can identify bypasses for existing security measures and generate exploit code tailored to specific architectural patterns almost as soon as a CVE is published. When the adversary is using machine-speed tools to find a way in, a defensive strategy that relies on manual validation or infrequent scanning is fundamentally mismatched. The dangerous gap that exists today is no longer just a technical one; it is a temporal one.
Bridging the Validation Gap with Real-Time Evidence
To combat the acceleration of threats, security leaders are beginning to shift their focus from simple vulnerability identification to continuous security validation. The goal is to move away from theoretical risk and toward evidence-based defense. This requires a validation loop that can provide immediate answers to the most critical questions: Is this vulnerability accessible from the public internet? Do our current endpoint protections or firewalls block the known techniques associated with this flaw? If an attacker were to exploit this, what would their next move be?
This shift in methodology is the focal point of an upcoming industry discussion led by Ishak Celikkanat, Solutions Architect Lead at Picus. In a scheduled live session titled "How to Prove You’re Ready for Mythos-Class Attacks," Celikkanat intends to demonstrate a modernized CVE-to-validation workflow. The core objective of this approach is to provide security teams with the tools to replace assumptions with defensible, data-driven answers while a vulnerability finding is still relevant.
The transition to this model involves moving beyond the "scan and patch" mentality. Instead, it encourages a "validate and mitigate" approach. By simulating the behaviors an attacker would use to exploit a specific CVE, organizations can gain a clear picture of their actual exposure. This process allows teams to see exactly where their defenses hold firm and where they crumble, enabling them to direct their limited resources toward the most impactful remediation efforts.

The Challenge of Testing in Production
One of the most significant hurdles to effective vulnerability validation has historically been the risk associated with testing. Production environments are the lifeblood of any enterprise, and running live exploit code against mission-critical systems is often seen as a recipe for disaster. The fear of causing a system crash or data corruption frequently leads security teams to rely on lab environments that may not accurately reflect the complexities of the live network.
However, the methodology being championed by experts like Celikkanat offers a safer alternative. Rather than running the raw, potentially destructive exploit code, teams can map a specific vulnerability to its constituent attack techniques. By understanding the behavioral patterns required to leverage a flaw—such as specific lateral movement tactics, credential harvesting methods, or data exfiltration paths—defenders can validate their security controls against those specific behaviors.
This behavioral validation provides the necessary evidence of readiness without the risks inherent in direct exploitation. It allows a security team to prove that even if a vulnerability exists on a production server, the existing security stack is capable of detecting and blocking the techniques an attacker would need to use to make that vulnerability "useful." This level of insight is crucial for maintaining operational stability while simultaneously hardening the organization’s security posture against Mythos-class threats.
Adapting to a Changing Environment
The reality of modern enterprise infrastructure is one of constant flux. Cloud environments, containerized applications, and remote workforces mean that the perimeter is no longer a fixed line, but a shifting boundary that changes by the hour. If an organization’s security validation process takes weeks to complete, it is essentially providing a snapshot of a world that no longer exists.
The rise of Mythos-class AI necessitates a move toward automation in the defensive stack that mirrors the automation being used by attackers. If an environment changes within minutes, the validation of that environment must keep pace. This requires integrated systems that can automatically trigger validation tests whenever a new CVE is announced or a significant change is made to the network configuration.
By closing the time gap between disclosure and validation, organizations can effectively neutralize the advantage currently held by AI-driven adversaries. The goal is to reach a state where a security team can confidently report to stakeholders that while a new, high-severity vulnerability has been identified, the organization’s specific controls have already been tested against the associated techniques and found to be effective.
Preparing for the Next Generation of Threats
As the industry prepares for the broader deployment of Mythos-class AI in the hands of both state-sponsored actors and cybercriminal syndicates, the need for a more dynamic defensive strategy has never been more urgent. The upcoming webinar featuring Ishak Celikkanat is designed to provide a roadmap for this transition, offering a live demonstration of how to navigate the CVE-to-validation workflow in a way that is both safe for production and fast enough to matter.
For those unable to attend the live session, the organizers have ensured that the recording and the demonstrated workflows will be made available, recognizing that the need for this information transcends a single time slot. The focus remains on empowering defenders to move beyond the limitations of CVSS scores and toward a future where security is validated, not just assumed.
Ultimately, the battle against Mythos-class attacks will be won by those who can process information and validate their defenses at the same speed with which the adversary evolves. The gap between a vulnerability and its exploitation is closing, and the only way to stay ahead is to ensure that the validation loop is faster, smarter, and more integrated than ever before. In a world where time is the most critical metric, the ability to prove readiness in real-time is the ultimate competitive advantage for the modern defender.
 Cybersecurity Basics & Security News
The Evolution of the Digital Frontier: How AI and Cloud Expansion are Redefining Modern Cybersecurity Strategy
The global cybersecurity landscape is currently undergoing a fundamental transformation, driven by...
 Cybersecurity Basics & Security News
The Rise of the Personal AI Agent: Navigating the Shift from BYOD to BYOAI in the Corporate Security Landscape
The rollout of personal artificial intelligence agents is proving to be a...
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....







