
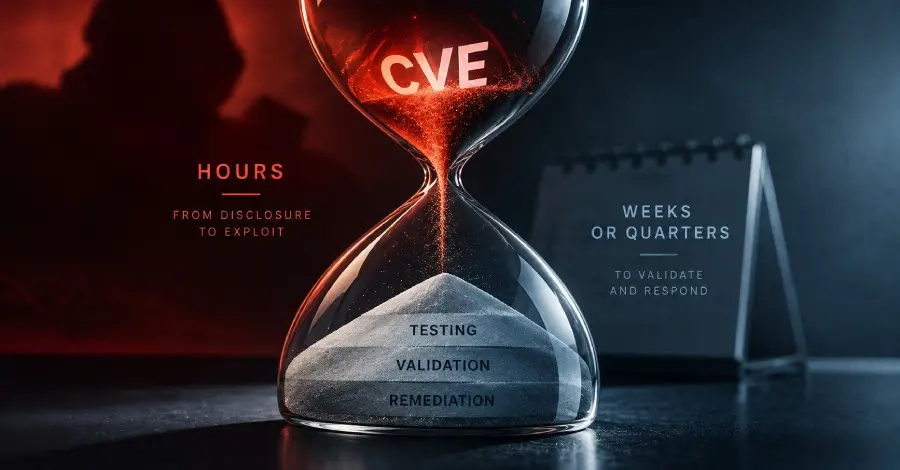
This shift in methodology is the focal point of an upcoming industry discussion led by Ishak Celikkanat, Solutions Architect Lead at Picus. In a scheduled live session titled "How to Prove You’re Ready for Mythos-Class Attacks," Celikkanat intends to demonstrate a modernized CVE-to-validation workflow. The core objective of this approach is to provide security teams with the tools to replace assumptions with defensible, data-driven answers while a vulnerability finding is still relevant.
The transition to this model involves moving beyond the "scan and patch" mentality. Instead, it encourages a "validate and mitigate" approach. By simulating the behaviors an attacker would use to exploit a specific CVE, organizations can gain a clear picture of their actual exposure. This process allows teams to see exactly where their defenses hold firm and where they crumble, enabling them to direct their limited resources toward the most impactful remediation efforts.

The Challenge of Testing in Production
One of the most significant hurdles to effective vulnerability validation has historically been the risk associated with testing. Production environments are the lifeblood of any enterprise, and running live exploit code against mission-critical systems is often seen as a recipe for disaster. The fear of causing a system crash or data corruption frequently leads security teams to rely on lab environments that may not accurately reflect the complexities of the live network.
However, the methodology being championed by experts like Celikkanat offers a safer alternative. Rather than running the raw, potentially destructive exploit code, teams can map a specific vulnerability to its constituent attack techniques. By understanding the behavioral patterns required to leverage a flaw—such as specific lateral movement tactics, credential harvesting methods, or data exfiltration paths—defenders can validate their security controls against those specific behaviors.
This behavioral validation provides the necessary evidence of readiness without the risks inherent in direct exploitation. It allows a security team to prove that even if a vulnerability exists on a production server, the existing security stack is capable of detecting and blocking the techniques an attacker would need to use to make that vulnerability "useful." This level of insight is crucial for maintaining operational stability while simultaneously hardening the organization’s security posture against Mythos-class threats.
Adapting to a Changing Environment
The reality of modern enterprise infrastructure is one of constant flux. Cloud environments, containerized applications, and remote workforces mean that the perimeter is no longer a fixed line, but a shifting boundary that changes by the hour. If an organization’s security validation process takes weeks to complete, it is essentially providing a snapshot of a world that no longer exists.
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...
 Cybersecurity Basics & Security News
CISA Issues Urgent Warning Over Actively Exploited Ivanti Connect Secure Zero-Day Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a critical advisory...
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...







