
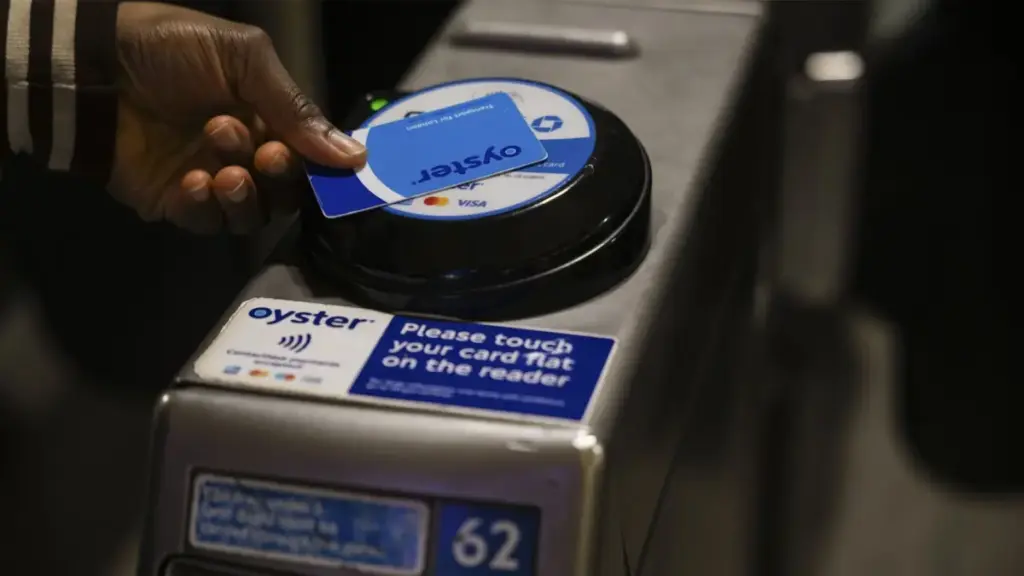
The transport operator now faces the dual challenge of restoring its digital services while rebuilding public trust. The photocard website remains a vital tool for Londoners to manage their travel costs, and its absence creates a logistical hurdle for those needing to renew or apply for concessions. TfL has not yet provided a definitive timeline for when the site will return to full functionality, stating only that the investigation is ongoing.
As the investigation continues, security experts are advising all TfL customers—regardless of whether they have been contacted yet—to remain vigilant. The primary advice involves being skeptical of any unsolicited communications, whether via email, SMS, or telephone, that claim to be from TfL, a bank, or a government agency. Users are also encouraged to update their security questions on other sensitive accounts if they have used the same answers that were registered with their Oyster photocard account.
The Information Commissioner’s Office will likely examine whether TfL’s security measures were commensurate with the sensitivity of the data being held, particularly given the previous breach in 2024. Under UK GDPR, organizations are required to implement appropriate technical and organizational measures to ensure a level of security appropriate to the risk.
For now, the focus remains on containment and communication. As one of the world’s most complex transport networks, TfL is a high-value target for cyber criminals. This latest incident serves as a stark reminder that in the age of digital infrastructure, the security of the data behind the journey is just as critical as the safety of the journey itself.
FOLLOW US ON SOCIAL MEDIA
Follow ITPro on Google News and add us as a preferred source to keep tabs on all our latest news, analysis, views, and reviews.
You can also follow ITPro on LinkedIn, X, Facebook, and BlueSky.
 Helpdesk & IT Service Management (ITSM)
OpenSSF and Tech Giants Call for Sustainable Funding to Secure Global Software Supply Chain
The OpenSSF (Open Source Security Foundation) Governing Board has issued an urgent...
 Helpdesk & IT Service Management (ITSM)
Overe Appoints Former Sophos CSO Simon Reed as Strategic Advisor to Accelerate MSP Security Growth
In a significant move aimed at strengthening its leadership and deepening its...
 Helpdesk & IT Service Management (ITSM)
NetApp Insight 2024: Navigating the Shift Toward AI Inference and Sovereign Data Infrastructure
As the autumn conference season gathers momentum, the technology industry’s focus has...







