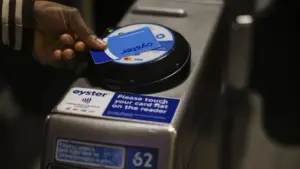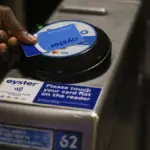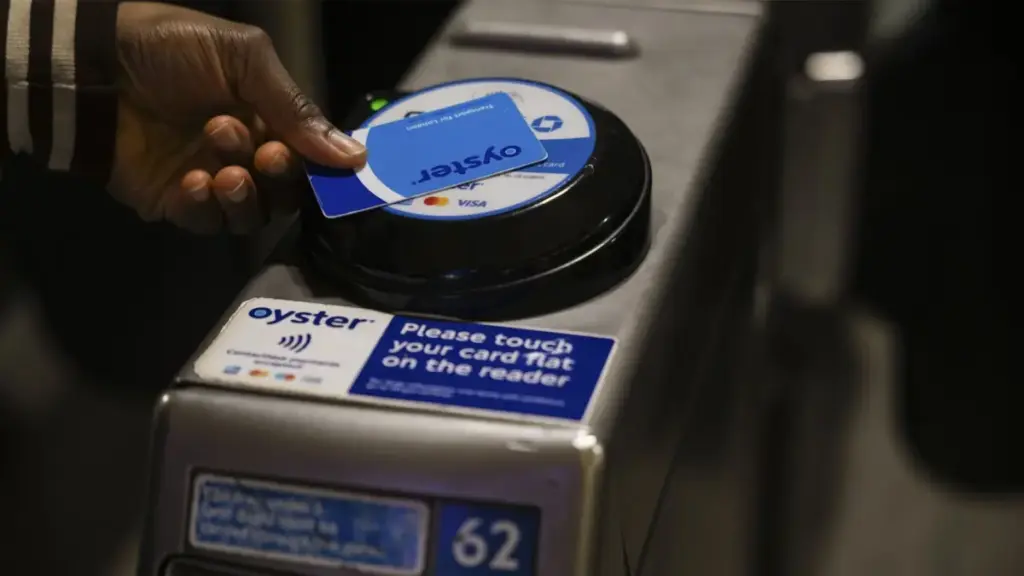
Transport for London (TfL) has confirmed that a significant cyber security incident has resulted in the unauthorized exposure of personal data belonging to more than 260,000 Oyster photocard customers. The breach, which was identified following the detection of suspicious activity within the transport operator’s digital infrastructure, has prompted an immediate investigation and the proactive suspension of several online services to prevent further compromise.
The data exposed in the incident is comprehensive, covering a wide array of personal identifiers that could potentially be leveraged by malicious actors. According to TfL, the compromised information is believed to include the full names of customers, their registered home addresses, contact telephone numbers, dates of birth, and email addresses. Most concerningly for security analysts, the breach also appears to have included the security questions and corresponding answers that users established to protect their accounts.
In the immediate aftermath of the discovery, TfL took the decisive step of taking its photocard web portal offline. This system is the primary interface for thousands of Londoners who rely on specialized travel concessions. The transport body has also initiated a formal notification process, reaching out to the specific individuals whose data was identified in the breach. Furthermore, the incident has been reported to the relevant regulatory authorities, including the Information Commissioner’s Office (ICO), which oversees data protection and privacy standards within the United Kingdom.
Despite the breadth of the personal data involved, TfL has moved to reassure the public regarding financial security. The organization stated that there is currently no evidence to suggest that any banking or payment-related information was accessed or exposed during the breach. Additionally, customer passwords and the digital photographs provided for the Oyster photocards are believed to remain secure, as they are stored using different security protocols.
A Pattern of Vulnerability in London’s Transport Infrastructure
This latest security failure marks the second major data breach for Transport for London in a span of just over two years, raising questions about the long-term cyber resilience of the city’s critical infrastructure. In September 2024, TfL was the target of a massive cyber attack that was significantly larger in scope, with reports indicating that the personal details of up to 10 million people may have been exposed after hackers gained access to a central customer database.
While the current breach involving 260,000 users is smaller in scale than the 2024 incident, the nature of the data stolen presents unique and persistent risks. Shashi Verma, TfL’s director of technology strategy and revenue, emphasized the organization’s rapid response in a statement provided to the media. Verma confirmed that the photocard website was disabled as soon as the anomaly was detected to facilitate a thorough forensic investigation.
"The protection of personal information is a priority for us, and I apologize to our customers affected by this incident," Verma stated, acknowledging the disruption and the potential anxiety caused to the traveling public.
 Helpdesk & IT Service Management (ITSM)
Hammer Distribution and Acronis Announce Strategic UK Partnership to Address Growing MSP Complexity and Cyber Threats
Hammer Distribution has officially announced a significant new strategic partnership with Acronis,...
 Helpdesk & IT Service Management (ITSM)
UK Firms Facing Surge in Agentic AI Security Incidents as ServiceNow Warns of Governance Gap
The rapid integration of autonomous artificial intelligence agents into the corporate ecosystem...
 Helpdesk & IT Service Management (ITSM)
TrendAI Integrates Nvidia Nemotron Models to Strengthen Data Sovereignty for Sovereign and Private Cloud Environments
In a significant move aimed at bridging the gap between cutting-edge generative...