
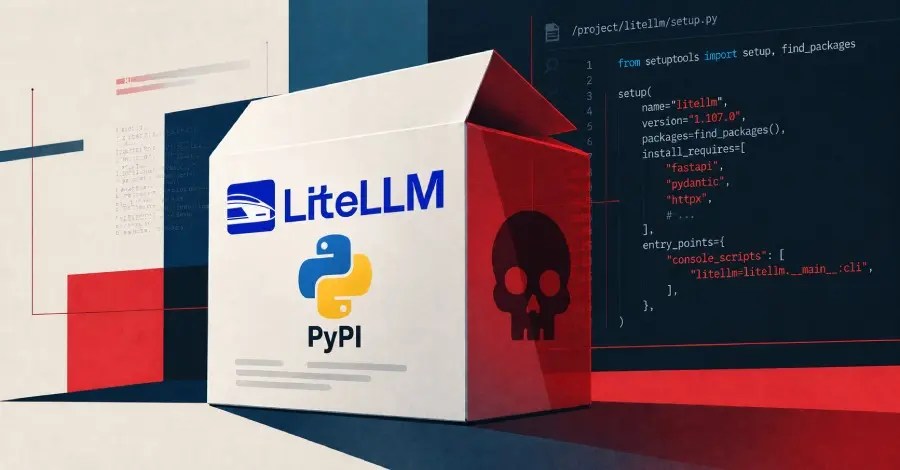
However, in the days leading up to the attack, these restrictions had been temporarily relaxed. The team was in the midst of a push for more frequent releases and bugfix backports, and to facilitate this speed, the protocol was adjusted to allow any two engineers to trigger and approve a release.
The attacker capitalized on this window of opportunity. Using the stolen owner-level credentials, they were able to act as both the initiator and the approver. By repointing the deployment mechanism to a malicious repository under their control, the threat actor successfully triggered the release of LiteLLM version 1.107.0. While the developers noted that the attacker could have used their owner-level access to remove the physical device restriction entirely, it is suspected that they chose to exploit the existing "two-engineer" relaxation to avoid triggering internal alarms.

Forensic Insights: The Hidden Workflows
Subsequent investigations by the application security firm Socket provided deeper insight into how the attacker managed the compromise without leaving a conspicuous trail in the repository’s primary history. Socket’s analysis revealed that the threat actor utilized short-lived branches, named with the prefix "ci-tmp-" followed by a hexadecimal string.
These branches were created, used to run malicious GitHub Actions workflows, and deleted within minutes. This "ephemeral branching" strategy ensured that the activity remained hidden from the repository’s ordinary commit history. Socket recovered two malicious commits made on October 10 and October 12, 2026, which added a workflow file located at .github/workflows/cache.yml.
These workflows were engineered for massive credential exfiltration. The October 10 workflow focused on harvesting GitHub tokens and API keys for the organization’s Linear workspace, Together AI, and the signing keys for a GitHub App. By October 12, the scope of the theft had expanded significantly. The updated workflow was designed to capture API keys for nearly every major AI provider, including OpenAI, Anthropic, and AWS Bedrock, as well as secrets for Tavily and the organization’s GitGuardian tenant.
The inclusion of the GitGuardian API key was particularly tactical. As a secret-scanning platform, GitGuardian is intended to alert developers when credentials are leaked. By compromising this key, the attacker gained visibility into—and potential control over—the very alerts that might have exposed their presence. Furthermore, the attacker exfiltrated "E2E_LINEAR_STORAGE_STATE_B64," which contains serialized browser session data. This allowed the attacker to gain authenticated access to the organization’s Linear account, effectively bypassing multi-factor authentication (MFA).
Anatomy of the Malicious Package
The impact of the breach extended far beyond LiteLLM’s internal systems once version 1.107.0 hit the public Python Package Index (PyPI). Detailed analysis from Microsoft Security Research and other firms revealed that the compromised package was designed to be exceptionally invasive.
 Cybersecurity Basics & Security News
Google Pixel 10 and Samsung Galaxy S26 Breached as Ikotas Labs Claims Top Honors at Pwn2Own Ireland 2026
The competitive landscape of cybersecurity research reached a fever pitch this week...
 Cybersecurity Basics & Security News
Trezor Issues Urgent Warning Over Hardware Implants Found in Wallets Sold by Southeast Asian Reseller
The cryptocurrency security landscape is facing a significant new challenge as Trezor,...
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...







