
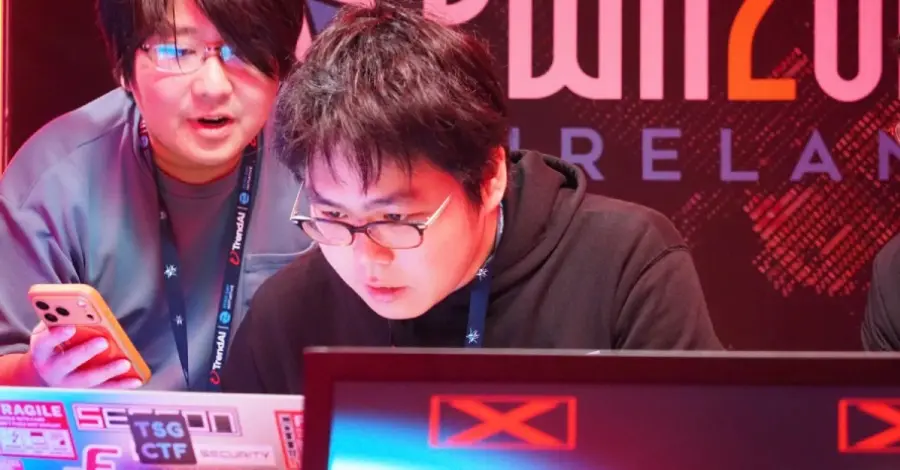
The competitive landscape of cybersecurity research reached a fever pitch this week in Cork, Ireland, as the world’s most elite ethical hackers gathered for Pwn2Own Ireland 2026. Over the course of three days, the event, organized by Trend Micro’s Zero Day Initiative (ZDI), served as a high-stakes proving ground for vulnerability research, with participants targeting everything from flagship smartphones and AI-driven databases to smart home infrastructure. By the conclusion of the event on October 8, 2026, the collective efforts of the research community resulted in more than $1.2 million in awarded prizes, underscoring both the sophistication of modern exploits and the critical importance of the "bug bounty" ecosystem in securing global technology.
The centerpiece of this year’s competition was the successful compromise of the Google Pixel 10, a device marketed for its robust security architecture. Over the course of the event, three separate research teams managed to penetrate the device’s defenses, demonstrating that even the most current, fully patched hardware remains susceptible to advanced attack chains. The most significant of these victories belonged to Ikotas Labs, whose technical prowess not only earned them a $300,000 top prize for their Pixel exploit but also propelled them to the title of "Master of Pwn," the contest’s highest individual honor.
The Breach of the Pixel 10
The rules of Pwn2Own are famously stringent: every target device must be running the most recent firmware and security updates available at the time of the attempt. For the Google Pixel 10, this meant researchers were working against a platform that had received its most recent security bulletin just two days prior, on October 6. Despite these hurdles, the Pixel 10 was successfully exploited three times in the remote attack category, a classification that requires the attacker to gain entry without physical access to the device, typically through web content or wireless radio links such as Wi-Fi, Bluetooth, NFC, or baseband.
The first successful breach was executed by the team known as Xint, comprised of researchers Tim Becker and Yves Bieri. Their attempt was initially met with high anticipation, though the final payout was adjusted to $150,000 and 15 points—exactly half of the maximum possible reward. This reduction was due to what the ZDI calls a "bug collision." In the context of Pwn2Own, a collision occurs when a researcher utilizes a vulnerability that has already been discovered by another party, such as the vendor or the contest organizers themselves. While the exploit remains valid and impressive, the prize is halved to reflect that the bug was not a "zero-day" unknown to the industry.
Following Xint, Ikotas Labs took the stage for their attempt on the Pixel 10. Their performance was a masterclass in exploit engineering, as they successfully chained multiple vulnerabilities together to achieve their objective. Interestingly, while the ZDI’s official results labeled the Ikotas entry as a collision, the team was still awarded the full $300,000 prize and 30 points. The ZDI has not yet provided a detailed explanation for this discrepancy, though it often occurs when a team’s exploit chain includes enough unique or novel elements to justify the full award despite the presence of a known bug within the sequence.

The third successful Pixel exploit was a collaborative effort by Dimitrios Valsamaras, Ken Gannon, and Tenia Valsamara. This team utilized a sophisticated chain of two distinct bugs: one that was identified as a collision and another that was a true zero-day. This hybrid approach earned them $112,500 and 22.5 points. Collectively, the three successful attacks on the Pixel 10 resulted in a total payout of $562,500, a figure that highlights the premium placed on mobile security vulnerabilities in today’s market.
Master of Pwn: The Rise of Ikotas Labs
While the Pixel 10 exploits were the most lucrative, they were only one part of a broader dominant performance by Ikotas Labs. To secure the title of "Master of Pwn," a team must demonstrate versatility across multiple categories of technology. Ikotas Labs did exactly that, proving their capabilities extended far beyond mobile operating systems.
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...
 Cybersecurity Basics & Security News
AI vs. AI: How Researchers Used Claude Opus 5 to Breach OpenAI’s Internal Systems
In a sophisticated demonstration of the "double-edged sword" nature of generative artificial...
 Cybersecurity Basics & Security News
Active Exploitation of Two New Unpatched Zero-Day Vulnerabilities Discovered in Citrix NetScaler Appliances
Security researchers and enterprise IT departments are on high alert following reports...







