
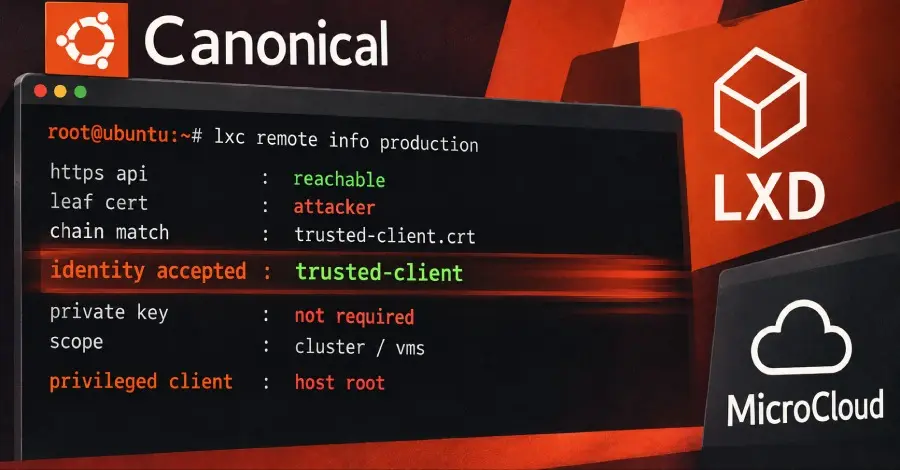
In a significant security development for the Linux container and cloud orchestration ecosystem, Canonical has disclosed a critical vulnerability affecting its LXD and MicroCloud products. The flaw, which has been assigned the highest possible severity rating, could potentially allow a remote attacker to bypass authentication mechanisms and gain full control over host machines. Identified as CVE-2026-112816, the vulnerability carries a maximum CVSS score of 10.0, highlighting the extreme risk it poses to cloud environments and virtualization infrastructure that rely on these technologies.
The vulnerability centers on a failure in how identity is verified during the authentication process. Specifically, the flaw allows an attacker to log into a system as a trusted client without ever possessing that client’s private key. Under normal security protocols, the possession of a private key is the fundamental proof of identity in a cryptographic exchange. By circumventing this requirement, the vulnerability effectively breaks the trust model upon which LXD and MicroCloud rely for secure remote management.
LXD, a powerful system container and virtual machine manager, and MicroCloud, a tool designed to automate the deployment of small-scale clouds, are both widely used in data centers and edge computing environments. Because these tools often manage sensitive workloads and provide deep access to underlying hardware, a vulnerability of this magnitude represents a tier-one security threat for enterprises and developers alike.
How the Flaw Works
To understand the mechanics of CVE-2026-112816, one must look at the implementation of mutual TLS (mTLS) within LXD and MicroCloud. In a standard secure connection, such as a browser visiting a website, the server provides a certificate to prove its identity to the client. In a mutual TLS setup, the process is bidirectional: the client must also present a certificate to the server to prove its identity before access is granted.
LXD and MicroCloud use this mTLS framework to manage remote client access to their APIs. When a client attempts to connect, it presents a certificate chain. The server then checks this certificate against its internal "trust store"—a list of identities and certificates that the administrator has explicitly authorized. If a match is found, the server assumes the client is who they claim to be and grants the appropriate permissions.
The critical failure discovered in these products involves the specific logic used to validate the certificate chain. In a legitimate mTLS handshake, the server must verify that the client owns the private key corresponding to the "leaf" certificate—the very first certificate in the chain. While a client can attach multiple certificates to a chain to show a path of trust back to a root authority, the cryptographic proof of ownership only applies to that initial leaf certificate.
The vulnerability stems from the fact that the affected versions of LXD and MicroCloud were designed to compare every certificate provided in the chain against the trust store. Crucially, the server did not sufficiently verify that the client actually held the private keys for the subsequent certificates in that chain. An attacker could therefore craft a connection where they present their own certificate as the leaf, but then append the public certificate of a highly privileged, trusted client further down the chain.

Because public certificates are, by their nature, not secret information, an attacker could easily obtain the public certificate of a known administrator or a trusted cluster member. By simply attaching this public certificate to their own connection attempt, the attacker could trick the server’s validation logic. The server, seeing a trusted certificate anywhere in the chain, would incorrectly validate the entire connection and treat the attacker as the trusted entity.
 Cybersecurity Basics & Security News
Critical OpenAI Vulnerability Allowed Attackers to Hijack ChatGPT Sessions via Malicious Shared Links
In a significant discovery for the landscape of artificial intelligence security, researchers...
 Cybersecurity Basics & Security News
CISA Issues Urgent Warning Over Actively Exploited Ivanti Connect Secure Zero-Day Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a critical advisory...
 Cybersecurity Basics & Security News
Bridging the Security Gap: Why Modern Enterprises are Moving Beyond Traditional Vulnerability Management
In the rapidly evolving landscape of cybersecurity, a critical finding can traverse...







