
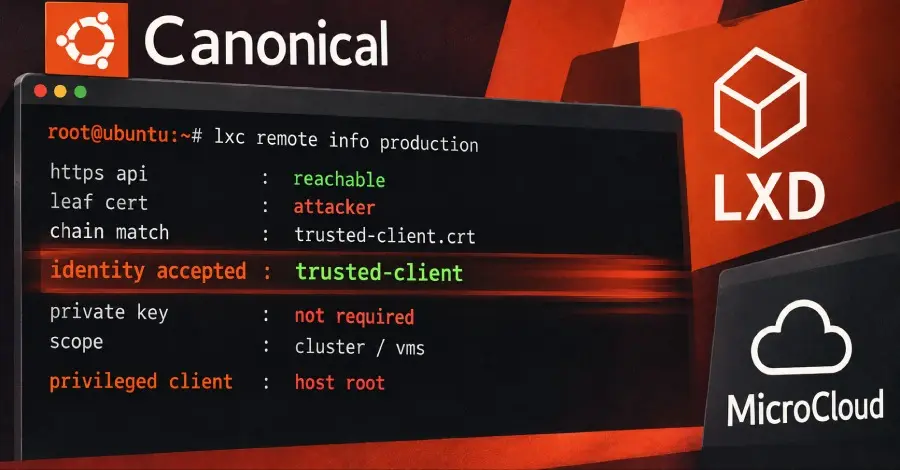
The Impact of Impersonation
The consequences of this flaw are severe. Once an attacker successfully impersonates a trusted client, they inherit all the permissions and access rights associated with that identity. In the context of LXD and MicroCloud, this means the attacker gains the ability to manage the entire cluster, manipulate virtual machines, and access sensitive data stored within containers.
The level of access depends on the privileges of the account being impersonated. If the attacker manages to impersonate a client with administrative or "privileged" status, the breach extends beyond the virtualization layer. Canonical has warned that in such scenarios, an attacker could gain root access to the host machine itself. Root access is the highest level of permission on a Linux system, allowing an intruder to modify the operating system, install persistent malware, intercept network traffic, or move laterally through the internal network to compromise other systems.
In a MicroCloud environment, the risk is compounded by the integrated nature of the cluster. MicroCloud is designed to tie several machines running LXD into a single, cohesive unit. Canonical noted a specific weak point in how new members join these clusters. If an attacker is positioned to capture a member’s public certificate as it is being exchanged during the initial cluster joining process, they can immediately use that certificate to log in as a legitimate member of the cloud infrastructure.
Discovery and Affected Versions
The origins of this bug were not found within Canonical’s internal development team, but rather through the broader open-source ecosystem. The Incus project, which began as a community-led fork of LXD following Canonical’s decision to change the project’s licensing and governance, originally discovered and reported the issue. Upon receiving the report, Canonical investigated its own codebase and confirmed that the vulnerability was present in LXD and MicroCloud.
This cross-project discovery highlights the interconnected nature of modern software development. Because Incus and LXD share a common ancestral codebase, security researchers working on the community fork were able to identify a deep-seated logic error that had persisted in both versions of the software.
The vulnerability affects several long-term support (LTS) and feature releases of LXD. Specifically, the CVE record identifies LXD versions 4.0.14, 5.0.10, 5.21.8, and 6.9 as being vulnerable. For MicroCloud, the flaw was present in versions prior to the latest security updates. Canonical has moved quickly to release fixed versions across all supported branches to ensure that users can secure their environments regardless of which specific release track they are following.
For users running LXD via the Snap packaging system, which is the standard distribution method for the software on Ubuntu and other Linux distributions, the following fixed versions have been made available:
 Cybersecurity Basics & Security News
Active Exploitation of Two New Unpatched Zero-Day Vulnerabilities Discovered in Citrix NetScaler Appliances
Security researchers and enterprise IT departments are on high alert following reports...
 Cybersecurity Basics & Security News
OpenSSH "SSHole" Vulnerability and the Persistence of Simple Misconfigurations Lead Weekly Cybersecurity Briefing
The cybersecurity landscape in late 2026 continues to demonstrate a paradoxical truth:...
 Cybersecurity Basics & Security News
Microsoft Addresses Critical Remote Code Execution Vulnerability in Windows Paint via Microsoft Store Update
Microsoft has officially released a definitive patch for CVE-2026-83844, a significant remote...







