
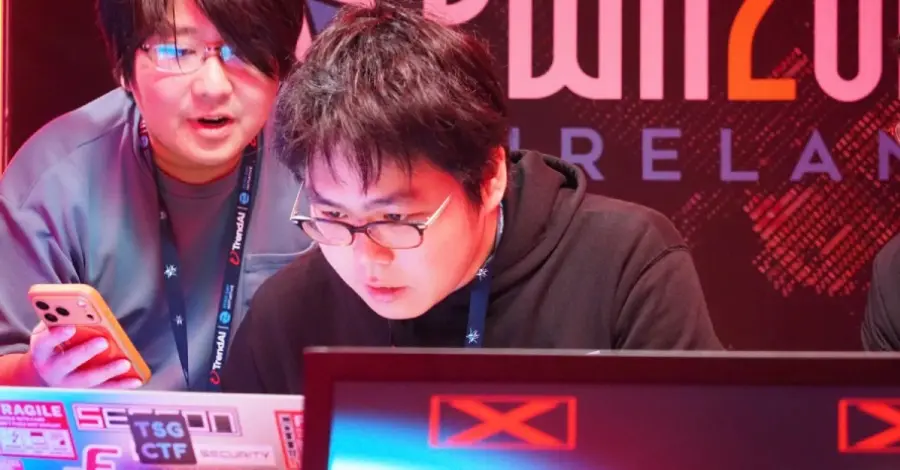
As of the conclusion of the contest, Google’s most recent security bulletin for the Pixel did not include fixes for the vulnerabilities demonstrated in Cork. This is expected, given that the exploits were revealed just as the bulletin was being finalized or released. Consequently, there are currently no specific steps for Pixel 10 or Galaxy S26 owners to take, other than the standard recommendation to keep their devices updated to the latest available security patch level.
A Broad Spectrum of Targets
While smartphones and AI systems dominated the headlines, Pwn2Own Ireland 2026 also featured a diverse array of "Internet of Things" (IoT) and office equipment targets. The ubiquity of these devices in both homes and corporate environments makes them attractive targets for hackers seeking a foothold in a network.
Researchers successfully demonstrated exploits against printers from Lexmark, Canon, and Brother, proving that these often-overlooked devices remain a viable entry point for attackers. The smart home category also saw significant activity, with successful breaches of the Sonos Era 300 smart speaker, the Philips Hue Bridge Pro, and the Home Assistant Green hub. Even wellness technology was not immune; the Garmin Index BPM, a smart blood pressure monitor, was successfully exploited during the event.

The statistical breakdown of the contest illustrates the high level of preparation among the participants. Out of 63 scheduled attempts across all categories, 51 were successful. Interestingly, some of the most high-profile targets on the schedule saw no action at all. There were no registered attempts to exploit Apple’s iPhone 17 or the WhatsApp messaging platform, both of which carried top prizes of $300,000. The absence of attempts on these targets often suggests that the research required to breach them is so intensive—or the value of the exploit on the private market is so high—that researchers may choose not to reveal their findings in a public forum.
Contextualizing the Current Threat Landscape
The events in Cork take place against a backdrop of increasing urgency in mobile security. Just last month, Google was forced to rush out a patch for a critical flaw in the Pixel’s modem (CVE-2026-58704) after reports surfaced that it was being targeted in limited, real-world attacks. That specific flaw allowed for remote exploitation, similar to the categories contested at Pwn2Own.
The fact that three teams were able to find entirely new (or partially new) ways to compromise the Pixel 10 so soon after such a significant patch underscores the "cat-and-mouse" nature of cybersecurity. As manufacturers introduce new hardware features and more complex software layers, the attack surface inevitably expands.
Pwn2Own Ireland 2026 has once again demonstrated that no device is truly "unhackable." However, by incentivizing the world’s best researchers to disclose their findings to vendors rather than selling them to malicious actors, the contest plays a vital role in the global effort to harden the technology that billions of people rely on every day. For now, the industry waits for the 90-day clock to tick down, at which point the lessons learned in Cork will become part of the foundational knowledge used to build the next generation of secure systems.
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...
 Cybersecurity Basics & Security News
Active Exploitation of Two New Unpatched Zero-Day Vulnerabilities Discovered in Citrix NetScaler Appliances
Security researchers and enterprise IT departments are on high alert following reports...
 Cybersecurity Basics & Security News
Critical Vulnerability in Elementor Plugin Leaves Two Million WordPress Sites Open to Full Takeover
A high-severity security flaw has been identified in Elementor, the most widely...







