
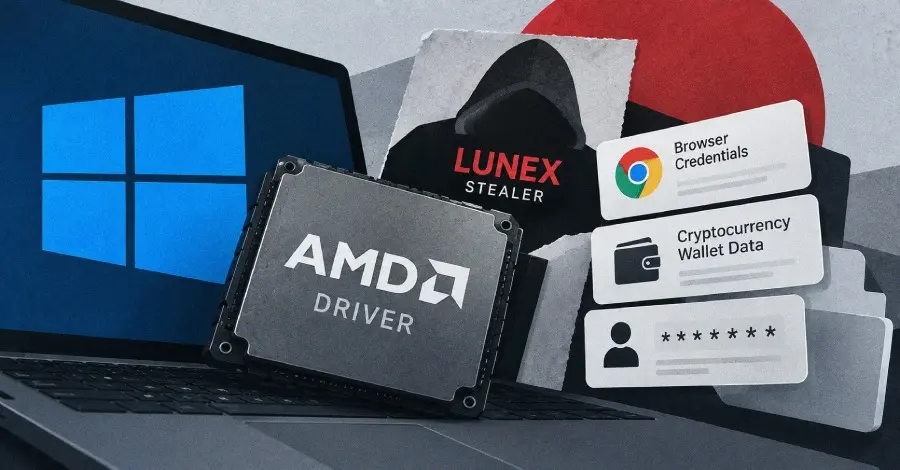
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service (MaaS) platform known as Lunex, which has recently been identified as the engine behind a series of targeted attacks against Ukrainian users. According to new research, the platform is being used to deploy a potent information-stealing component dubbed "Psychedelic Stealer." The operation utilizes a complex, multi-stage infection chain that leverages compromised legitimate websites, social engineering lures, and advanced evasion techniques—including the exploitation of vulnerable kernel-mode drivers—to bypass modern security defenses and maintain a persistent foothold on victim systems.
The discovery of this activity comes from the threat intelligence firm Ontinue, which recently published a detailed technical analysis of the Lunex ecosystem. Researchers described the campaign as a meticulously orchestrated four-stage attack chain designed to deceive users and neutralize Endpoint Detection and Response (EDR) solutions before the final payload is ever delivered. This methodical approach highlights a growing trend in the cybercriminal underworld where traditionally "noisy" malware, such as information stealers, is being paired with sophisticated delivery mechanisms usually reserved for high-level espionage or ransomware operations.
The initial point of compromise typically involves legitimate Ukrainian websites that have been breached by threat actors. These sites—ranging from those of hair-treatment clinics and scale-model manufacturers to tool retailers and psychological facilities—are injected with malicious iframe elements. These iframes serve a "ClickFix" style lure, a social engineering tactic that mimics legitimate browser or security verification checks. Specifically, users are presented with a fake CAPTCHA or a fraudulent Cloudflare verification page. These pages are designed to trick the visitor into performing an action, such as downloading and running a file, under the guise of proving they are not a bot.

Rhys Downing, a threat researcher at Ontinue, noted that the attack chain begins with this fake CAPTCHA page and culminates in the deployment of a fully-featured command-and-control (C2) agent. Once a user is lured into interacting with the fraudulent page, they are typically prompted to download a bogus MSI installer. This installer acts as the gateway for the subsequent stages of the infection. The use of the ClickFix lure is particularly effective because it capitalizes on the habitual nature of web browsing, where users are accustomed to seeing and interacting with verification prompts to access content.
The second stage of the attack involves a loader known as LunexLoader. This component is responsible for preparing the victim’s environment for the stealer and ensuring that the malware can operate with the necessary permissions. To achieve this, LunexLoader utilizes a sophisticated bypass for Windows User Account Control (UAC). By leveraging the CMSTPLUA COM object—a well-known but still effective technique for privilege escalation—the loader can execute commands with elevated rights without triggering the standard Windows prompt that would otherwise alert a vigilant user.
Perhaps the most significant aspect of the Lunex infection chain is its use of a "Bring Your Own Vulnerable Driver" (BYOVD) attack for defense evasion. This technique involves the malware purposely installing a legitimate but known-vulnerable kernel-mode driver onto the victim’s system. In this specific campaign, Lunex takes advantage of an AMD Radeon Software driver, identified as "PDFWKRNL.sys." This driver is susceptible to CVE-2023-20598, a vulnerability that allows for privilege escalation and the manipulation of system processes at the kernel level.
 Cybersecurity Basics & Security News
ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group Members
Khader, who also operated under the moniker ReyXBF, is far from an...
 Cybersecurity Basics & Security News
The Evolution of the Vulnerability Gap: Defending Against the Rise of Mythos-Class AI Attacks
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities...
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...






