
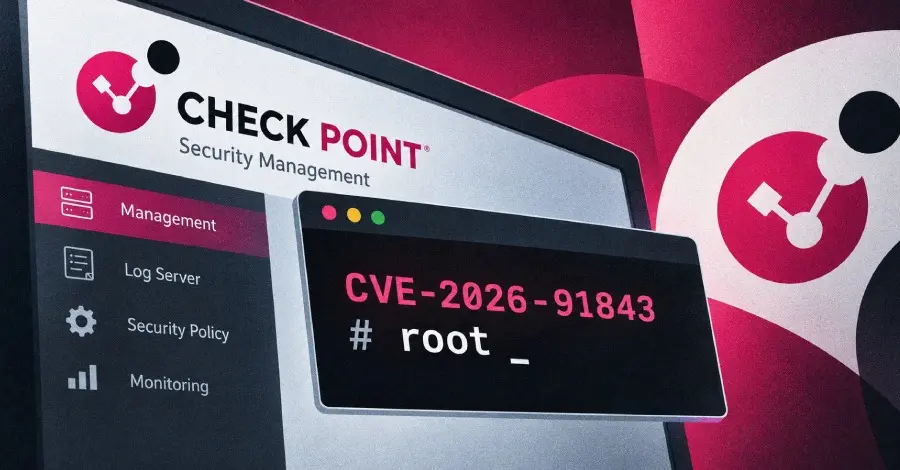
A severe security vulnerability has been identified within Check Point’s Security Management and Log Servers, presenting a significant risk to enterprise network infrastructures worldwide. The flaw, which allows an unauthenticated attacker to execute arbitrary code with root-level privileges over a network, has sent ripples through the cybersecurity community due to the central role these servers play in maintaining organizational security posture. Because the Security Management Server acts as the central nervous system for firewall policies and administrative access, a compromise at this level could grant an adversary total control over an organization’s network defenses.
Check Point has moved quickly to address the issue, deploying a fix through its specialized LivePatch update channel. While the company maintains that there is currently no evidence of the vulnerability being exploited in the wild, the technical nature of the flaw and its potential for high-impact exploitation have prompted urgent warnings from both the vendor and independent security researchers. The vulnerability is particularly dangerous because it does not require an attacker to possess valid login credentials, significantly lowering the barrier for a successful breach.
The Mechanics of the Stack Overflow
Tracked as CVE-2026-91843, the vulnerability has been assigned a near-perfect Critical severity rating of 9.8 out of 10 on the Common Vulnerability Scoring System (CVSS) scale. At its core, the flaw is a stack-based buffer overflow located within the server’s login process. This specific component is responsible for handling incoming connection requests before a user is even authenticated, meaning the vulnerable code is exposed to any entity capable of reaching the server over the network.
According to technical analysis provided by the internet scanning and threat intelligence firm Censys, the overflow is triggered by a specially crafted login request. Specifically, the vulnerability resides in how the system processes the username field; if a request carries an excessively long username string, it can overwhelm the allocated memory space on the stack, allowing for the injection and execution of malicious code. Because the login process on these systems typically runs with high privileges, a successful exploit grants the attacker "root" access—the highest level of administrative control—allowing them to modify system files, intercept logs, or pivot deeper into the internal network.
Check Point’s internal investigations, later confirmed in communications with industry analysts, revealed that the vulnerable execution path is only accessible through the "Trusted Clients" configuration. This setting is a fundamental security feature in the Check Point ecosystem, designed to restrict which specific hosts or IP addresses are permitted to connect to the management server via the SmartConsole administrative interface. However, if this setting is configured too broadly, or if an attacker can spoof a trusted IP, the path to exploitation remains open.

Affected Versions and System Architectures
The scope of CVE-2026-91843 is extensive, covering several generations of Check Point’s software. The company’s official CVE record indicates that multiple branches of the software are affected, categorized by their "Jumbo Hotfix Take" levels—a numbering system Check Point uses to identify cumulative update packages. Administrators are advised that any server running on a listed branch at or below the specified Take level is considered vulnerable and requires immediate attention.
One notable point of concern involves the R82.20 branch. While early versions of the CVE record did not explicitly list this version, Aviv Abramovich, Check Point’s Vice President of Product Management for Network Security, has confirmed that R82.20 is indeed vulnerable. Independent research from Censys further suggests that every current build of R82.20 is affected, noting that as of the initial disclosure, no Jumbo Hotfix had yet been released to protect that specific branch, leaving administrators reliant on the LivePatch system or manual mitigations.
 Cybersecurity Basics & Security News
OpenAI Dismisses Safety Researchers Following Leak of Confidential Infrastructure Data Amid Growing Security Concerns
OpenAI has terminated the employment of three prominent members of its safety...
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...
 Cybersecurity Basics & Security News
The Evolution of the Digital Frontier: How AI and Cloud Expansion are Redefining Modern Cybersecurity Strategy
The global cybersecurity landscape is currently undergoing a fundamental transformation, driven by...







