
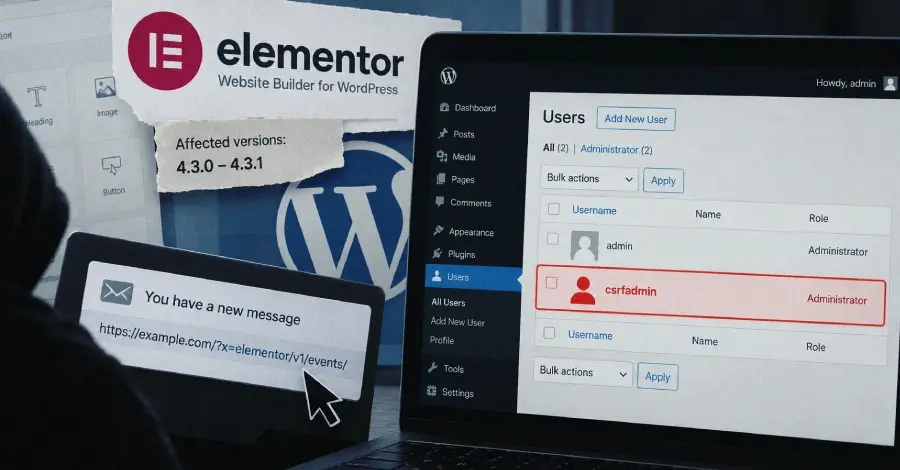
A high-severity security flaw has been identified in Elementor, the most widely used website builder plugin for the WordPress ecosystem, which could allow unauthenticated attackers to gain full administrative control over affected websites. The vulnerability, characterized as a cross-site request forgery (CSRF) bypass, resides in the way the plugin handles internal communication via the WordPress REST API. Security researchers have warned that the flaw is particularly dangerous because it does not require an attacker to have any prior access to the target site, nor does it rely on complex scripts or sophisticated social engineering. Instead, a single malicious link, if clicked by a logged-in administrator, is sufficient to trigger the creation of a new, rogue administrator account controlled by the threat actor.
The issue specifically impacts versions 4.3.0 and 4.3.1 of the Elementor plugin. While Elementor is currently active on more than 10 million WordPress websites worldwide, data from the official WordPress.org plugin repository indicates that these two specific versions alone have been deployed on more than 2 million sites. This massive install base makes the vulnerability a significant concern for the broader web, as it presents a large-scale opportunity for automated attacks and site hijackings. The flaw has been assigned a CVSS score of 8.8 out of 10.0, reflecting its high severity and the ease with which it can be exploited in real-world scenarios.
Cross-site request forgery is a type of web security vulnerability that allows an attacker to induce users to perform actions that they do not intend to perform. In a typical CSRF attack, the attacker leverages the trust that a web application has in a user’s browser. Because browsers automatically include authentication credentials, such as session cookies, with requests made to a domain, an attacker can craft a malicious request and trick a logged-in user into executing it. In the context of WordPress, this usually means an attacker attempts to force an administrator to change a setting, delete content, or, in the most extreme cases, create a new user account with elevated privileges.
The vulnerability in Elementor was discovered and reported by a security researcher known by the alias "Saggre." The technical details of the flaw, which were subsequently analyzed and published by the WordPress security firm Patchstack, reveal a significant oversight in the plugin’s "Editor Events" module. This module was designed to handle specific events within the Elementor editor interface, but it introduced a logic error that effectively disabled CSRF protections across the entire site’s REST API surface under certain conditions.
According to the technical analysis, the core of the problem lies in how the Editor Events module validates incoming requests. To facilitate its own internal operations, the module was programmed to skip standard CSRF protection—usually enforced via WordPress "nonces" or security tokens—whenever the literal string "elementor/v1/events/" was detected within the request URI. The developers likely intended this as a shortcut to allow specific, harmless editor events to be processed without the overhead of nonce validation. However, the implementation was overly broad. Because the request URI includes the query string, and because an attacker has complete control over the query string when crafting a link, they can simply append that specific string as a dummy parameter to any request.
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...
 Cybersecurity Basics & Security News
ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group Members
Khader, who also operated under the moniker ReyXBF, is far from an...
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...







