
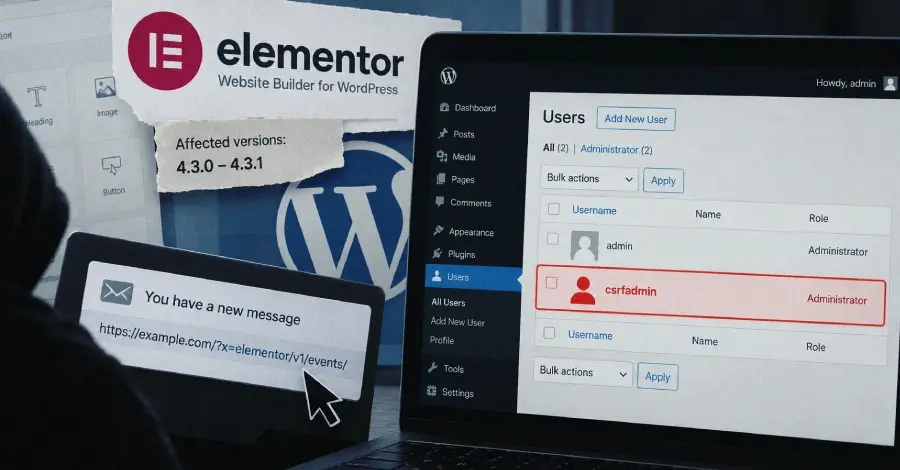
This bypass is not limited to Elementor’s own functions. Because the check occurs at a high level during the REST API initialization, the CSRF protection is waived for the entire REST API infrastructure of the WordPress site. This includes the WordPress core REST API routes and the routes of every other plugin installed on the website. This "universal" bypass turns a plugin-specific bug into a site-wide security failure. An attacker could, for instance, target the standard WordPress core route for user management. By crafting a URL that points to the user creation endpoint and appending the "magic" Elementor string as a query parameter, the attacker can bypass the security checks that would normally block such an unauthorized request.

The mechanics of the attack are strikingly simple. A threat actor could compose a URL that directs a POST request to the WordPress REST API to create a new user with the "administrator" role. By adding a parameter such as "&x=elementor/v1/events/" to the end of the URL, the attacker ensures that the Elementor plugin sees the required string and suppresses the CSRF defense. If an authenticated administrator of a WordPress site clicks this link while logged into their dashboard, their browser will automatically send their session cookies along with the request. The WordPress backend, seeing a valid administrator session and noting that the CSRF protection has been "waived" by the Elementor logic, will process the request and create the attacker’s new account.
Patchstack noted that this attack does not require the attacker to host a malicious website or use complex JavaScript to hide the activity. The link could be delivered through a variety of common communication channels, including email, chat messages, or even as a plain anchor tag in a comment on the target site itself. There is no requirement for a submitted form or any other interactive element; the mere act of the browser attempting to resolve the link while the administrator is authenticated is enough to complete the exploit. This "one-click" nature of the vulnerability significantly lowers the barrier to entry for potential attackers.
The discovery of this flaw highlights the ongoing challenges of securing large-scale plugin ecosystems. Elementor has become an industry standard for WordPress design, powering a significant portion of the modern web. Its modular architecture and extensive feature set provide immense value to users, but also increase the attack surface of any site where it is installed. The Editor Events module, which introduced this specific flaw, was not present in versions of Elementor prior to 4.3.0. This explains why older installations are not affected by this particular bypass, but it also serves as a reminder that new features and updates can inadvertently introduce critical security regressions.
 Cybersecurity Basics & Security News
Cloudflare Resolves Critical Cross-Tenant Data Leakage Flaw in Container Infrastructure
Cloudflare has recently addressed a significant security vulnerability within its containerized infrastructure...
 Cybersecurity Basics & Security News
The Evolution of the Digital Frontier: How AI and Cloud Expansion are Redefining Modern Cybersecurity Strategy
The global cybersecurity landscape is currently undergoing a fundamental transformation, driven by...
 Cybersecurity Basics & Security News
Critical Remote Code Execution Vulnerability Discovered in GitLab AI Gateway
GitLab has issued an urgent security advisory regarding a critical vulnerability discovered...







