
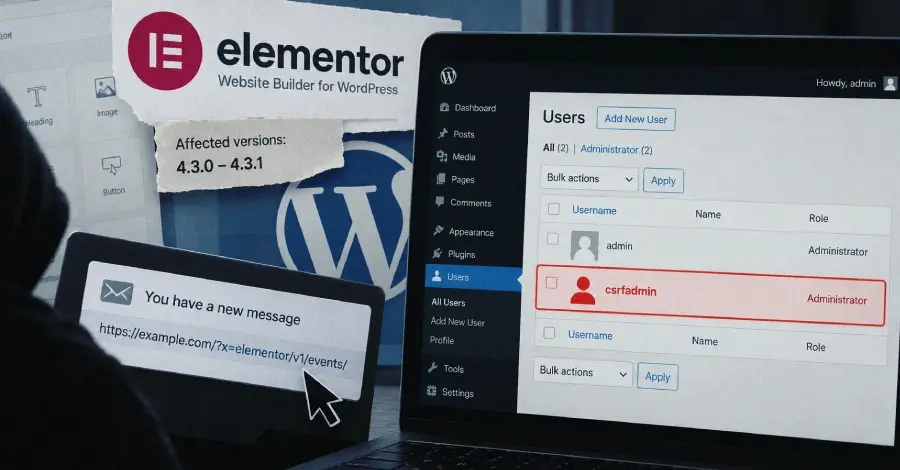
Following the responsible disclosure of the vulnerability by Saggre, the development team at Elementor acted to address the issue. The fix was included in version 4.3.2 of the plugin, which was released earlier this week. The patch involves refining the logic used to identify Editor Events, ensuring that CSRF protection is not erroneously disabled for unrelated REST API requests. Security experts are urging all users of the Elementor plugin to verify their current version and update to 4.3.2 or higher immediately. Given that more than 2 million sites were identified as running the vulnerable versions, the window for exploitation is narrow, and the risk of automated "bot" campaigns scanning for these versions is high.
For administrators of WordPress sites, this incident underscores the importance of rigorous update management and the principle of least privilege. While the CSRF attack requires an administrator to click a link, the potential for harm is magnified when administrative accounts are used for routine tasks. Security professionals often recommend that site owners use lower-privileged accounts for daily content management and only log into administrator accounts when necessary for configuration changes or updates. Furthermore, the use of security plugins that provide additional layers of firewall protection and monitoring can help detect and block suspicious REST API requests before they reach the application logic.
The role of the WordPress REST API has grown significantly in recent years, as more sites move toward "headless" configurations or use dynamic, block-based editors. While the API provides powerful tools for developers, it also necessitates a robust approach to authentication and authorization. The Elementor vulnerability demonstrates how a single line of code intended to simplify a specific internal process can have cascading effects on the security of the entire platform. As the ecosystem continues to evolve, the scrutiny of how plugins interact with core WordPress APIs will remain a critical focus for the security research community.
As of now, there have been no confirmed reports of this vulnerability being exploited in the wild, but the public disclosure of the technical details and the example payload means that the risk is now immediate. The "Saggre" researcher and the team at Patchstack have been credited with identifying the flaw before it could be widely abused by malicious actors. Users who have enabled automatic updates for their plugins may already be protected, but manual verification is strongly advised for any mission-critical website. The vulnerability serves as a potent reminder that even the most trusted and widely used tools in the web development world require constant vigilance and proactive maintenance to remain secure against an ever-shifting threat landscape.
 Cybersecurity Basics & Security News
Critical Cryptographic Flaw in GoBalance Load Balancer Exposes Dark Web Sites to Takeover Attacks
A significant security vulnerability discovered in GoBalance, a specialized load-balancing tool widely...
 Cybersecurity Basics & Security News
CISA Issues Urgent Warning Over Actively Exploited Ivanti Connect Secure Zero-Day Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a critical advisory...
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...







