
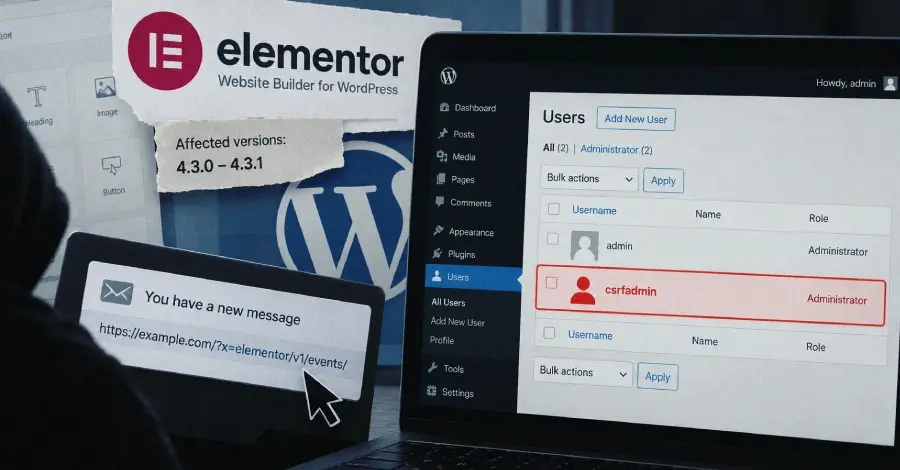
A high-severity security flaw has been identified in Elementor, the most widely used website builder plugin for the WordPress ecosystem, which could allow unauthenticated attackers to gain full administrative control over affected websites. The vulnerability, characterized as a cross-site request forgery (CSRF) bypass, resides in the way the plugin handles internal communication via the WordPress REST API. Security researchers have warned that the flaw is particularly dangerous because it does not require an attacker to have any prior access to the target site, nor does it rely on complex scripts or sophisticated social engineering. Instead, a single malicious link, if clicked by a logged-in administrator, is sufficient to trigger the creation of a new, rogue administrator account controlled by the threat actor.
The issue specifically impacts versions 4.3.0 and 4.3.1 of the Elementor plugin. While Elementor is currently active on more than 10 million WordPress websites worldwide, data from the official WordPress.org plugin repository indicates that these two specific versions alone have been deployed on more than 2 million sites. This massive install base makes the vulnerability a significant concern for the broader web, as it presents a large-scale opportunity for automated attacks and site hijackings. The flaw has been assigned a CVSS score of 8.8 out of 10.0, reflecting its high severity and the ease with which it can be exploited in real-world scenarios.
Cross-site request forgery is a type of web security vulnerability that allows an attacker to induce users to perform actions that they do not intend to perform. In a typical CSRF attack, the attacker leverages the trust that a web application has in a user’s browser. Because browsers automatically include authentication credentials, such as session cookies, with requests made to a domain, an attacker can craft a malicious request and trick a logged-in user into executing it. In the context of WordPress, this usually means an attacker attempts to force an administrator to change a setting, delete content, or, in the most extreme cases, create a new user account with elevated privileges.
The vulnerability in Elementor was discovered and reported by a security researcher known by the alias "Saggre." The technical details of the flaw, which were subsequently analyzed and published by the WordPress security firm Patchstack, reveal a significant oversight in the plugin’s "Editor Events" module. This module was designed to handle specific events within the Elementor editor interface, but it introduced a logic error that effectively disabled CSRF protections across the entire site’s REST API surface under certain conditions.
According to the technical analysis, the core of the problem lies in how the Editor Events module validates incoming requests. To facilitate its own internal operations, the module was programmed to skip standard CSRF protection—usually enforced via WordPress "nonces" or security tokens—whenever the literal string "elementor/v1/events/" was detected within the request URI. The developers likely intended this as a shortcut to allow specific, harmless editor events to be processed without the overhead of nonce validation. However, the implementation was overly broad. Because the request URI includes the query string, and because an attacker has complete control over the query string when crafting a link, they can simply append that specific string as a dummy parameter to any request.
This bypass is not limited to Elementor’s own functions. Because the check occurs at a high level during the REST API initialization, the CSRF protection is waived for the entire REST API infrastructure of the WordPress site. This includes the WordPress core REST API routes and the routes of every other plugin installed on the website. This "universal" bypass turns a plugin-specific bug into a site-wide security failure. An attacker could, for instance, target the standard WordPress core route for user management. By crafting a URL that points to the user creation endpoint and appending the "magic" Elementor string as a query parameter, the attacker can bypass the security checks that would normally block such an unauthorized request.

The mechanics of the attack are strikingly simple. A threat actor could compose a URL that directs a POST request to the WordPress REST API to create a new user with the "administrator" role. By adding a parameter such as "&x=elementor/v1/events/" to the end of the URL, the attacker ensures that the Elementor plugin sees the required string and suppresses the CSRF defense. If an authenticated administrator of a WordPress site clicks this link while logged into their dashboard, their browser will automatically send their session cookies along with the request. The WordPress backend, seeing a valid administrator session and noting that the CSRF protection has been "waived" by the Elementor logic, will process the request and create the attacker’s new account.
Patchstack noted that this attack does not require the attacker to host a malicious website or use complex JavaScript to hide the activity. The link could be delivered through a variety of common communication channels, including email, chat messages, or even as a plain anchor tag in a comment on the target site itself. There is no requirement for a submitted form or any other interactive element; the mere act of the browser attempting to resolve the link while the administrator is authenticated is enough to complete the exploit. This "one-click" nature of the vulnerability significantly lowers the barrier to entry for potential attackers.
The discovery of this flaw highlights the ongoing challenges of securing large-scale plugin ecosystems. Elementor has become an industry standard for WordPress design, powering a significant portion of the modern web. Its modular architecture and extensive feature set provide immense value to users, but also increase the attack surface of any site where it is installed. The Editor Events module, which introduced this specific flaw, was not present in versions of Elementor prior to 4.3.0. This explains why older installations are not affected by this particular bypass, but it also serves as a reminder that new features and updates can inadvertently introduce critical security regressions.
Following the responsible disclosure of the vulnerability by Saggre, the development team at Elementor acted to address the issue. The fix was included in version 4.3.2 of the plugin, which was released earlier this week. The patch involves refining the logic used to identify Editor Events, ensuring that CSRF protection is not erroneously disabled for unrelated REST API requests. Security experts are urging all users of the Elementor plugin to verify their current version and update to 4.3.2 or higher immediately. Given that more than 2 million sites were identified as running the vulnerable versions, the window for exploitation is narrow, and the risk of automated "bot" campaigns scanning for these versions is high.
For administrators of WordPress sites, this incident underscores the importance of rigorous update management and the principle of least privilege. While the CSRF attack requires an administrator to click a link, the potential for harm is magnified when administrative accounts are used for routine tasks. Security professionals often recommend that site owners use lower-privileged accounts for daily content management and only log into administrator accounts when necessary for configuration changes or updates. Furthermore, the use of security plugins that provide additional layers of firewall protection and monitoring can help detect and block suspicious REST API requests before they reach the application logic.
The role of the WordPress REST API has grown significantly in recent years, as more sites move toward "headless" configurations or use dynamic, block-based editors. While the API provides powerful tools for developers, it also necessitates a robust approach to authentication and authorization. The Elementor vulnerability demonstrates how a single line of code intended to simplify a specific internal process can have cascading effects on the security of the entire platform. As the ecosystem continues to evolve, the scrutiny of how plugins interact with core WordPress APIs will remain a critical focus for the security research community.
As of now, there have been no confirmed reports of this vulnerability being exploited in the wild, but the public disclosure of the technical details and the example payload means that the risk is now immediate. The "Saggre" researcher and the team at Patchstack have been credited with identifying the flaw before it could be widely abused by malicious actors. Users who have enabled automatic updates for their plugins may already be protected, but manual verification is strongly advised for any mission-critical website. The vulnerability serves as a potent reminder that even the most trusted and widely used tools in the web development world require constant vigilance and proactive maintenance to remain secure against an ever-shifting threat landscape.
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...
 Cybersecurity Basics & Security News
Advanced Wazza Phishing Kit Leverages Multi-Stage Routing and Device Code Tactics to Target Critical Global Sectors
The landscape of email-based threats is undergoing a fundamental transformation. Phishing kits,...
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...







