
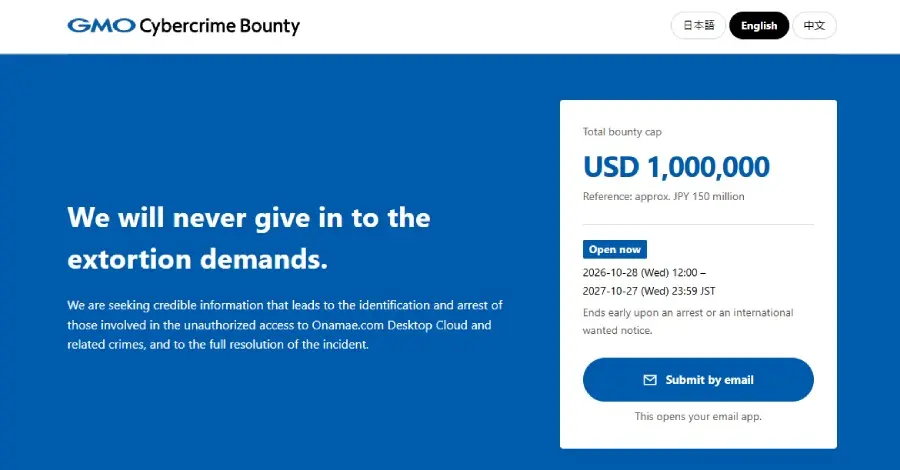
In a decisive counter-offensive against cyber-extortionists, the Japanese technology conglomerate GMO Internet Group has announced a massive financial reward for information leading to the apprehension of those responsible for a recent breach of its Onamae.com Desktop Cloud service. The move comes as a direct response to a staggering $50 million ransom demand, which the company has flatly refused to pay.
The reward program, officially titled the "GMO Cybercrime Bounty," was inaugurated on October 28. Under the terms of the initiative, the group is offering a total of up to $1 million for tips that facilitate the arrest or the issuance of an international wanted notice for the perpetrators. This aggressive stance marks a significant shift in how major Japanese corporations handle high-stakes digital extortion, opting to invest in justice and investigation rather than capitulating to the demands of anonymous attackers.
The breach has specifically targeted the Onamae.com Desktop Cloud, a specialized infrastructure service that provides users with remote Windows desktops. This service is predominantly utilized by foreign exchange (FX) traders who require stable, high-availability environments for automated trading software. The compromise has already had real-world financial consequences, with at least one major broker linking unauthorized trades on customer accounts to credentials exfiltrated from the GMO service.
How the Reward Works
The GMO Cybercrime Bounty is a structured program funded and managed directly by the GMO Internet Group. The company has established a dedicated website to facilitate the secure and, if necessary, anonymous submission of information. To accommodate a global audience of security researchers and whistleblowers, the program accepts tips in three languages: Japanese, English, and Chinese.
The eligibility criteria for the bounty are stringent, designed to ensure that the information provided is of high investigative value. The reward is contingent upon the tip leading directly to a breakthrough in the legal process—specifically, a formal arrest by law enforcement or the issuance of an international wanted notice, such as an Interpol Red Notice. The program is set to remain active until such an arrest occurs, or until October 27, 2027, whichever milestone is reached first.
GMO is actively seeking technical and forensic data that can link specific individuals, servers, or digital assets to the attack. This includes information regarding command-and-control servers, domains, IP addresses, and digital footprints left during the movement of funds, such as cryptocurrency wallet addresses. The company has emphasized that the bounty is intended for actionable intelligence and evidence of criminal methodology; general guesses, unsubstantiated accusations, or the mere reposting of information already available in the public domain will not qualify for payment.
The distribution of the $1 million fund is at the sole discretion of GMO, based on the perceived contribution of the information provided. A single tipster could potentially claim the entire $1 million sum if their information is deemed pivotal, or the total may be divided among multiple contributors. It is a requirement that tipsters prove their identity before any funds are disbursed. Furthermore, the company has clarified that if no submitted tip meets the necessary threshold of utility, no payments will be made.
Strict ethical and legal boundaries have been set for the program. Participation is barred for anyone involved in the original crime, as well as for those who obtained their information through illegal means, such as the purchase of leaked data from the dark web. Employees of the GMO Internet Group are also ineligible. In a stern warning to the public, GMO has instructed potential tipsters not to attempt to breach systems, negotiate with the attackers, or handle stolen credentials and malware in their pursuit of the bounty.

All gathered intelligence is being shared with relevant law enforcement agencies both within Japan and internationally. GMO has already handed over a comprehensive dossier of evidence to the authorities, including detailed communication records from the extortion attempts. To protect participants from phishing, the company has stated it will never request passwords, authentication codes, or administrative fees from tipsters, and all official correspondence will originate from the specific @cybercrimebounty.gmo domain.
 Cybersecurity Basics & Security News
NGINX Issues Critical Security Updates to Address Five Vulnerabilities, Including a Two-Decade-Old Memory Bug
NGINX, the high-performance web server and reverse proxy that powers a vast...
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....
 Cybersecurity Basics & Security News
Critical Memory Corruption Vulnerability in Google’s Brotli Decoder Impacts Node.js, Bun, and Enterprise Infrastructure
A pervasive memory-corruption vulnerability has been identified within Google’s Brotli compression library,...







