
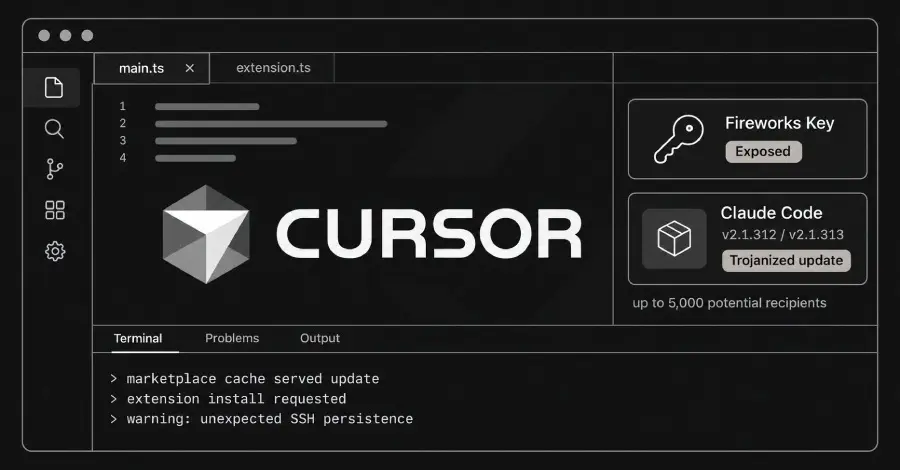
Cursor’s internal monitoring eventually flagged the anomaly, but not before the malicious extension had been available for approximately 11 hours. During this window, the company estimates that at most 5,000 users who requested those specific cached versions potentially received the compromised build.
Upon discovery, Cursor took immediate action to mitigate the threat. The extension marketplace was taken offline to prevent further downloads, and the malicious files were purged from the cache. The company also collaborated with the cloud service provider hosting the attacker’s command-and-control (C2) server to have the infrastructure dismantled. Since November 1, 2026, Cursor reports that no further malicious activity related to this incident has been detected.
Remediation and User Protection
In the wake of the incident, Cursor has implemented a series of aggressive security measures to prevent a recurrence. The company has moved all its inference traffic away from Fireworks AI and deactivated the access key previously issued to the vendor. Furthermore, all access to data sets shared with Fireworks has been terminated.
For the users identified as having downloaded the malicious extension versions, Cursor has issued direct notifications. The company assisted these individuals in revoking any credentials that may have been exposed during the 11-hour window. Additionally, the company performed an extensive sweep to rotate internal credentials and hunt for any signs of deeper persistence within its own production environment.
Importantly, Cursor emphasized that the core components of its service remained secure. There is currently no evidence that the breach impacted:
- Users who had Privacy Mode enabled.
- Customer code repositories hosted on the platform.
- Cursor’s primary production environment.
- The official Cursor application or its primary update channel.
- Other extensions or plugins available on the marketplace.
The company stated that the breach was contained to the specific marketplace cache and the data traces previously shared with the compromised third-party vendor.
Uber and the Widening Impact of the Fireworks Incident
The revelation from Cursor coincides with a broader investigation into the security of Fireworks AI, which appears to have been a central point of failure for multiple high-profile companies. Uber has also confirmed that it was impacted by the same underlying incident at the service provider.

In a filing with the California Attorney General’s office, Uber disclosed that an unauthorized third party had compromised the internal credentials of a service provider on October 9, 2026. While Uber’s public filing did not explicitly name the provider, industry reports and subsequent investigations have linked the breach to Fireworks AI.
 Cybersecurity Basics & Security News
MALFEX Campaign Escalates: New Malicious ‘imgdecode’ Package Discovered Targeting Windows Systems via npm Registry
The landscape of software supply chain security has faced a persistent and...
 Cybersecurity Basics & Security News
AI vs. AI: How Researchers Used Claude Opus 5 to Breach OpenAI’s Internal Systems
In a sophisticated demonstration of the "double-edged sword" nature of generative artificial...
 Cybersecurity Basics & Security News
GMO Internet Group Launches $1 Million Global Bounty After Refusing $50 Million Cyber-Extortion Demand
In a decisive counter-offensive against cyber-extortionists, the Japanese technology conglomerate GMO Internet...







