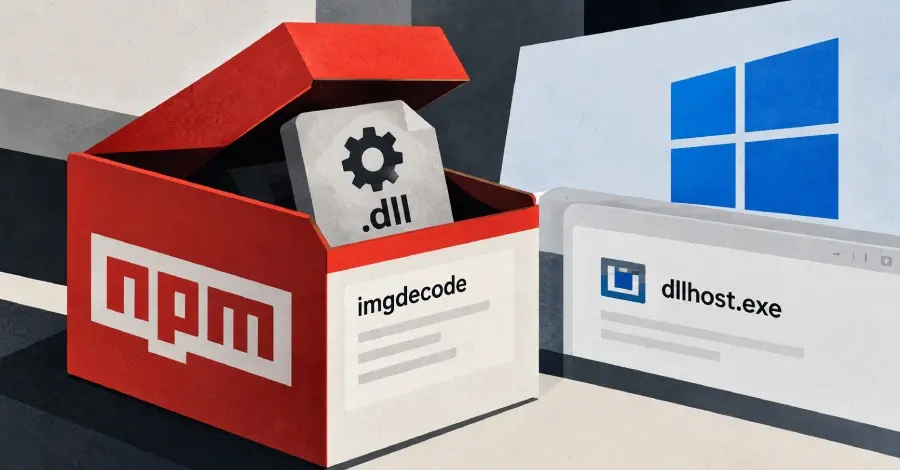
The landscape of software supply chain security has faced a persistent and evolving threat as cybersecurity researchers uncover a sophisticated malware campaign dubbed "MALFEX." This campaign, which has been active for over three years, recently reached a new milestone with the discovery of a malicious npm package named "imgdecode." This latest finding highlights the agility of threat actors who continue to exploit the trust inherent in open-source ecosystems to compromise Windows-based development environments and production systems.
The package in question, "imgdecode," was first identified by security researchers at SafeDep after it was uploaded to the npm registry on September 30, 2026. Attributed to a user account operating under the handle "malfexteste8," the package managed to garner nearly 1,000 downloads—979 at the time of the latest analysis—before its true nature was fully understood by the security community. Despite the identification of its malicious components, the package remained accessible on the registry for a period, highlighting the challenges faced by repository maintainers in policing millions of active packages.
At first glance, "imgdecode" appears to be a legitimate utility for image processing. However, a deep dive into its source code reveals a highly specialized loader designed to bypass traditional security scanners. Unlike many crude malicious packages that rely on obvious post-installation scripts, "imgdecode" utilizes a compiled Node.js native addon to execute its payload. This method is particularly effective because native addons, which are often written in C or C++, are typically distributed as binary files, making them significantly harder for static analysis tools to inspect compared to standard JavaScript files.
The Anatomy of the Attack
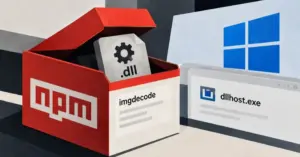
The technical execution of "imgdecode" is a masterclass in minimalist evasion. The package contains a deceptively simple nine-line JavaScript file. When a developer or a Node.js application invokes the command require('imgdecode') on a Windows system, the JavaScript code triggers the loading of a Windows dynamic-link library (DLL). This DLL is the core of the infection mechanism.
Once active within a Windows console environment, the DLL initiates a network request to a GitHub repository to fetch what appears to be an ordinary image file. In reality, this file contains encrypted shellcode. The loader is programmed to decrypt this response in memory and subsequently inject the resulting malicious code into a new "dllhost.exe" process. By choosing "dllhost.exe"—a legitimate Windows system process—the malware effectively masks its presence, blending into the background of standard system operations to avoid detection by basic task monitoring tools.
This discovery is part of a much larger narrative. MALFEX was first documented in detail by security firms Checkmarx and CloudSEK, who identified it as a long-running campaign. The threat actor behind MALFEX has been systematically publishing malicious packages to npm since at least August 6, 2023. These packages have been distributed through a series of interconnected publisher handles, including "malfexkkj," "malfex_user," "malfexteste2," "malfexteste3," and "malfexteste4." The consistent naming convention suggests a single operator or a tightly coordinated group that is undeterred by previous package removals.

Evolution and Adaptability
One of the most concerning aspects of the MALFEX campaign is the speed at which the threat actor adapts to public disclosures. Researchers noted that as soon as security reports were published and packages like "native-runner" or "img-to-native" were removed from the npm registry, the operator responded within 48 hours by publishing functional replacements.
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...
 Cybersecurity Basics & Security News
OpenAI Dismisses Safety Researchers Following Leak of Confidential Infrastructure Data Amid Growing Security Concerns
OpenAI has terminated the employment of three prominent members of its safety...