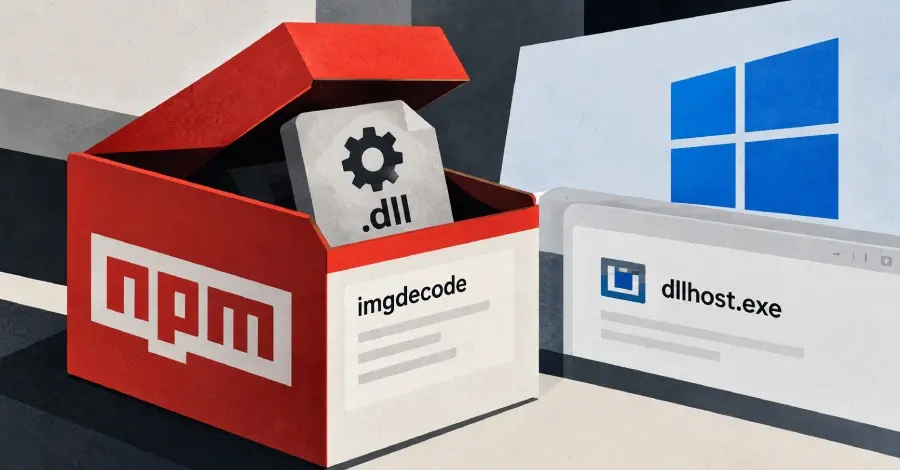
To ensure long-term access, the malware implements persistence by adding a Registry Run key and creating a scheduled task deceptively named "MicrosoftEdgeUpdateService." This ensures that the malicious code is re-executed every time the system boots or at specific intervals, even if the initial process is terminated.
The presence of a .env file within the malicious Node.js application containing a "MALFEX license key" is a particularly telling detail. It suggests that the threat actor may be using a specialized malware builder or that the MALFEX toolset is being operated as a service, potentially sold or licensed to other cybercriminals.
Recommendations for Developers
The discovery of "imgdecode" serves as a stark reminder of the vulnerabilities within the modern development workflow. Security experts advise any developer who has interacted with the aforementioned packages to take immediate action.
Because the malware is designed for persistence and deep system integration, a standard uninstallation of the npm package is insufficient. Affected systems should be treated as fully compromised. Recommended steps include isolating the machine from the network, auditing the Windows Registry and Task Scheduler for unauthorized entries, and performing a clean re-installation of the operating system if possible.
Furthermore, because the MALFEX stealer specifically targets credentials and cryptocurrency wallets, users must rotate all passwords and API keys that were stored on the affected machine. If cryptocurrency seed phrases were accessible to the system, funds should be moved to new, secure wallets immediately.
As the MALFEX campaign continues to evolve, the security community remains on high alert. The transition from simple script-based attacks to sophisticated, native-binary loaders represents a significant escalation in the ongoing battle to secure the global software supply chain. Developers are urged to exercise extreme caution when adding new dependencies to their projects and to utilize tools that can provide deeper visibility into the behavior of third-party packages.
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....
 Cybersecurity Basics & Security News
The Rise of the Personal AI Agent: Navigating the Shift from BYOD to BYOAI in the Corporate Security Landscape
The rollout of personal artificial intelligence agents is proving to be a...
 Cybersecurity Basics & Security News
The Evolution of the Digital Frontier: How AI and Cloud Expansion are Redefining Modern Cybersecurity Strategy
The global cybersecurity landscape is currently undergoing a fundamental transformation, driven by...