
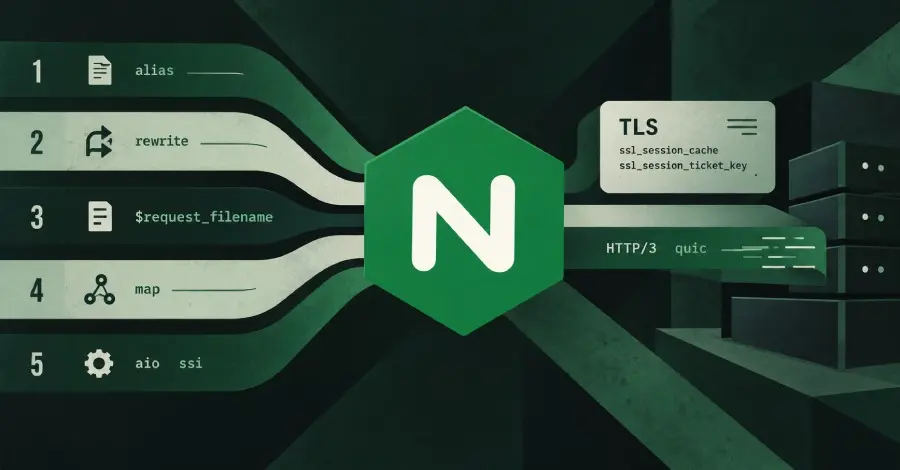
NGINX, the high-performance web server and reverse proxy that powers a vast portion of the modern internet, has released critical security updates to address five distinct vulnerabilities. The updates, which arrived on October 14, target versions 1.30.6 and 1.31.7, resolving issues that range from potential remote code execution to the bypass of client-certificate authentication. Perhaps most notably, one of the addressed flaws has been present in the software’s codebase for nearly twenty years, tracing its origins back to a release in May 2005.
The security advisory, issued by F5—the parent company of NGINX—highlights three memory-related bugs that could lead to worker process crashes or, in more severe scenarios, allow an attacker to execute arbitrary code. While these vulnerabilities are considered critical by F5, they are not universal threats to every NGINX installation. Instead, each requires a specific, often advanced, configuration to be exploitable. This nuance places the burden on system administrators to audit their configuration files to determine their level of exposure.
In addition to the memory-handling flaws, the update addresses a vulnerability in the Transport Layer Security (TLS) implementation that could allow an attacker to forge sessions, potentially bypassing rigorous client-certificate checks. A fifth vulnerability concerns the relatively newer HTTP/3 protocol, where a flaw in request parsing could allow a client to inject additional data into a request before it is passed to a backend server.
As of mid-October, none of these five vulnerabilities have been listed in the Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities catalog. Furthermore, neither NGINX nor F5 has reported any active exploitation in the wild. However, the severity ratings provided by the two entities show a marked difference in perspective. NGINX has classified all five issues as "Medium" severity. In contrast, F5, utilizing the CVSS v4.0 scoring system, has assigned the three memory bugs a "Critical" score of 9.2. The TLS flaw received a score of 8.3, while the HTTP/3 injection bug was rated at 6.9.
The Anatomy of Configuration-Based Exposure
The common thread among these vulnerabilities is their dependency on specific NGINX directives. Unlike "zero-day" exploits that might target a default installation, these flaws lie dormant until a server administrator enables certain features. These features include the use of an alias with a rewrite, regex-based mapping, Asynchronous I/O (AIO) combined with Server Side Includes (SSI), a shared TLS session cache, or the activation of HTTP/3.

The complexity of these configurations varies. For instance, NGINX’s own official documentation suggests the use of a shared session cache and request buffering for optimal performance. Because these are recommended best practices, many high-traffic environments may find themselves inadvertently exposed to the vulnerabilities associated with those specific settings.
 Cybersecurity Basics & Security News
Beyond Policy Intent: Why Identity Visibility Has Become the Critical Frontier in Modern Cybersecurity
In the current landscape of enterprise security, the traditional perimeter has not...
 Cybersecurity Basics & Security News
The Rise of the Personal AI Agent: Navigating the Shift from BYOD to BYOAI in the Corporate Security Landscape
The rollout of personal artificial intelligence agents is proving to be a...
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....







