
NGINX, the high-performance web server and reverse proxy that powers a vast portion of the modern internet, has released critical security updates to address five distinct vulnerabilities. The updates, which arrived on October 14, target versions 1.30.6 and 1.31.7, resolving issues that range from potential remote code execution to the bypass of client-certificate authentication. Perhaps most notably, one of the addressed flaws has been present in the software’s codebase for nearly twenty years, tracing its origins back to a release in May 2005.
The security advisory, issued by F5—the parent company of NGINX—highlights three memory-related bugs that could lead to worker process crashes or, in more severe scenarios, allow an attacker to execute arbitrary code. While these vulnerabilities are considered critical by F5, they are not universal threats to every NGINX installation. Instead, each requires a specific, often advanced, configuration to be exploitable. This nuance places the burden on system administrators to audit their configuration files to determine their level of exposure.
In addition to the memory-handling flaws, the update addresses a vulnerability in the Transport Layer Security (TLS) implementation that could allow an attacker to forge sessions, potentially bypassing rigorous client-certificate checks. A fifth vulnerability concerns the relatively newer HTTP/3 protocol, where a flaw in request parsing could allow a client to inject additional data into a request before it is passed to a backend server.
As of mid-October, none of these five vulnerabilities have been listed in the Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities catalog. Furthermore, neither NGINX nor F5 has reported any active exploitation in the wild. However, the severity ratings provided by the two entities show a marked difference in perspective. NGINX has classified all five issues as "Medium" severity. In contrast, F5, utilizing the CVSS v4.0 scoring system, has assigned the three memory bugs a "Critical" score of 9.2. The TLS flaw received a score of 8.3, while the HTTP/3 injection bug was rated at 6.9.
The Anatomy of Configuration-Based Exposure
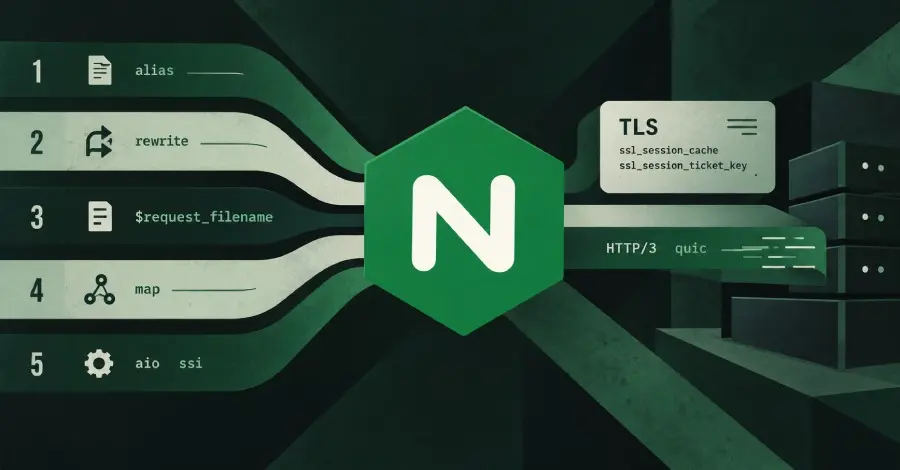
The common thread among these vulnerabilities is their dependency on specific NGINX directives. Unlike "zero-day" exploits that might target a default installation, these flaws lie dormant until a server administrator enables certain features. These features include the use of an alias with a rewrite, regex-based mapping, Asynchronous I/O (AIO) combined with Server Side Includes (SSI), a shared TLS session cache, or the activation of HTTP/3.

The complexity of these configurations varies. For instance, NGINX’s own official documentation suggests the use of a shared session cache and request buffering for optimal performance. Because these are recommended best practices, many high-traffic environments may find themselves inadvertently exposed to the vulnerabilities associated with those specific settings.
The TLS flaw, identified as CVE-2026-97629, is particularly concerning for environments that rely on client-side certificates for identity verification. The bug resides in the mechanism responsible for the automatic rotation of session ticket keys. Session tickets are designed to enhance performance by allowing a client to resume a TLS session without undergoing a full, resource-intensive handshake. Since version 1.23.2, released in late 2022, NGINX has utilized a shared session cache to automatically generate and rotate these ticket keys unless the administrator manually loads them from a file.
The technical failure occurs because each NGINX worker process maintains a copy of three key slots. During the rotation process, the system was found to only correctly copy two of the three slots. This left the third slot containing uninitialized memory—essentially whatever data happened to be in that memory space previously. If an attacker could identify or manipulate a ticket naming that specific slot, the ticket could be verified and decrypted using that "junk" memory material. F5 notes that while this allows for a forged session, the process is "non-deterministic" and largely beyond the direct control of an attacker. Nevertheless, the potential for a bypass of client-certificate verification remains a high-priority concern for secure enterprise perimeters.
A Legacy of Complexity: Memory Overflows and Use-After-Free Flaws
Among the memory bugs, the most historically significant is CVE-2026-15176, a heap overflow vulnerability that has existed in NGINX since version 0.1.29, released in 2005. This flaw is triggered in specific scenarios involving the alias directive and a rewrite that alters the URI. If the configuration also includes directives that read the $request_filename variable—such as return, set, if, or add_header—the system may overflow a buffer when mapping the URI to a physical file path. This occurs specifically when the location’s prefix is longer than the rewritten URI, creating a logic gap in the moment after the URI is changed but before NGINX determines the next processing location.
Another critical memory issue, CVE-2026-97205, involves a "use-after-free" condition. This bug is tied to the use of Asynchronous I/O (AIO) in conjunction with SSI pages that utilize include virtual commands. The technical root of the problem is an 8-bit counter used to track pending asynchronous operations on a request. Because the field is only 8 bits, it can only track up to 255 operations. If 256 operations are pending, the counter wraps back to zero. NGINX may then incorrectly conclude that all operations are complete and free the memory associated with the request, even though active operations are still attempting to access that memory. This leads to memory corruption, potential crashes, and a path toward code execution.
The third memory flaw, CVE-2026-93479, highlights the ongoing challenge of patching complex software. This "map flaw" exists within the string-handling code that NGINX previously patched in July to address a different high-severity vulnerability. According to technical commits, the July patch successfully added protections against certain buffer overruns but inadvertently created a new edge case. While the original patch prevented data from spilling past certain bounds, a subsequent change caused the final string to be sized based on the length of data that had "spilled" into a reserved area. This allowed the final string to outgrow its assigned buffer. This vulnerability is specific to configurations using a regex map where captures are referenced by root or log_format before the map’s output variable is processed.

Protocol Challenges in HTTP/3 and Proactive Mitigation
The vulnerability affecting HTTP/3, CVE-2026-95101, demonstrates the difficulties of implementing emerging protocols. The flaw stems from a parser field that was tasked with two different roles: tracking the remaining length of an unknown frame being skipped and tracking the number of DATA bytes to be passed as part of a request body. When an unknown frame was split across multiple read operations, the system would erroneously treat the leftover count as body data. This data would then be passed to the backend server, effectively bypassing the client_max_body_size check and allowing for the injection of extra bytes into a proxied request.
Given the critical nature of these findings, the recommended course of action for all NGINX users is to upgrade to version 1.30.6 on the stable branch or 1.31.7 on the mainline branch. The stable release is particularly notable as it contains only security and bug fixes, making it a safer choice for production environments that prioritize uptime. NGINX generally only provides fixes for these two active branches. Users on older versions, such as 1.28, will remain vulnerable unless their specific Linux distribution backports the necessary patches to their repository packages.
For organizations that cannot immediately perform an upgrade, F5 has provided several workarounds. These include disabling the alias directive in affected locations, avoiding the use of the $request_filename variable, and switching to named captures in regex maps. For the AIO flaw, administrators are advised to turn off AIO or cease serving SSI pages. The HTTP/3 flaw can be mitigated by setting proxy_request_buffering off, while the TLS session forgery risk can be neutralized by removing the shared cache directive or manually loading session ticket keys from a file using ssl_session_ticket_key.
The urgency of these updates is underscored by the history of NGINX vulnerabilities. Earlier this year, a flaw in the rewrite module (CVE-2026-42945) was exploited in the wild within days of its public disclosure. This latest round of patches represents NGINX’s eighth security release in 2026, reflecting an intensive year for the project’s security maintainers.
The discovery of these flaws involved a collaborative effort between internal F5 researchers and the broader security community. F5 credited Matt Suiche of Tolmo, Mateusz Gierblinski, Hansol Lee of GOTROOT, PhiNode Labs, and a researcher known as Cyberlanc3r for their contributions to identifying these vulnerabilities. In tandem with the core server updates, NGINX also released njs 1.0.2 to address two medium-severity XML-handling flaws in its JavaScript module, further rounding out the security of the NGINX ecosystem.
 Cybersecurity Basics & Security News
The Rise of the Personal AI Agent: Navigating the Shift from BYOD to BYOAI in the Corporate Security Landscape
The rollout of personal artificial intelligence agents is proving to be a...
 Cybersecurity Basics & Security News
AI vs. AI: How Researchers Used Claude Opus 5 to Breach OpenAI’s Internal Systems
In a sophisticated demonstration of the "double-edged sword" nature of generative artificial...
 Cybersecurity Basics & Security News
CISA Issues Urgent Warning Over Actively Exploited Ivanti Connect Secure Zero-Day Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a critical advisory...







