
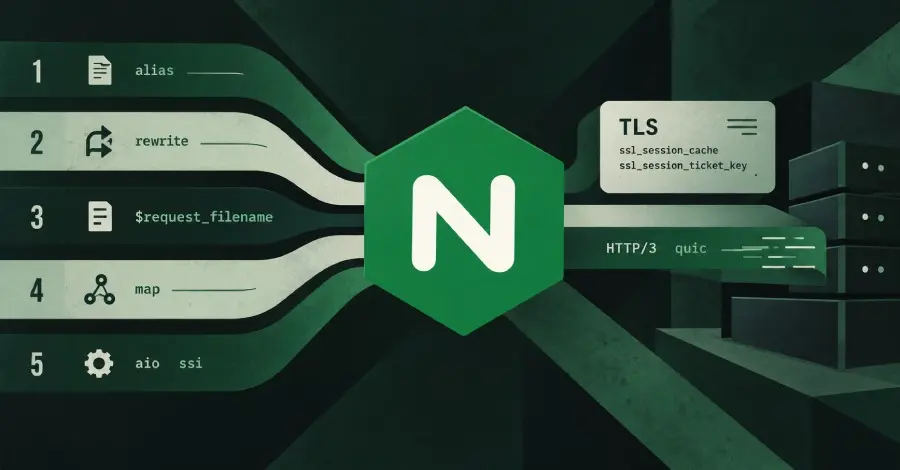
The TLS flaw, identified as CVE-2026-97629, is particularly concerning for environments that rely on client-side certificates for identity verification. The bug resides in the mechanism responsible for the automatic rotation of session ticket keys. Session tickets are designed to enhance performance by allowing a client to resume a TLS session without undergoing a full, resource-intensive handshake. Since version 1.23.2, released in late 2022, NGINX has utilized a shared session cache to automatically generate and rotate these ticket keys unless the administrator manually loads them from a file.
The technical failure occurs because each NGINX worker process maintains a copy of three key slots. During the rotation process, the system was found to only correctly copy two of the three slots. This left the third slot containing uninitialized memory—essentially whatever data happened to be in that memory space previously. If an attacker could identify or manipulate a ticket naming that specific slot, the ticket could be verified and decrypted using that "junk" memory material. F5 notes that while this allows for a forged session, the process is "non-deterministic" and largely beyond the direct control of an attacker. Nevertheless, the potential for a bypass of client-certificate verification remains a high-priority concern for secure enterprise perimeters.
A Legacy of Complexity: Memory Overflows and Use-After-Free Flaws
Among the memory bugs, the most historically significant is CVE-2026-15176, a heap overflow vulnerability that has existed in NGINX since version 0.1.29, released in 2005. This flaw is triggered in specific scenarios involving the alias directive and a rewrite that alters the URI. If the configuration also includes directives that read the $request_filename variable—such as return, set, if, or add_header—the system may overflow a buffer when mapping the URI to a physical file path. This occurs specifically when the location’s prefix is longer than the rewritten URI, creating a logic gap in the moment after the URI is changed but before NGINX determines the next processing location.
Another critical memory issue, CVE-2026-97205, involves a "use-after-free" condition. This bug is tied to the use of Asynchronous I/O (AIO) in conjunction with SSI pages that utilize include virtual commands. The technical root of the problem is an 8-bit counter used to track pending asynchronous operations on a request. Because the field is only 8 bits, it can only track up to 255 operations. If 256 operations are pending, the counter wraps back to zero. NGINX may then incorrectly conclude that all operations are complete and free the memory associated with the request, even though active operations are still attempting to access that memory. This leads to memory corruption, potential crashes, and a path toward code execution.
The third memory flaw, CVE-2026-93479, highlights the ongoing challenge of patching complex software. This "map flaw" exists within the string-handling code that NGINX previously patched in July to address a different high-severity vulnerability. According to technical commits, the July patch successfully added protections against certain buffer overruns but inadvertently created a new edge case. While the original patch prevented data from spilling past certain bounds, a subsequent change caused the final string to be sized based on the length of data that had "spilled" into a reserved area. This allowed the final string to outgrow its assigned buffer. This vulnerability is specific to configurations using a regex map where captures are referenced by root or log_format before the map’s output variable is processed.
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...
 Cybersecurity Basics & Security News
The Evolution of the Vulnerability Gap: Defending Against the Rise of Mythos-Class AI Attacks
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities...
 Cybersecurity Basics & Security News
The Evolution of the Digital Frontier: How AI and Cloud Expansion are Redefining Modern Cybersecurity Strategy
The global cybersecurity landscape is currently undergoing a fundamental transformation, driven by...







