

Protocol Challenges in HTTP/3 and Proactive Mitigation
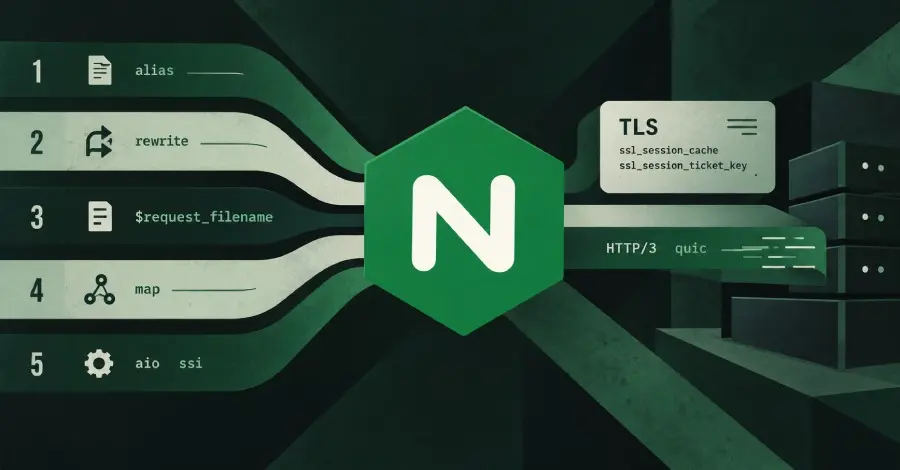
The vulnerability affecting HTTP/3, CVE-2026-95101, demonstrates the difficulties of implementing emerging protocols. The flaw stems from a parser field that was tasked with two different roles: tracking the remaining length of an unknown frame being skipped and tracking the number of DATA bytes to be passed as part of a request body. When an unknown frame was split across multiple read operations, the system would erroneously treat the leftover count as body data. This data would then be passed to the backend server, effectively bypassing the client_max_body_size check and allowing for the injection of extra bytes into a proxied request.
Given the critical nature of these findings, the recommended course of action for all NGINX users is to upgrade to version 1.30.6 on the stable branch or 1.31.7 on the mainline branch. The stable release is particularly notable as it contains only security and bug fixes, making it a safer choice for production environments that prioritize uptime. NGINX generally only provides fixes for these two active branches. Users on older versions, such as 1.28, will remain vulnerable unless their specific Linux distribution backports the necessary patches to their repository packages.
For organizations that cannot immediately perform an upgrade, F5 has provided several workarounds. These include disabling the alias directive in affected locations, avoiding the use of the $request_filename variable, and switching to named captures in regex maps. For the AIO flaw, administrators are advised to turn off AIO or cease serving SSI pages. The HTTP/3 flaw can be mitigated by setting proxy_request_buffering off, while the TLS session forgery risk can be neutralized by removing the shared cache directive or manually loading session ticket keys from a file using ssl_session_ticket_key.
The urgency of these updates is underscored by the history of NGINX vulnerabilities. Earlier this year, a flaw in the rewrite module (CVE-2026-42945) was exploited in the wild within days of its public disclosure. This latest round of patches represents NGINX’s eighth security release in 2026, reflecting an intensive year for the project’s security maintainers.
The discovery of these flaws involved a collaborative effort between internal F5 researchers and the broader security community. F5 credited Matt Suiche of Tolmo, Mateusz Gierblinski, Hansol Lee of GOTROOT, PhiNode Labs, and a researcher known as Cyberlanc3r for their contributions to identifying these vulnerabilities. In tandem with the core server updates, NGINX also released njs 1.0.2 to address two medium-severity XML-handling flaws in its JavaScript module, further rounding out the security of the NGINX ecosystem.
 Cybersecurity Basics & Security News
GitHub Actions Compromised in ‘Mini Shai-Hulud’ Attack Disabled Again Following Brief Reappearance
The cybersecurity landscape has been reminded once again of the persistent and...
 Cybersecurity Basics & Security News
The Evolution of the Vulnerability Gap: Defending Against the Rise of Mythos-Class AI Attacks
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities...
 Cybersecurity Basics & Security News
Cloudflare Resolves Critical Cross-Tenant Data Leakage Flaw in Container Infrastructure
Cloudflare has recently addressed a significant security vulnerability within its containerized infrastructure...






