
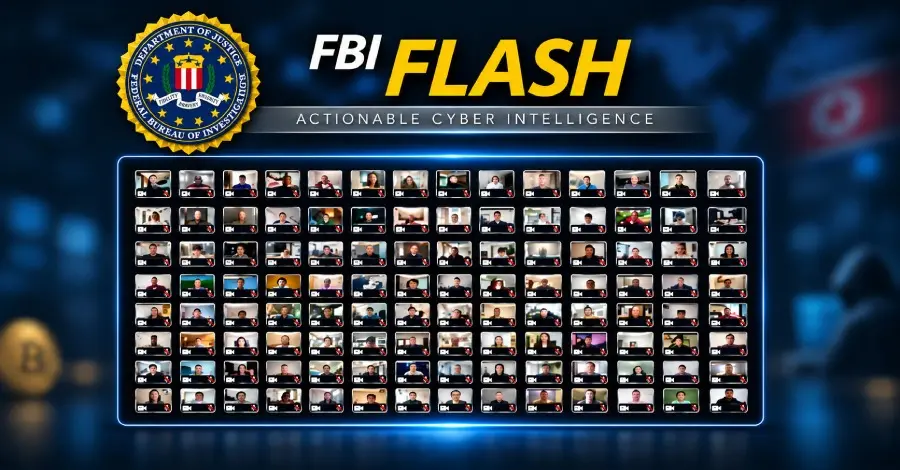
The trap is typically sprung just a few seconds into the meeting. The attackers present a mock technical error, claiming the victim cannot be heard or that there is a synchronization issue. They then provide a link to a "fix"—a classic ClickFix-style lure. In reality, the link is designed to install malware on the victim’s workstation. This malware is capable of not only stealing cryptocurrency and private keys but also leveraging the victim’s authenticated access to compromise broader corporate infrastructure.

This activity overlaps significantly with research published by Kaspersky in October 2025 under the name "GhostCall." Both campaigns highlight the regime’s pivot toward interactive, media-rich social engineering. The FBI’s investigation has linked these efforts to BlueNoroff, a prolific and financially motivated threat cluster also known as APT38, Stardust Chollima, and Sapphire Sleet. BlueNoroff is widely recognized by the international intelligence community as the financial cyber-arm of the Lazarus Group, tasked specifically with generating hard currency for the North Korean state.
Expanding the Target Set: From Executives to Open-Source Developers
While the initial focus of North Korean cyber operations was often large financial institutions, the FaceStealer campaign demonstrates a strategic shift toward the Web3 and software development ecosystems. Data from cybersecurity firm Arctic Wolf indicates that the campaign has targeted over 677 individuals across 58 countries, with a heavy concentration in the United States, Singapore, the United Kingdom, and South Korea.
The victimology is strikingly specific. Approximately 80% of identified targets operate directly within cryptocurrency or blockchain finance. Perhaps more alarming is the focus on leadership; founders and C-suite executives account for nearly half of the target set. By compromising a CEO or a founder, the attackers gain a direct pathway to significant capital, wallet infrastructure, and investment authority.
However, the threat extends beyond immediate financial assets. BlueNoroff has increasingly singled out developers involved in the maintenance of popular open-source software. The goal is to facilitate software supply chain attacks. Earlier this year, the FaceStealer scheme was used to target the maintainer of the Axios npm package, a widely used library in the JavaScript ecosystem. By gaining access to the developer’s workstation, the attackers were able to push a trojanized version of the package that delivered a cross-platform remote access trojan (RAT) to thousands of downstream users.

To maintain the quality of their lures, the threat actors have expanded their reconnaissance. They no longer rely solely on stolen webcam footage. Investigators found that the group scrapes YouTube interviews, conference talks, and social media profiles to capture the likeness and voice of their targets. This allows them to create synthetic meeting footage of high-value individuals—such as a specific CEO—without ever having to compromise that individual directly. This "synthetic reconnaissance" allows for the creation of highly credible lure content that can be reused across multiple targets.
From FaceStealer to Contagious Interview
While FaceStealer focuses on video-based deception, another parallel campaign known as "Contagious Interview" (or "ClickFake Interview") targets the professional recruitment sector. This campaign leverages the global nature of remote work to deceive job seekers and developers.
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...
 Cybersecurity Basics & Security News
Critical WordPress Vulnerability Turns Core Update Process Into Attack Vector
The very mechanism designed to keep millions of websites secure has emerged...







