
In the complex world of medical device procurement and engineering, the presentation of a quality management system certificate is often viewed as a final hurdle cleared. However, for the engineers and quality assurance professionals tasked with ensuring product safety, a certificate is merely the beginning of a much deeper inquiry. As the industry navigates a significant regulatory shift in 2026, the distinction between ISO 13485:2016 and the newly updated ISO 9001:2026 has become more than a matter of administrative preference; it has become a defining factor in a manufacturer’s technical capability.
The dilemma often begins on a procurement officer’s desk. Two potential suppliers submit their credentials. The first holds a current ISO 13485:2016 certification, while the second presents a brand-new ISO 9001:2026 certificate. To the untrained eye, both factories appear equally qualified and "certified." Yet, when a critical design change is implemented on the production line, one of these suppliers will be able to demonstrate exactly what was re-verified and validated, while the other may struggle to provide any objective evidence of the transition. This gap represents the practical reality of the ISO 13485 versus ISO 9001 debate, and it is a gap that a paper certificate alone cannot bridge.
To understand why these two standards lead to such different operational outcomes, one must look past the logos and into the specific capabilities that separate the two systems. These differences are most pronounced in five key areas: design control, risk management, corrective action, traceability, and regulatory evidence.
The Foundational Role of Design Control
The most significant divergence between the two standards lies in design control. Under ISO 13485, design control is a non-negotiable requirement for any organization that takes responsibility for the specification of a medical device. This framework covers the entire lifecycle of a product’s development, including design inputs, outputs, verification, validation, transfer, and change control. In contrast, ISO 9001 allows an organization to exclude design and development from its scope entirely if it only manufactures products based on customer-provided specifications.
This exclusion creates a significant technical risk. Without a formal design baseline, the concepts of "change" and "consistency" have nothing to attach to. If a supplier holding only an ISO 9001 certificate makes a subtle adjustment to a component—such as reducing the wall thickness of a plastic housing to save on material costs—they may remain perfectly consistent with their own internal production standards. Because their quality system may not contain an "approved design" to depart from, they have technically broken no rules. For the buyer, however, this unrecorded change could lead to catastrophic mechanical failure in the field. Design control converts a verbal promise of quality into a comparable, documented reference point. It ensures that every change is a traceable event rather than just another undocumented day on the production floor.
The transition from a prototype to a production-ready unit, known as design transfer, is perhaps the most critical step often overlooked in these discussions. This is the moment where a validated prototype, often built by engineers in a lab setting, becomes a repeatable production process involving specific fixtures, inspection points, and operator instructions. ISO 13485 requires this transfer to be documented and verified. Without this step, a prototype and a production unit are essentially two different products, and the manufacturer has no way of proving that the safety and efficacy of the original design have been preserved during mass production.
Risk Management and the 14971 Standard
While ISO 9001:2026 promotes "risk-based thinking," it does not require a formal risk management file or a specific methodology for assessing product hazards. ISO 13485, however, demands comprehensive risk management throughout the entire product lifecycle. It specifically points toward ISO 14971 as the recognized method for managing risk in medical devices.
In a 13485-compliant system, risk management is not a standalone document kept in a drawer; it is a shared input that informs both the design process and the corrective action system. If a failure occurs, the manufacturer must go back to the risk file to see if that specific failure mode was anticipated. If it was, they must determine if the probability or severity was underestimated. If it wasn’t, the risk file must be updated. This closed-loop system ensures that every failure results in a more robust product, a level of rigor that ISO 9001 does not mandate.
Corrective Action and the Link to Effectiveness
Both standards require a process for corrective action, but the depth of implementation varies significantly. In a general quality system like ISO 9001, a corrective action might be closed once a repair is made or a faulty batch is replaced. ISO 13485 adds two critical layers: a mandatory link to the risk file and a requirement for an effectiveness check.
In the medical device world, a distinction must be made between a "correction" and a "corrective action." A correction fixes the immediate problem—reworking a specific serial number or replacing a broken part. A corrective action, however, fixes the underlying cause to prevent the failure from returning. Under ISO 13485, a corrective action is only considered "closed" when there is objective data proving it worked. This might involve monitoring complaint rates over several months or performing additional sampling. If a file is closed the same week it was opened with a note saying "monitoring ongoing," it fails the 13485 standard for effectiveness.
Traceability and the Recall Boundary

Traceability is often dismissed as mere paperwork until the moment a recall becomes necessary. ISO 13485 requires detailed records that trace products and batches through the entire manufacturing and distribution chain. ISO 9001 requires identification and traceability only "where necessary," often without a strict obligation to track at the batch or serial number level.
The value of this technical capability becomes clear when a defect is discovered in a raw material lot. A supplier with full traceability can identify the specific 100 units that contain the suspect material and issue a targeted recall. A supplier without this capability is faced with a binary choice: recall every unit ever produced or recall nothing. Traceability is what allows a manufacturer to make a technical decision rather than a purely commercial or "honest" one. It keeps the boundary of the affected population clear and defensible.
The Shifting Regulatory Landscape of 2026
The importance of choosing the right standard is underscored by the major regulatory changes taking effect in 2026. One of the most significant developments is the United States FDA’s Quality Management System Regulation (QMSR). Effective February 2026, the QMSR officially incorporates ISO 13485:2016 by reference, replacing much of the old 21 CFR 820 Quality System Regulation. This means that for the first time, the international standard and the U.S. federal regulation share a common base, simplifying compliance for global manufacturers.
Simultaneously, ISO 9001 has entered a transition period. The 2015 edition of ISO 9001 was withdrawn on September 16, 2026, replaced by the ISO 9001:2026 edition. While a three-year transition window exists until September 2029, no new certificates citing the 2015 text can be issued after March 31, 2028. This makes the date and edition on a certificate a vital piece of information. A 2015 certificate may still be valid, but it now carries a known expiry boundary that buyers must monitor.
Interestingly, ISO 13485 has not followed this update cycle. Following a systematic review concluded in 2025, the 2016 edition of ISO 13485 was retained without changes. This stability reflects the standard’s continued effectiveness in meeting the rigorous demands of global medical device regulations, including the EU Medical Device Regulation (MDR).
Practical Evaluation of a Supplier
For an engineer or a buyer, the true test of these systems happens on the factory floor, not in a document review. These capabilities can be tested in an afternoon by asking targeted questions that move beyond the certificate.
When evaluating design control, one should ask to see the last design change on a specific model. A robust system will show a clear chain of evidence: the initial change request, the specific re-verification tests performed after the change, and a drawing revision on the production line that matches the current build. A "bad" answer often involves a disconnect between engineering and production, where drawings in the office do not match the parts being manufactured.
Similarly, when testing traceability, one should pick a random serial number from a shipment sent a year ago and ask to see every incoming raw material lot that went into that unit. A high-functioning ISO 13485 system can chain this data all the way back to the supplier’s lot and the incoming inspection records. In a weaker system, the chain often breaks at the shipment date or relies on paper cards that are not linked to individual serial numbers.
Making the Certification Decision
Ultimately, the choice between ISO 13485 and ISO 9001 depends on the product’s intended use and the regulatory route it follows. If a product is sold as a medical device under the EU MDR or U.S. FDA, ISO 13485 is the standard that matters. While ISO 13485 is technically a voluntary standard, it is the widely accepted route to meeting mandatory government regulations.
For products with no medical claim—such as a standard shower chair sold as a general consumer product—ISO 9001 may be defensible. However, in these cases, the buyer must recognize that the risk of specification conformity and change visibility sits squarely with them. ISO 9001 governs general quality management; it simply does not carry the device-specific obligations required to ensure long-term safety in a medical context.
As the industry moves through 2026 and beyond, the distinction between these two standards will only sharpen. Checking a certificate’s logo is merely checking the cover of a book; the real value lies in the technical capabilities—design control, risk management, and traceability—that the standard mandates within the factory walls. For those responsible for patient safety and product reliability, understanding these differences is not just a matter of compliance, but a fundamental requirement of the profession.
 Software Development & Scripting for IT
The Evolution of Polymorphic Serialization: Why System.Text.Json Offers a Safer Path for Obfuscated .NET Applications
In the landscape of .NET development, maintaining the integrity of serialized data...
 Software Development & Scripting for IT
AI That Urges You to Unplug: Pranav Suryawanshi Unveils TouchCall Voice Assistant for the Hacktoberfest AI Challenge
In an era where digital wellness applications often paradoxically demand more of...
 Software Development & Scripting for IT
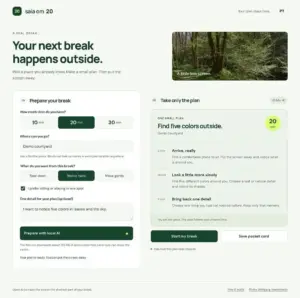
"Outside in 20" Redefines Digital Wellness with Local AI-Driven Outdoor Encouragement
In an era where digital connectivity often feels inescapable, a new open-source...







