
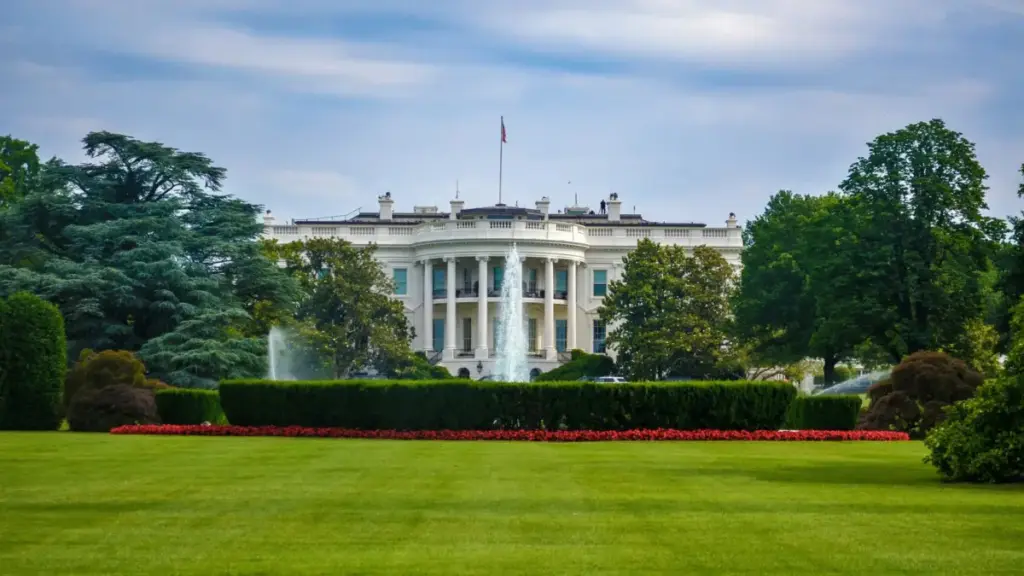
In an era where the digital perimeter of government institutions is under constant scrutiny, a new discovery has raised significant questions regarding the integrity of one of the most secure networks in the world. Recent data indicates that residential proxy software, a tool frequently utilized by cybercriminals to obfuscate their origins and bypass security protocols, has been detected operating within the network infrastructure serving the Executive Office of the President of the United States.
The discovery was made by the Residential Proxy Observatory, a specialized monitoring initiative established by the cybersecurity firm Layer3 Intel. The project was designed specifically to track and analyze the global spread of anonymized network activity, providing a window into how residential IP addresses are being co-opted for various purposes. According to the Observatory’s findings, proxy "exit activity" was identified on a network designated as AS2650. This specific Autonomous System is officially registered to the Executive Office of the President and is the primary network operated out of the White House.
The presence of such software in a high-security environment highlights a growing challenge for federal cybersecurity officials. While the White House is synonymous with some of the most rigorous digital defenses on the planet, the emergence of residential proxies within its internal network suggests that even the most fortified environments are not immune to the pervasive nature of modern anonymization tools.
The Mechanics and Risks of Residential Proxies
To understand the implications of this discovery, it is necessary to examine what residential proxies are and how they function. Unlike traditional data center proxies, which use IP addresses associated with large servers and hosting providers, residential proxies utilize IP addresses assigned by Internet Service Providers (ISPs) to legitimate home users and personal devices. When a user or a piece of software routes traffic through a residential proxy, the resulting internet activity appears to originate from a standard household or a personal mobile device rather than a suspicious server or a known malicious source.
This masking of the true source of internet traffic is a double-edged sword. While the technology itself is not inherently illegal and can be used for legitimate purposes—such as market research, localized content testing, or bypassing censorship in restrictive regimes—it has become a preferred tool for "bad actors." By appearing as a regular home user, cybercriminals can bypass geo-blocking, evade rate-limiting defenses, and carry out large-scale automated attacks without triggering traditional security alarms that often flag data center traffic as suspicious.
The risks associated with these proxies are diverse and significant. They are frequently employed in distributed denial-of-service (DDoS) operations, where a vast network of compromised devices is used to overwhelm a target’s servers. They are also central to the distribution of malware and the execution of credential-stuffing attacks, where hackers attempt to log into various accounts using stolen passwords. Because the traffic originates from a "trusted" residential IP, security systems are less likely to block the requests, allowing the malicious activity to blend in with legitimate web traffic.
A Growing Trend in Enterprise Environments
While the detection of such activity within the White House network is particularly striking, it is not an isolated incident in the broader landscape of corporate and governmental security. The findings from Layer3 Intel align with recent research conducted by Infoblox, a leader in cloud-first networking and security services. Infoblox’s investigations have revealed that residential proxies are increasingly "hiding in plain sight" within major enterprise networks across the globe.
 Small Business IT & Cloud Computing
Microsoft Issues Massive October 2026 Security Update Addressing Record 1,408 Vulnerabilities Amid Active SharePoint Exploits
In an unprecedented move that has sent shockwaves through the cybersecurity and...
 Small Business IT & Cloud Computing
Otter.ai Transitions to Agentic Workflow Automation with New ‘Work’ Mode and Deep Third-Party Integrations
The landscape of workplace productivity is undergoing a fundamental shift as artificial...
 Small Business IT & Cloud Computing
Microsoft Unveils Copilot Workspaces as Strategy Shifts Toward Collaborative, Agent-Led Productivity
At its annual Ignite conference this week, Microsoft signaled a significant evolution...







