
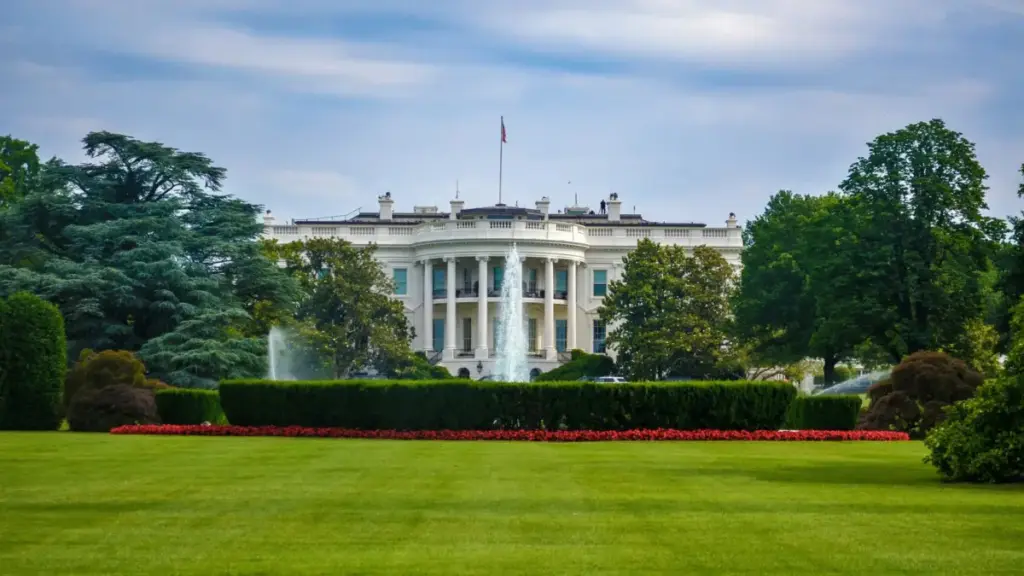
In an era where the digital perimeter of government institutions is under constant scrutiny, a new discovery has raised significant questions regarding the integrity of one of the most secure networks in the world. Recent data indicates that residential proxy software, a tool frequently utilized by cybercriminals to obfuscate their origins and bypass security protocols, has been detected operating within the network infrastructure serving the Executive Office of the President of the United States.
The discovery was made by the Residential Proxy Observatory, a specialized monitoring initiative established by the cybersecurity firm Layer3 Intel. The project was designed specifically to track and analyze the global spread of anonymized network activity, providing a window into how residential IP addresses are being co-opted for various purposes. According to the Observatory’s findings, proxy "exit activity" was identified on a network designated as AS2650. This specific Autonomous System is officially registered to the Executive Office of the President and is the primary network operated out of the White House.
The presence of such software in a high-security environment highlights a growing challenge for federal cybersecurity officials. While the White House is synonymous with some of the most rigorous digital defenses on the planet, the emergence of residential proxies within its internal network suggests that even the most fortified environments are not immune to the pervasive nature of modern anonymization tools.
The Mechanics and Risks of Residential Proxies
To understand the implications of this discovery, it is necessary to examine what residential proxies are and how they function. Unlike traditional data center proxies, which use IP addresses associated with large servers and hosting providers, residential proxies utilize IP addresses assigned by Internet Service Providers (ISPs) to legitimate home users and personal devices. When a user or a piece of software routes traffic through a residential proxy, the resulting internet activity appears to originate from a standard household or a personal mobile device rather than a suspicious server or a known malicious source.
This masking of the true source of internet traffic is a double-edged sword. While the technology itself is not inherently illegal and can be used for legitimate purposes—such as market research, localized content testing, or bypassing censorship in restrictive regimes—it has become a preferred tool for "bad actors." By appearing as a regular home user, cybercriminals can bypass geo-blocking, evade rate-limiting defenses, and carry out large-scale automated attacks without triggering traditional security alarms that often flag data center traffic as suspicious.
The risks associated with these proxies are diverse and significant. They are frequently employed in distributed denial-of-service (DDoS) operations, where a vast network of compromised devices is used to overwhelm a target’s servers. They are also central to the distribution of malware and the execution of credential-stuffing attacks, where hackers attempt to log into various accounts using stolen passwords. Because the traffic originates from a "trusted" residential IP, security systems are less likely to block the requests, allowing the malicious activity to blend in with legitimate web traffic.
A Growing Trend in Enterprise Environments
While the detection of such activity within the White House network is particularly striking, it is not an isolated incident in the broader landscape of corporate and governmental security. The findings from Layer3 Intel align with recent research conducted by Infoblox, a leader in cloud-first networking and security services. Infoblox’s investigations have revealed that residential proxies are increasingly "hiding in plain sight" within major enterprise networks across the globe.
The prevalence of these proxies in professional environments often stems from the proliferation of "shadow IT"—unauthorized software or hardware used by employees without the explicit approval of the organization’s IT department. In many cases, a device becomes a node in a residential proxy network through the installation of seemingly benign software. Some free VPN services, browser extensions, or even "passive income" applications offer their services for free in exchange for the user allowing their device’s idle bandwidth to be used as a proxy exit point.
In an enterprise or government setting, an employee might inadvertently turn a work-issued laptop or a personal device connected to the office Wi-Fi into a proxy gateway. Once this happens, any traffic routed through that device carries the organization’s IP address. If that organization happens to be the Executive Office of the President, the traffic routed through that proxy carries the immense digital reputation and authority of the White House. This makes the "exit point" highly valuable to bad actors, as traffic coming from such a prestigious network is rarely questioned by the destination servers it reaches.
The Global Reach of Network Interference
The discovery by the Residential Proxy Observatory suggests that no location, regardless of its security stature or its geographic isolation, is beyond the reach of these networks. In addition to the activity found within the White House’s AS2650 network, researchers also identified evidence of residential proxy activity on the island of St. Helena.
Located in the South Atlantic Ocean, St. Helena is one of the most remote inhabited places on Earth. The fact that residential proxy software has successfully established a presence there underscores the truly global and ubiquitous nature of this threat. The researchers noted that if these proxies can find their way into the networks of a remote volcanic island and the most protected workspace in the United States, there is effectively "no place on earth to hide" from this form of internet interference.
The St. Helena finding serves as a stark reminder that the infrastructure of the internet is inherently interconnected. A device in a remote location can be co-opted just as easily as one in a major metropolitan hub, provided it has a stable internet connection. For security professionals, this means that the "threat surface" is no longer confined to known high-risk regions; it is everywhere.
Implications for Federal Network Security
The detection of proxy activity within the White House network does not necessarily mean that a malicious "mole" is physically present or that a state-sponsored hack has occurred in the traditional sense. However, it does point to a breach of protocol or a lapse in endpoint security that allowed the software to be activated on a device within the AS2650 infrastructure.
For the Executive Office of the President, the presence of an unauthorized proxy exit point is a serious concern. It implies that a device under their jurisdiction could, in theory, be used to facilitate illicit activities elsewhere on the internet. Whether the software was installed by an unwitting staffer or through more clandestine means, the result is the same: the White House’s network reputation is being leveraged to mask someone else’s digital footprint.
This situation reflects the ongoing battle between network administrators and the developers of anonymization software. As security tools become better at identifying and blocking traffic from known malicious IP ranges, the demand for "clean" residential IPs grows. This creates a market where even the most secure networks are targeted, not necessarily to steal their data, but to steal their "identity" in the form of their IP address.
The Challenge of Detection and Mitigation
One of the primary reasons residential proxies are so effective is that they are notoriously difficult to detect through standard monitoring. Traditional firewalls and intrusion detection systems (IDS) are often configured to look for patterns of behavior associated with automated scripts or known bad actors. However, because residential proxy traffic is routed through a legitimate host device, it often mimics the behavior of a human user.
The research from Infoblox and Layer3 Intel suggests that organizations must move beyond simple IP blacklisting. Since residential IPs are dynamic and assigned to real people, blacklisting them can lead to significant "false positives," where legitimate users are blocked from accessing services. Instead, security teams are being urged to look deeper into the behavior of the applications running on their endpoints and to maintain stricter control over what software is permitted on the network.
The Residential Proxy Observatory’s work in identifying the activity on AS2650 is a testament to the need for specialized monitoring tools that can distinguish between a standard user session and a proxy relay. As the boundary between personal and professional devices continues to blur, and as the sophistication of anonymization tools increases, the task of keeping residential proxies out of sensitive networks will likely remain a top priority for cybersecurity experts.
Conclusion
The presence of residential proxy activity at the heart of the U.S. administration serves as a powerful illustration of the evolving nature of digital threats. It demonstrates that the challenges of the modern internet—anonymity, the exploitation of trusted networks, and the global reach of unauthorized software—affect everyone from the remote residents of St. Helena to the staff of the White House.
As the Residential Proxy Observatory continues its monitoring, the findings will likely serve as a catalyst for a broader discussion on network hygiene and the risks posed by "hidden" software. For now, the discovery within the AS2650 network remains a significant marker of how deeply residential proxies have integrated themselves into the global internet infrastructure, proving that even the most high-profile networks are subject to the same vulnerabilities as the rest of the connected world.
 Small Business IT & Cloud Computing
WordPress Issues Emergency Patch for Critical RCE Vulnerability as Attackers Strike Within Hours of Disclosure
The global cybersecurity community is on high alert following the release of...
 Small Business IT & Cloud Computing
Alibaba Unveils Qwen4-Max with Claims of Massive Cost Reductions and Enhanced Cyber Defenses Amid Analyst Skepticism
Alibaba has officially pulled back the curtain on its latest flagship artificial...
 Small Business IT & Cloud Computing
OpenAI Terminates Contractors for Utilizing Artificial Intelligence in Model Training Processes
In an industry defined by the rapid advancement of artificial intelligence, a...







