
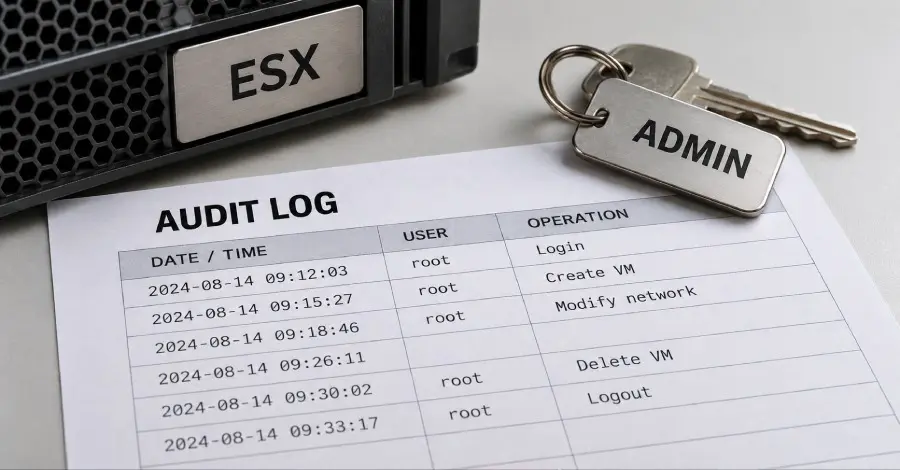
The United States Cybersecurity and Infrastructure Security Agency (CISA) has formally expanded its Known Exploited Vulnerabilities (KEV) catalog to include a security flaw impacting Broadcom’s VMware ESX. The move, announced on Wednesday, follows a series of sophisticated cyberattacks attributed to a prominent China-nexus threat actor. The vulnerability, which allows administrative actions to bypass standard logging protocols, was reportedly weaponized as a zero-day earlier this year to facilitate stealthy operations within the U.S. legal sector.
The inclusion of the flaw, identified as CVE-2026-41709, underscores the persistent threat posed by state-sponsored adversaries who specialize in subverting infrastructure management tools to maintain long-term access to sensitive environments. While the vulnerability carries a relatively low CVSS score of 2.7, its utility in the hands of an advanced persistent threat (APT) actor is significant, providing a mechanism for "anti-forensic" maneuvers that complicate incident response and detection.
The Mechanics of CVE-2026-41709
The security flaw is categorized as an insufficient logging vulnerability. In a standard enterprise environment, every administrative action—from the creation of new virtual machines to the modification of network permissions—is recorded in a secure audit trail. These logs are the primary resource for security operations centers (SOCs) and forensic investigators when attempting to reconstruct a breach.
CVE-2026-41709 permits a malicious actor who has already obtained administrative privileges to perform specific operations without triggering these essential log entries. By effectively "silencing" the system’s internal auditing mechanisms, the attacker can move laterally or modify the environment without leaving the digital fingerprints typically picked up by security monitoring tools.
Broadcom, which acquired VMware in 2023, initially addressed the issue in July 2026. At the time of the advisory, the company released patches for several versions of its virtualization software, urging administrators to update their systems to ensure full audit integrity. However, recent findings from the private sector indicate that the vulnerability had already been identified and exploited by sophisticated hackers months before a public fix was available.
Warp Panda and the Targeting of the Legal Sector
The catalyst for CISA’s update was a detailed intelligence report from CrowdStrike, titled the "2026 Legal Threat Landscape Report." The research identified a threat actor known as Warp Panda as the primary driver behind the exploitation of CVE-2026-41709. Warp Panda, a group with a long history of high-stakes cyber espionage, reportedly used the flaw as a zero-day in early 2026.
According to the report, the adversary’s primary objective in the legal sector was to reduce the visibility of their audit trail. By exploiting the VMware flaw, Warp Panda could operate within highly sensitive vCenter environments—the centralized management hubs for VMware infrastructure—with a much lower risk of discovery.
The legal sector has increasingly become a prime target for state-sponsored espionage. Law firms and legal departments often hold a concentrated repository of high-value information, including proprietary client communications, strategic plans for mergers and acquisitions, sensitive litigation strategies, and intellectual property. For a state-directed adversary, compromising a single major law firm can provide a "downstream" advantage, offering insights into multiple corporate and government entities simultaneously.
 Cybersecurity Basics & Security News
Active Exploitation of Two New Unpatched Zero-Day Vulnerabilities Discovered in Citrix NetScaler Appliances
Security researchers and enterprise IT departments are on high alert following reports...
 Cybersecurity Basics & Security News
Critical OpenAI Vulnerability Allowed Attackers to Hijack ChatGPT Sessions via Malicious Shared Links
In a significant discovery for the landscape of artificial intelligence security, researchers...
 Cybersecurity Basics & Security News
Security Researcher Unveils ‘Tailworm’ Report, Highlighting Critical Privilege Escalation Risks in Tailscale SSH
A comprehensive security analysis published this week has sent ripples through the...







