
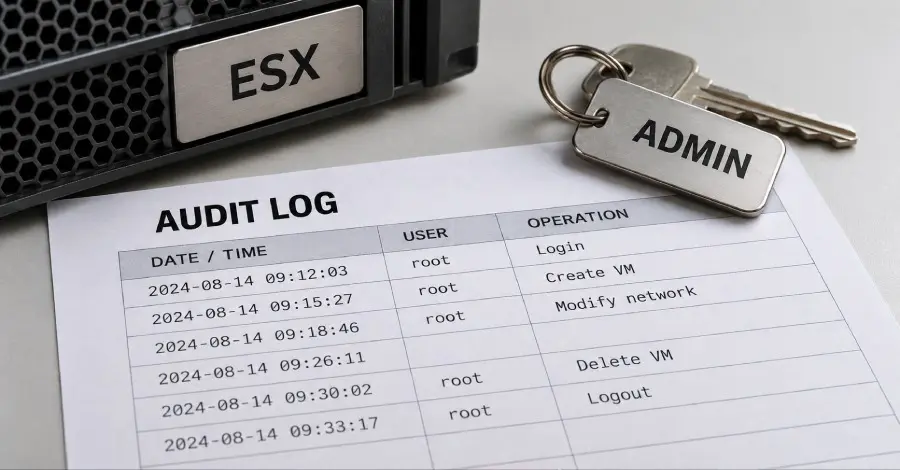
CrowdStrike’s analysis characterized Warp Panda as a sustained and strategically focused threat to U.S. entities. The group’s ability to pivot from initial access to deep infrastructure compromise makes them a particularly formidable opponent for organizations maintaining large-scale virtualized environments.
A History of High-Profile Exploitation
Warp Panda is known by several other monikers within the cybersecurity community, including Armory Castle (formerly UNC5221), Clay Typhoon, and VerdantBamboo. This actor has established a reputation for identifying and weaponizing zero-day vulnerabilities in internet-facing edge devices.
In the past, the group has been linked to the exploitation of critical flaws in Citrix NetScaler and Ivanti Connect Secure devices. These edge devices are often the first line of defense for an enterprise network, and vulnerabilities within them allow attackers to bypass the perimeter entirely. Once inside, Warp Panda typically shifts its focus toward maintaining persistence and harvesting credentials.

The group’s recent activity is not limited to VMware. Earlier in October 2026, Mandiant, a subsidiary of Google, attributed the exploitation of a critical improper origin validation flaw in BeyondTrust Remote Support (CVE-2026-102764) to the same hacking crew. In those instances, the attackers utilized the high-severity vulnerability (CVSS 9.3) to deliver custom malware families, such as SAWFLY and BARECLAW, further demonstrating their diverse toolkit and technical proficiency.
Advanced Tactics: From vCenter to the Cloud
The operational methodology of Warp Panda involves a multi-stage approach that begins with the exploitation of internet-facing hardware. Once a foothold is established, the threat actor pivots to the internal virtualization layer. By targeting VMware vCenter environments, the group can gain control over the underlying servers that power an organization’s most critical applications.
To maintain this access, Warp Panda deploys custom malware specifically designed for virtualization platforms. This includes BRICKSTORM and SharpStorm, tools that allow for persistent backdoors and remote command execution. The use of such specialized malware indicates a high level of investment in research and development, tailored specifically to bypass modern security stacks.
Beyond the virtualization layer, the adversary has demonstrated a sophisticated ability to move into cloud environments. In several documented intrusions, Warp Panda targeted cloud services with the intent of extracting user session tokens. This technique allows the attackers to access Microsoft 365 environments without the need for traditional credentials, effectively bypassing password-based alerts and multi-factor authentication (MFA) prompts.
 Cybersecurity Basics & Security News
PostgreSQL Issues Critical Security Updates to Address Type Confusion Flaw and 51 Other Vulnerabilities
The PostgreSQL Global Development Group has announced the release of critical security...
 Cybersecurity Basics & Security News
The Rise of the Personal AI Agent: Navigating the Shift from BYOD to BYOAI in the Corporate Security Landscape
The rollout of personal artificial intelligence agents is proving to be a...
 Cybersecurity Basics & Security News
Critical WordPress Vulnerability Turns Core Update Process Into Attack Vector
The very mechanism designed to keep millions of websites secure has emerged...







