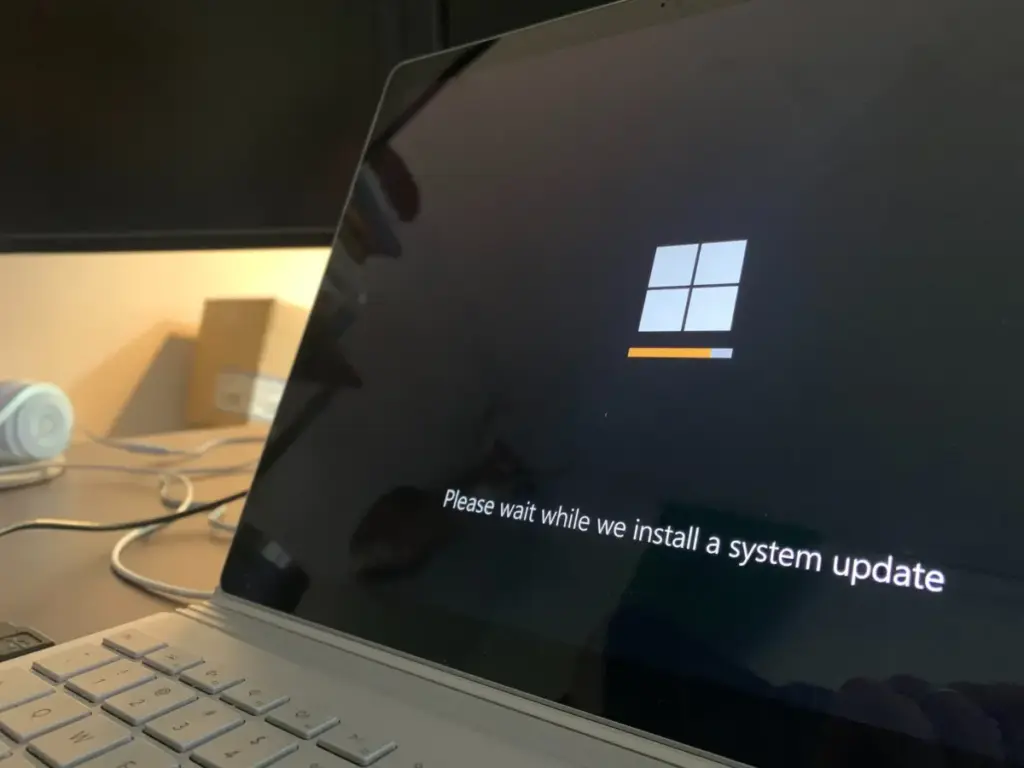
In an unprecedented move that has sent shockwaves through the cybersecurity and IT management sectors, Microsoft has released its October 2026 Patch Tuesday update, marking the largest single-month security release in the company’s history. With a staggering 1,408 Common Vulnerabilities and Exposures (CVEs) requiring immediate customer action, the release dwarfs previous records and presents a monumental challenge for systems administrators worldwide. To put the scale into perspective, the previous record was set only a month ago in September, which carried 963 CVEs. This rapid escalation in the volume of discovered and patched vulnerabilities underscores an increasingly complex threat landscape and a rigorous internal auditing process at the Redmond-based tech giant.
Of the 1,408 vulnerabilities addressed this month, 72 have been classified as critical, the highest severity rating assigned by Microsoft. These flaws, if left unpatched, could allow for remote code execution, unauthorized elevation of privileges, or complete system compromise with little to no user intervention. The sheer volume of the release has prompted security experts and readiness teams to urge organizations to prioritize their patching schedules, focusing on the most immediate threats to their infrastructure.
Active Exploits and Public Disclosures
The most pressing concern for security teams is the presence of vulnerabilities that are already being exploited in the wild. Highlighting this urgency is CVE-2026-96951, a significant flaw within the Windows Shell. This vulnerability is designed to bypass "Mark of the Web" (MotW), a critical security feature in Windows that flags files originating from the internet or other untrusted locations. By circumventing this defense, attackers can deliver malicious payloads that bypass traditional security prompts, making it significantly easier to compromise end-user devices.
Furthermore, a significant discrepancy has emerged regarding a SharePoint Server flaw. While Microsoft’s official documentation for some time suggested certain vulnerabilities were not under active attack, reports from September 25 confirmed that CVE-2026-65660—a SharePoint flaw originally addressed in August—is indeed being exploited in the wild. This serves as a stark reminder to IT departments that the "not exploited" status can change rapidly, and even previously patched systems require diligent monitoring.
In addition to active exploits, two other vulnerabilities were publicly disclosed prior to the Patch Tuesday release. These include flaws within the .NET Framework and the MessagePack-CSharp library. Public disclosure significantly increases the risk of exploitation, as threat actors often move quickly to develop functional exploits once the details of a vulnerability are made known to the public.
Known Issues and Technical Hurdles
As is often the case with updates of this magnitude, the October release has introduced several known issues that administrators must navigate. Shortly after the rollout began on October 14, Microsoft acknowledged a significant bug affecting Windows 11 updates, specifically KB5127648 (for versions 24H2, 25H2, and 26H2) and KB5127646 (for version 26H1).
The issue involves a conflict with "Administrator protection," a feature enabled by default in Windows 11 security baselines. Following the update, non-administrator users may find themselves unable to establish Remote Desktop connections to managed devices, resulting in error code 0xC000000D. Microsoft has traced the root of this problem back to September’s non-security preview update. As a temporary mitigation, Microsoft suggests that administrators disable Administrator protection through policy management tools until a formal fix is issued in a subsequent update. Security experts recommend testing remote access on a subset of managed hosts before proceeding with a broad deployment to avoid widespread connectivity disruptions.
Microsoft Windows and Infrastructure Security
 Small Business IT & Cloud Computing
OpenAI Terminates Contractors for Utilizing Artificial Intelligence in Model Training Processes
In an industry defined by the rapid advancement of artificial intelligence, a...
 Small Business IT & Cloud Computing
Micron Warns of Persistent Memory Shortage Through 2028 as Industry Braces for Protracted Price Hikes
The global semiconductor landscape is facing a prolonged period of volatility as...
 Small Business IT & Cloud Computing
Meta’s AI Vision Is the Best in the Industry—But Its History Makes It Impossible to Trust
We are currently standing on the precipice of a fundamental revolution in...