
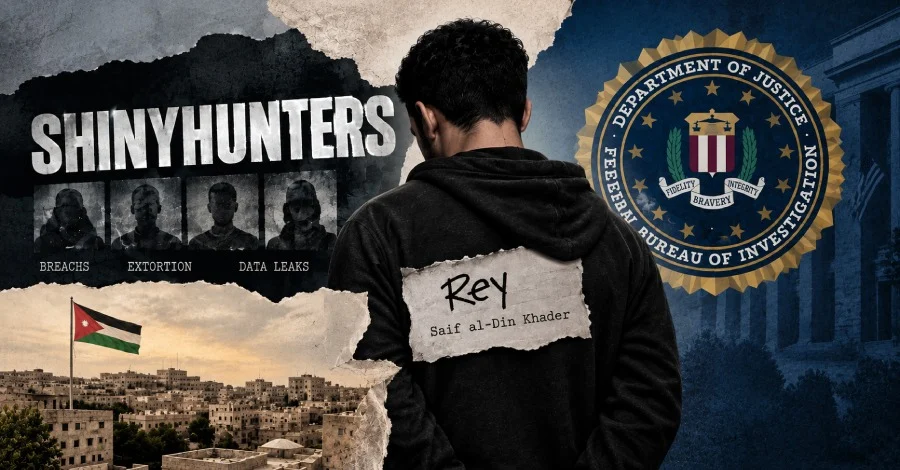
Khader, who also operated under the moniker ReyXBF, is far from an obscure figure in the world of illicit data brokerage and digital extortion. His arrest in Jordan is being viewed as a pivotal moment for investigators, as reports suggest that Khader is currently cooperating with the FBI and other international law enforcement agencies. This cooperation is expected to provide critical intelligence regarding the internal hierarchy, operational protocols, and identities of other members within the ShinyHunters network. One source noted that Khader’s willingness to provide information could be the key to unmasking the remaining actors in a group that has historically proven to be exceptionally elusive.
The profile of Saif al-Din Khader reveals a career deeply embedded in the most active corners of the cybercriminal underground. In late 2025, independent security journalist Brian Krebs identified Khader as one of the primary administrators of an entity known as Scattered LAPSUS$ Hunters (SLH). This group is widely believed to be a sophisticated amalgamation of three of the most disruptive threat actor groups in recent history: Scattered Spider, LAPSUS$, and ShinyHunters. By merging their resources and expertise, these groups created a formidable alliance capable of targeting high-value corporate assets with unprecedented efficiency.
Khader’s influence extended beyond the SLH umbrella. He was previously recognized as an administrator for the data leak site of Hellcat, a ransomware-as-a-service (RaaS) operation that emerged in the latter half of 2024. Perhaps most significantly, Khader is alleged to have taken over the leadership of the most recent iteration of BreachForums, the premier destination for the sale and distribution of stolen databases. Interestingly, Khader’s relationship with law enforcement may not be entirely new; he reportedly informed Krebs that he had been in contact with authorities and cooperating in some capacity since at least June 2025. This suggests a complex, double-sided existence that may have finally collapsed with his formal detention in Jordan.
The apprehension of Khader is the second major blow dealt to the ShinyHunters brand in a matter of weeks. Just prior to the news from Jordan, authorities in the Netherlands arrested a 24-year-old man in Amsterdam in connection with the group’s malicious operations. While official channels were initially reserved regarding his identity, subsequent reports identified the man as Pepijn van der Stap. Van der Stap occupied a unique position in the tech world, serving as an offensive security lead at the Dutch firm Neo Security. His arrest highlighted the often-blurred lines between the professional cybersecurity sector and the underground hacking scene. Despite the evidence presented by investigators, a spokesperson for ShinyHunters denied any affiliation with van der Stap, a move that some analysts view as an attempt to maintain operational security or distance the "brand" from individuals who have been compromised.

In the wake of these arrests, the leadership of the FBI has taken an uncharacteristically public and combative stance. FBI Director Kash Patel utilized social media to signal that the investigation is rapidly gaining momentum. In a series of posts, Patel emphasized that the bureau is actively pursuing new leads generated by the recent detentions and warned that further arrests are imminent. This public posturing appears to be part of a broader psychological operation intended to sow distrust among the remaining members of the group and pressure them into surrendering.
The recent activities of ShinyHunters explain why the group has become a top priority for federal investigators. In a daring display of technical skill and criminal hubris, the group recently hijacked the darknet presence of a rival cybercriminal organization, the Cl0p ransomware gang. By exploiting an unpatched vulnerability in the Grav Content Management System (CMS), ShinyHunters seized control of Cl0p’s leak site, effectively "hacking the hackers." Furthermore, the group claimed a direct strike against the FBI itself by breaching the "apply.fbijobs.gov" portal. During this intrusion, they allegedly exfiltrated approximately three terabytes of sensitive data, including information related to potential applicants for positions within the bureau.
The motive behind the FBI job portal breach appears to be more political than financial. ShinyHunters asserted that they were not seeking a ransom payment for the stolen data. Instead, they claimed the hack was an effort to force the FBI to retract what the group described as false allegations. Specifically, the group has taken issue with the FBI’s attempts to link them to "The Com," a decentralized and notoriously violent cybercrime collective. The Com is known not just for digital crimes like SIM swapping and phishing, but for real-world violence, including kidnapping, physical assault, and the practice of "swatting"—sending armed police responses to the homes of targets under false pretenses. ShinyHunters has sought to distinguish its "business-oriented" model of data extortion from the more chaotic and brutal tactics associated with The Com.
Despite the group’s attempts to frame themselves as high-end digital entrepreneurs, the FBI maintains a starkly different view of their impact. Brett Leatherman, the assistant director of the FBI’s cyber division, provided a sobering assessment of the group’s reach. According to Leatherman, the collective and its co-conspirators have compromised more than 140 organizations since last year, extracting an estimated $70 million in extortion payments. Their primary tactic involves targeting third-party vendors and cloud-based platforms, which allows them to gain access to vast repositories of sensitive customer data that can then be used as leverage against the victimized corporations.
Leatherman’s public statements have been framed as a direct ultimatum to those still active within the ShinyHunters network. He noted that the seizure of digital infrastructure often provides a roadmap for investigators, revealing the footprints of those who believe they are anonymous. "Arrests have a way of changing who is willing to talk," Leatherman stated, suggesting that the information provided by individuals like Khader is already narrowing the window of escape for his former associates. He urged other members to come forward and cooperate before they are tracked down, emphasizing that the FBI’s ability to find them is no longer a matter of if, but when.

To understand the resilience of ShinyHunters, cybersecurity researchers have looked back at the group’s lineage. A joint analysis by Sekoia and Beazley Security traced the group’s origins to the remnants of two earlier extortion groups: TheDarkOverlord and GnosticPlayers. Both of those organizations were infamous for large-scale data breaches and aggressive ransom demands in the late 2010s. The ShinyHunters brand itself solidified around the spring of 2020, initially gaining notoriety for selling stolen databases on the now-defunct RaidForums.
The true strength of ShinyHunters, according to researchers Enzo Saez and Robert Venal, lies in its modular structure. It has evolved from a small, tight-knit crew into a persistent business model that can survive the loss of individual members or leaders. The group operates through a sophisticated division of labor: social engineers secure initial access, adjacent actors assist with recruitment and technical amplification, and the final monetization occurs under the recognizable ShinyHunters brand. This decentralized approach has allowed the collective to absorb indictments and forum seizures over the past six years without ever remaining dormant for long.
However, the current wave of arrests in Jordan and the Netherlands, combined with the apparent cooperation of high-ranking administrators like Saif al-Din Khader, represents perhaps the most significant challenge to the group’s continuity to date. As the FBI leverages the data seized from BreachForums and the testimonials of detained members, the "modular" resilience of the ShinyHunters brand is being put to its ultimate test. For now, the global law enforcement community appears to have the initiative, turning the hunters into the hunted.
 Cybersecurity Basics & Security News
The Silent Proliferation: Enterprise Security Grapples with the Rise of Invisible AI Agents
As the enterprise landscape prepares for the full-scale integration of artificial intelligence,...
 Cybersecurity Basics & Security News
CISA Issues Urgent Warning Over Actively Exploited Ivanti Connect Secure Zero-Day Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a critical advisory...
 Cybersecurity Basics & Security News
OpenAI Dismisses Safety Researchers Following Leak of Confidential Infrastructure Data Amid Growing Security Concerns
OpenAI has terminated the employment of three prominent members of its safety...







