
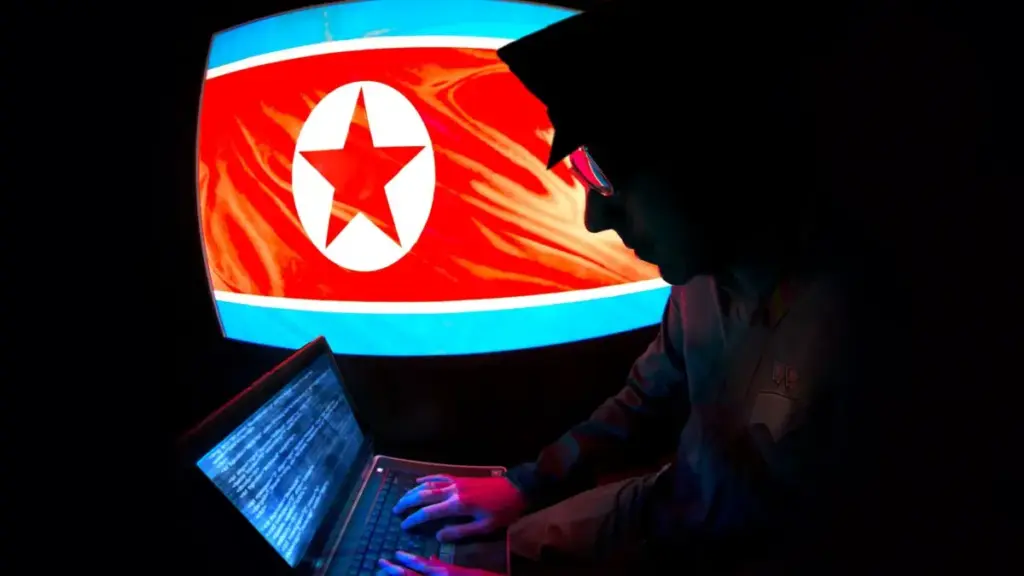
The threat posed by these actors is not merely theoretical; the agencies cited several instances where the group’s activities escalated into direct confrontation and sabotage. In one case, the criminals extorted a company over a payment dispute and subsequently published the firm’s proprietary source code online when their demands were not met. In another incident, a North Korean operative who had successfully been hired for website maintenance used their access to deface the company’s site and render it completely inaccessible to the public.
Nick Tausek, lead security automation architect at Swimlane, noted that this campaign represents a significant expansion of the established North Korean playbook. By targeting both the hiring process and the developers themselves, the group has created a self-sustaining cycle of fraud.
"Fake IT workers seek salary income and trusted access from inside a company. WaterPlum targets legitimate applicants from the outside," Tausek explained. "Stolen credentials, source code, and identity documents can then support espionage, extortion, or new fraudulent personas. The shared laptop farms and IP addresses cited in the advisory suggest these aren’t isolated schemes. Each operation can feed the other. They can steal identities and credentials that help fraudulent workers appear legitimate. Those workers can then gain trusted access to corporate systems, opening further opportunities for theft or disruption."
Ross Filipek, CISO at Corsica Technologies, underscored the systemic risk that freelance and contract work introduces to the modern enterprise. In an era where remote work is the norm, a single compromised contractor can serve as a "Patient Zero" for a much larger corporate breach.
"One compromised workstation can expose several employers or clients without any of them being directly attacked," Filipek said. "Organizations need to know how outside developers access their environments and what information can leave through those accounts. Unknown code should be isolated before execution."
The advisory serves as a stark reminder that for North Korean cyber actors, the recruitment process is not just a way to earn a salary, but a potent vector for state-sponsored warfare and financial gain. Security agencies are advising all IT professionals to exercise extreme caution when asked to download software or run code during an interview process, particularly when the request comes from an unverified or recently created profile on a freelance platform. Organizations are likewise encouraged to implement stricter vetting processes and isolated "sandbox" environments for any technical testing of prospective hires.
 Helpdesk & IT Service Management (ITSM)
Bridging the Gap Between AI Adoption and Business Value: The Evolving Reality of IT Service Management
For years, the mere adoption of Artificial Intelligence was considered the ultimate...
 Helpdesk & IT Service Management (ITSM)
Omdia Research Highlights Significant Cost Savings and Operational Gains for MSPs and IT Teams Adopting Unified Management Platforms
In an era defined by tightening budgets and an explosion of digital...
 Helpdesk & IT Service Management (ITSM)
Overe Appoints Former Sophos CSO Simon Reed as Strategic Advisor to Accelerate MSP Security Growth
In a significant move aimed at strengthening its leadership and deepening its...







