
Persistence and Exfiltration Strategies
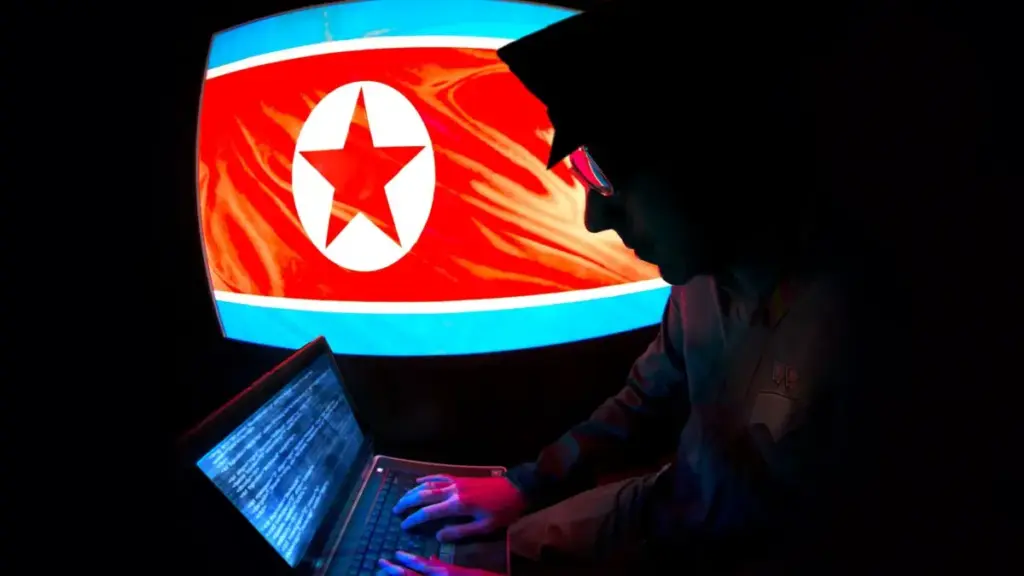
The initial infection is only the beginning of the WaterPlum lifecycle. Once the malware is executed, the attackers deploy Remote-Access Trojans (RATs) to establish a foothold. These RATs are designed to maintain a constant connection with the compromised device, ensuring persistence even if the user reboots their system or changes their network settings.
These pathways allow the attackers to pivot across the victim’s systems and potentially into any corporate networks to which the developer has access. Using advanced infostealers, the group exfiltrates a wide range of sensitive data back to Command-and-Control (C2) IP addresses. These C2 servers act as the central nervous system for the operation, allowing the remote management of thousands of infected devices and networks simultaneously.
The data targeted for theft is comprehensive and designed to facilitate further financial crime or identity fraud. This includes authentication data stored in web browsers—such as usernames and passwords—as well as clipboard information, key-logs, and screenshots of the victim’s desktop. Most critically for the group’s immediate funding, the malware specifically searches for cryptocurrency wallet data, including private keys and seed phrases, which are then used to drain the victims’ funds.
Japanese authorities have emphasized that the threat extends far beyond the individual freelancer. "Beyond immediate credential theft, successful infections provide WaterPlum actors opportunities to infiltrate organizations employing targeted developers, enabling espionage, intellectual property theft, and additional lateral movement in corporate environments," the agencies warned in a joint statement. Furthermore, the stolen identity documents and images obtained through these "interviews" are repurposed by North Korean IT workers to create fake personas, allowing them to bypass international sanctions and generate foreign currency for the regime.
Another North Korean threat campaign
The investigation into WaterPlum reveals a complex logistical network supporting these cyber operations. According to the reporting agencies, while the masterminds behind the campaign are primarily based in North Korea, China, and Russia, the operational footprint extends into Africa and Southeast Asia.
One of the more alarming aspects of the group’s infrastructure is the operation of "laptop farms." These facilities are used to host and manage hardware that provides a veneer of legitimacy for fake IT workers. In these farms, attackers can simulate a local presence in a target country, making it difficult for HR departments to flag them as high-risk or fraudulent applicants.
 Helpdesk & IT Service Management (ITSM)
SolarWinds Announces Comprehensive September Webinar Series Addressing AI Integration, IT Observability, and Cloud Database Migration Challenges
The modern data landscape is currently undergoing a period of unprecedented transformation,...
 Helpdesk & IT Service Management (ITSM)
Keeper Security Hits Major Milestone with 100,000 Enterprise Customers Amid Rapid Growth in Identity Security Market
In a significant validation of the growing demand for unified identity and...
 Helpdesk & IT Service Management (ITSM)
International Law Enforcement Operation Dismantles KillSec Ransomware Group and Arrests Teenage Mastermind
In a sweeping international law enforcement operation coordinated across multiple borders, authorities...







