
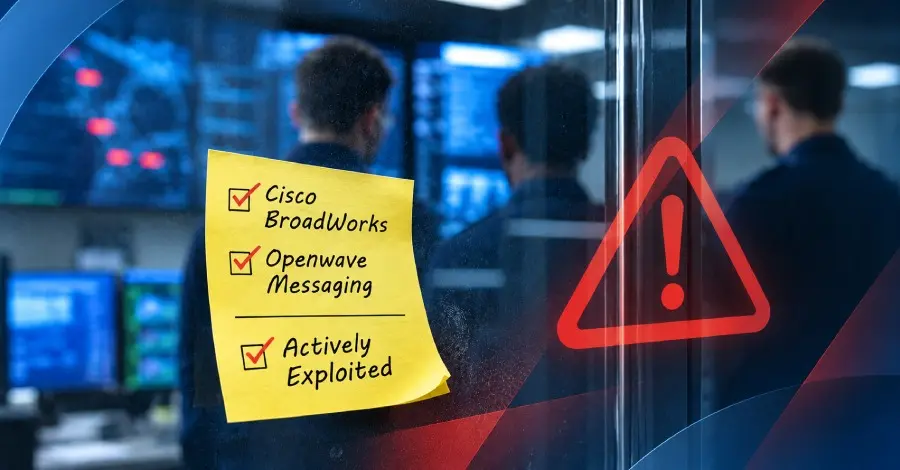
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a fresh set of mandates for federal agencies and private sector partners following the discovery of active exploitation targeting enterprise-grade communication and messaging infrastructure. On Tuesday, the agency officially updated its Known Exploited Vulnerabilities (KEV) catalog, adding two significant security flaws impacting Cisco BroadWorks and the Openwave Messaging Webtop Media Transcoder.
The move marks a continued effort by the federal government to stay ahead of sophisticated threat actors who have increasingly shifted their focus toward the underlying infrastructure of global communications. By adding these vulnerabilities to the KEV list, CISA is signaling that these are not merely theoretical risks but are currently being leveraged in real-world attacks.
Cisco BroadWorks, a widely utilized cloud communications platform used by service providers to deliver VOIP, unified communications, and mobile services, represents a high-value target for adversaries. Similarly, the Openwave Messaging Webtop Media Transcoder is a critical component in carrier-grade messaging environments. The exploitation of such systems can provide attackers with deep access to sensitive communication streams, user data, and the broader network architecture of service providers and large-scale enterprises.
As is common with early-stage disclosures involving high-stakes infrastructure, the specific technical details regarding the methods of exploitation remain closely guarded. CISA has confirmed that there is evidence of active abuse but has not yet released a public post-mortem on the mechanics of the breaches. Furthermore, the agency has not formally attributed the activity to a specific threat actor or nation-state group. While Cisco has acknowledged the vulnerabilities and issued relevant advisories, the company’s initial public statements did not explicitly detail the extent of the malicious use discovered by federal monitors.
This latest update to the KEV catalog comes during a particularly turbulent period for enterprise networking security. The addition of the BroadWorks and Openwave flaws follows a series of high-profile disclosures from Cisco involving other core components of its portfolio. Late last month, the networking giant revealed that two separate vulnerabilities in its Catalyst SD-WAN and its flagship security appliances were being actively exploited by hackers.
One of those flaws, identified as CVE-2026-20127, carried a maximum CVSS severity score of 10.0. Impacting the Catalyst SD-WAN, the vulnerability allowed for a complete takeover of affected systems, granting attackers the ability to manipulate network traffic at a foundational level. Simultaneously, Cisco addressed CVE-2026-76418, a critical flaw with a CVSS score of 8.6 affecting the Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software. These platforms are the bedrock of perimeter security for thousands of organizations worldwide, and their exploitation underscores a trend where attackers bypass endpoints to strike at the heart of the network.
The decision by CISA to mandate the patching of the BroadWorks and Openwave Messaging flaws is rooted in Binding Operational Directive (BOD) 22-01. This directive requires Federal Civilian Executive Branch (FCEB) agencies to remediate vulnerabilities identified in the KEV catalog within specific timeframes. For these latest additions, agencies have been given a deadline of November 24, 2026, to apply the necessary security updates and mitigate the risk of compromise.
While the mandate technically applies only to federal agencies, CISA strongly urges private sector organizations and critical infrastructure providers to follow suit. The KEV catalog has evolved into a de facto prioritization guide for security teams globally. In an era where thousands of new vulnerabilities are discovered annually, the catalog serves as a filter, helping administrators focus on the "known-knowns"—the vulnerabilities that are actually being used by adversaries to gain unauthorized access.
The lack of public information regarding the threat actors involved in these latest exploits has led to significant speculation within the cybersecurity community. Historically, infrastructure-level vulnerabilities in platforms like BroadWorks are the domain of advanced persistent threat (APT) groups, often associated with state-sponsored espionage. These actors prioritize "living off the land" techniques and the exploitation of edge devices to maintain long-term persistence within a target network without being detected by traditional endpoint detection and response (EDR) tools.

The targeting of a media transcoder, such as the one in the Openwave Messaging suite, is particularly telling of the current threat landscape. Media transcoders are responsible for converting data formats for various devices and platforms. Because they sit at the intersection of different data streams, a compromise at this level can allow an attacker to intercept, modify, or inject malicious content into communications as they are processed. For an intelligence-gathering operation, this is an ideal vantage point.
Security experts note that the rapid succession of Cisco-related vulnerabilities being added to the KEV catalog highlights the increasing pressure on legacy infrastructure. As organizations migrate to more complex, software-defined environments, the attack surface expands. Platforms that were once considered "internal" or "backend" are now frequently exposed to the internet or are accessible through compromised VPNs and management interfaces.
The timeline for remediation—less than two weeks—reflects the urgency of the situation. For federal agencies, the process of patching enterprise-level communication platforms is rarely a simple task. It requires extensive testing to ensure that security fixes do not disrupt critical services. However, CISA’s stance remains clear: the risk of an active exploit outweighs the operational challenges of rapid deployment.
For Cisco, the recent string of exploits represents a significant challenge in maintaining the integrity of its ecosystem. The company has invested heavily in its Security Advisories and Response Team (PSIRT), but the sheer volume of exploitation attempts against its hardware and software continues to rise. The vulnerabilities in the ASA and FTD software, which are designed to protect networks, are particularly ironic targets for attackers, turning a security asset into a liability.
The broader implications of these disclosures suggest a shift in the "rules of engagement" for cyber defense. In previous years, the primary concern for many IT departments was the protection of individual workstations from malware or ransomware. Today, the focus has shifted toward the resilience of the network fabric itself. If the routers, firewalls, and communication platforms are compromised, the security of the endpoints becomes largely irrelevant.
CISA’s role in this ecosystem has become more proactive under recent leadership. By acting as a clearinghouse for threat intelligence and a centralized authority for vulnerability management, the agency aims to reduce the "mean time to remediate" across the entire federal enterprise. The KEV catalog is the primary tool in this effort, ensuring that when a fire is spotted, the response is immediate and uniform.
As the November 24 deadline approaches, cybersecurity analysts expect more information to emerge regarding the nature of the attacks. It is common for researchers to release technical deep-dives once the initial patching window has closed, providing the community with the signatures and indicators of compromise (IOCs) needed to hunt for signs of past breaches.
For now, the focus remains on defense. Organizations using Cisco BroadWorks or Openwave Messaging Webtop Media Transcoder are advised to audit their systems immediately. This involves not only applying the latest patches but also reviewing logs for any anomalous activity that may suggest an attacker has already gained a foothold. In many cases, patching a vulnerability does not remove an attacker who has already established persistence; it merely closes the door for future intruders.
The ongoing exploitation of these enterprise tools serves as a stark reminder that the perimeter is constantly under siege. As the 2026 threat landscape continues to evolve, the collaboration between government agencies like CISA and private vendors like Cisco will be crucial in defending the digital infrastructure that underpins modern society. The speed at which these vulnerabilities are identified, cataloged, and remediated will likely determine the success or failure of national cybersecurity strategies in the years to come.
 Cybersecurity Basics & Security News
The Rise of the Personal AI Agent: Navigating the Shift from BYOD to BYOAI in the Corporate Security Landscape
The rollout of personal artificial intelligence agents is proving to be a...
 Cybersecurity Basics & Security News
AI vs. AI: How Researchers Used Claude Opus 5 to Breach OpenAI’s Internal Systems
In a sophisticated demonstration of the "double-edged sword" nature of generative artificial...
 Cybersecurity Basics & Security News
OpenAI Dismisses Safety Researchers Following Leak of Confidential Infrastructure Data Amid Growing Security Concerns
OpenAI has terminated the employment of three prominent members of its safety...







