
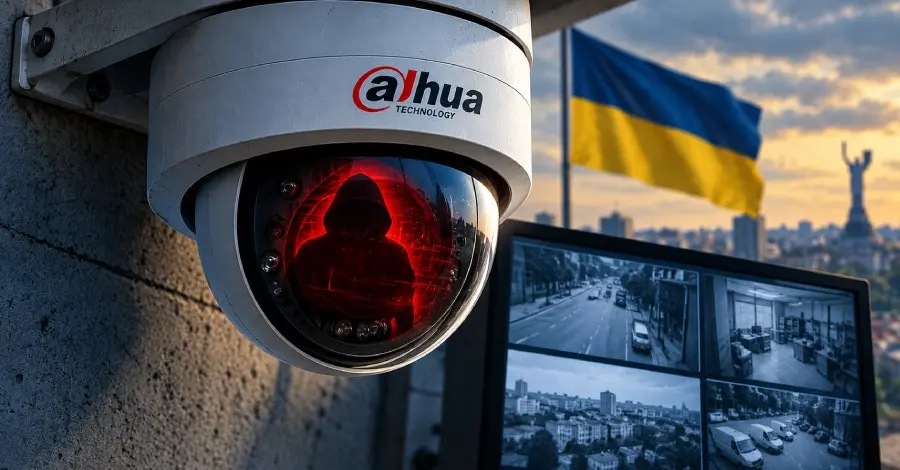
The Computer Emergency Response Team of Ukraine (CERT-UA) has issued a critical security alert following a surge in unauthorized remote access incidents targeting video surveillance infrastructure manufactured by Dahua Technology. The warning highlights a sophisticated campaign where threat actors are gaining full control over Internet Protocol (IP) cameras and Digital Video Recorders (DVRs), allowing them to hijack live video streams, alter critical device configurations, and establish persistent third-party accounts. This wave of cyberattacks represents a significant threat to both private security and national stability, particularly as these devices are increasingly being leveraged for intelligence gathering in the ongoing conflict within the region.
According to a formal statement from the State Special Communications Service of Ukraine (SSSCIP), the recorded compromises involve more than just passive observation. Attackers are actively manipulating the internal settings of the surveillance hardware, ensuring they maintain long-term access while potentially blinding the legitimate owners to the breach. The scale and frequency of these incidents have prompted Ukrainian authorities to urge immediate defensive measures across all sectors that rely on Dahua hardware for physical security and monitoring.
The primary gateway for these intrusions has been identified as Easy4IP, a widely used peer-to-peer (P2P) platform designed by Dahua to facilitate remote monitoring. Easy4IP is marketed as a user-friendly solution for homeowners and small business owners, allowing them to connect their IP cameras, Network Video Recorders (NVRs), and DVRs to a smartphone application or web browser. The system is designed for convenience, enabling users to register their devices by simply scanning a QR code or manually entering a hardware Serial Number (SN). By utilizing a cloud-based relay, the P2P service allows users to view their camera feeds from anywhere in the world without the need for complex network configurations like port forwarding or static IP addresses.
However, the very features that make Easy4IP accessible have become its greatest security liabilities. CERT-UA and independent cybersecurity researchers have warned that the serial numbers used to register these devices follow a highly predictable and structured format. These identifiers typically consist of a 10-character model prefix—which remains identical for every unit within a specific device family—followed by a five-character hexadecimal counter. This counter is incremented almost sequentially, meaning that if an attacker knows the serial number of one device in a product line, they can accurately predict the serial numbers of thousands of others.
This predictability effectively eliminates the "security through obscurity" that many users rely on. Because the serial numbers are not randomized, threat actors can employ automated brute-force attacks at a massive scale. By cycling through sequential hexadecimal combinations, attackers can systematically probe the Dahua cloud infrastructure to identify which serial numbers are currently active and connected to the P2P relay. Crucially, this method of discovery does not appear to trigger standard rate limits or account lockouts, allowing attackers to map out thousands of reachable devices with minimal resistance.
 Cybersecurity Basics & Security News
Critical Security Flaws in Meta Muse AI Agent Allowed Silent Data Theft and Full System Compromise
A sophisticated security vulnerability discovered in Meta’s personal artificial intelligence assistant, Muse,...
 Cybersecurity Basics & Security News
CISA Alerts Federal Agencies to Exploited VMware ESX Vulnerability Following Targeted Cyber Espionage Campaign
The United States Cybersecurity and Infrastructure Security Agency (CISA) has formally expanded...
 Cybersecurity Basics & Security News
Security Flaw in Anthropic’s Claude Code Exposes Sensitive Developer Secrets on Public GitHub Repositories
The rapid integration of artificial intelligence into the software development lifecycle has...







