
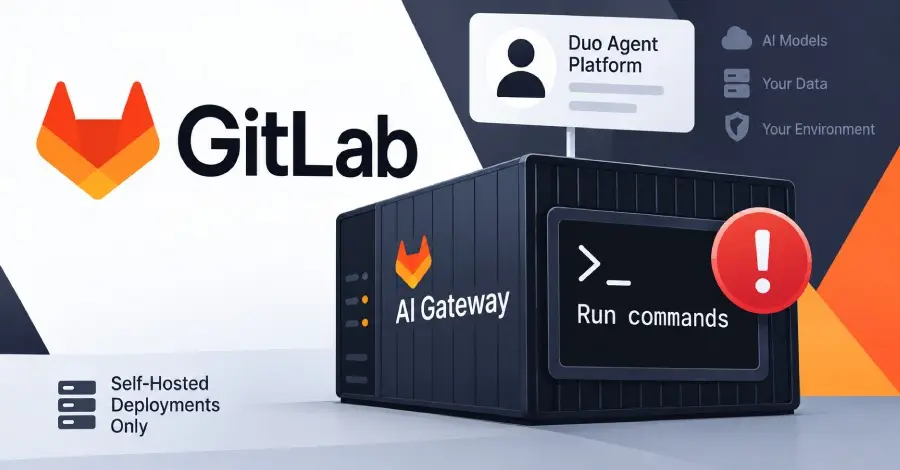
The recurring nature of these flaws highlights the inherent difficulty in sandboxing AI-related workflows. As AI becomes more deeply integrated into the software development lifecycle (SDLC), the tools that manage these interactions become high-value targets. The AI Gateway, by design, handles the "prompts" that define how an AI assists a developer. If those prompts can be manipulated to interact with the underlying system shell, the security of the entire CI/CD pipeline is put at risk.
Security Recommendations and Best Practices
GitLab has been proactive in its communication, reportedly reaching out to customers known to be using self-hosted gateways before the public advisory was published. This "heads-up" approach is part of a broader trend in the industry to give administrators a lead time to patch critical infrastructure before the details are made public.
At this time, there are no known workarounds for the vulnerability. Organizations that cannot immediately update their AI Gateway are left with few options other than temporarily disabling the AI features or restricting access to the Duo Agent Platform to a minimal number of highly trusted users. Given the severity of the RCE risk, GitLab strongly recommends that all affected customers prioritize the update.
Furthermore, the advisory does not provide a specific method for administrators to audit their systems for signs of past exploitation. In the absence of such guidance, security teams are encouraged to review their gateway logs for unusual process executions or unexpected network outbound connections, which are often indicators of an RCE event.
The discovery of CVE-2026-90970 was credited to a security researcher known as "invisiblemeerkat," who reported the issue through GitLab’s bug bounty program on the HackerOne platform. Such programs continue to be a vital component of the security landscape, allowing vendors to identify and remediate "zero-day" level threats before they can be weaponized by malicious actors.
As organizations continue to adopt AI-driven development tools, this incident serves as a reminder that the infrastructure supporting these tools must be managed with the same rigor as any other critical enterprise service. The AI Gateway is a powerful enabler for developer productivity, but its role as a bridge between internal codebases and external AI models makes its security paramount. Administrators are urged to verify their gateway versions immediately and apply the necessary patches to protect their environments from potential exploitation.
 Cybersecurity Basics & Security News
Advanced Wazza Phishing Kit Leverages Multi-Stage Routing and Device Code Tactics to Target Critical Global Sectors
The landscape of email-based threats is undergoing a fundamental transformation. Phishing kits,...
 Cybersecurity Basics & Security News
Google Issues Global Warning Over Mass Exploitation of Critical Oracle PeopleSoft Vulnerability
Cybersecurity researchers at Google’s Mandiant division have issued an urgent warning regarding...
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...







