
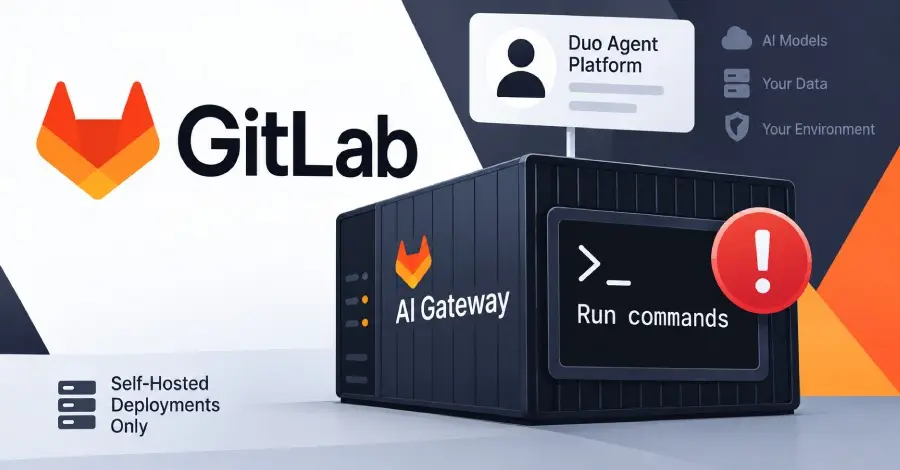
Scope of Affected Versions and Necessary Actions
The vulnerability affects a broad range of AI Gateway versions, specifically those starting from version 18.1.6. GitLab has identified that all releases within the 19.1 line and earlier versions back to 18.1.6 are susceptible to the exploit. The company has released three specific patched versions to address the issue: 19.2.4, 19.3.2, and 19.4.1.
For organizations running their own AI Gateway, the update process depends on how the service was initially deployed. Most self-hosted gateways are managed as Docker images or via Helm charts for Kubernetes environments. Administrators utilizing Docker must stop their current containers, remove them, and pull the updated image tags, such as the "self-hosted-v19.4.1-ee" tag. Those using Helm must update the image settings within their charts to point to the new, secure versions.
It is important to note that GitLab’s maintenance policy generally covers the three most recent minor versions of the software. As of the disclosure date, these are versions 19.4, 19.3, and 19.2. The fact that fixes were released for these specific lines aligns with this policy, but it also leaves questions for organizations running older, out-of-maintenance versions. GitLab’s installation documentation typically recommends that the AI Gateway version matches the minor version of the GitLab instance. If an organization is running a version older than 19.2, they may need to perform a more comprehensive upgrade of their entire GitLab environment to ensure compatibility with the patched gateway.
GitLab has confirmed that it has already updated the AI Gateways it manages for GitLab.com and GitLab Dedicated customers. Therefore, organizations using these managed services do not need to take any action. The burden of mitigation falls entirely on those who have opted for the self-hosted gateway model to maintain data sovereignty.
Assessment of Current Risk and Historical Context
Despite the critical severity of the flaw, there are currently no reports of CVE-2026-90970 being exploited in the wild. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) reviewed the vulnerability upon its disclosure and, as of October 2, categorized the exploitation status as "none." This assessment suggests that while the potential for damage is high, the security community has not yet observed active attacks or the public release of a functional proof-of-concept (PoC) exploit.
However, the high CVSS score often serves as a catalyst for threat actors to begin reverse-engineering the patch to develop their own exploits. The requirement for the attacker to be a logged-in user with Duo Agent Platform access provides some level of mitigation, as it prevents unauthenticated attackers on the open internet from reaching the flaw. Nevertheless, in large enterprise environments where many developers or automated systems may have such access, the internal threat surface remains substantial.

This incident is not the first time the GitLab AI Gateway has faced a critical security challenge. In February 2026, GitLab addressed a similar vulnerability, CVE-2026-1868, which also received a 9.9 CVSS score. That previous flaw similarly involved crafted flow definitions and could lead to denial of service or remote code execution. Both vulnerabilities share the same CWE-1336 classification, pointing to a recurring challenge in securing the template engines used for AI prompt orchestration.
 Cybersecurity Basics & Security News
GitHub Actions Compromised in ‘Mini Shai-Hulud’ Attack Disabled Again Following Brief Reappearance
The cybersecurity landscape has been reminded once again of the persistent and...
 Cybersecurity Basics & Security News
The Evolution of the Vulnerability Gap: Defending Against the Rise of Mythos-Class AI Attacks
In the modern cybersecurity landscape, the arrival of a new Common Vulnerabilities...
 Cybersecurity Basics & Security News
Cloudflare Resolves Critical Cross-Tenant Data Leakage Flaw in Container Infrastructure
Cloudflare has recently addressed a significant security vulnerability within its containerized infrastructure...







