
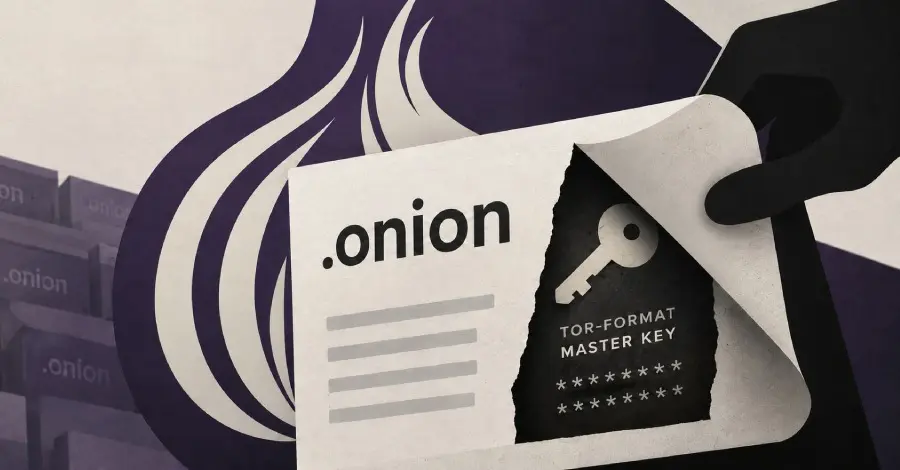
However, the risk is not universal for all GoBalance users. The vulnerability specifically affects hidden services that store their master keys in Tor’s native key format. GoBalance’s own setup utility includes an option to write keys in a different, safer format that is not susceptible to this specific extraction method. Consequently, while the threat is widespread across the dark-web ecosystem, not every service utilizing the GoBalance or EndGame toolkits is necessarily exposed. The determining factor is how the administrator initially generated and stored their site’s cryptographic identity.
The Dread Takeover
The real-world consequences of this flaw became apparent during a chaotic period between October 5 and October 7, involving Dread, one of the most prominent community forums on the dark web. Dread, which serves as a central hub for news and discussion within the dark-net community, is managed by administrators known by the pseudonyms HugBunter and Paris.
The incident began on October 5, when users noticed that Dread’s primary .onion address was no longer leading to the forum. Instead, visitors were being redirected to Conclave, a competing platform. Initially, the administrators believed the issue was the result of a manual error. Paris issued a public statement admitting that he had "stupidly uploaded dread’s main onion private key into a gobalance update," suggesting a simple case of administrative negligence.

However, the situation escalated two days later when Dread’s secondary address—a backup link reserved for premium members and trusted partners—was also hijacked and redirected to the same rival site. Unlike the primary address, the backup key had not been handled in the same update, making a manual leak highly unlikely. This second takeover prompted the administrators to reassess the situation. HugBunter later concluded that an attacker had exploited a previously unknown vulnerability in GoBalance to target multiple dark-web services simultaneously. Searchlight Cyber’s research supports this conclusion, noting that while the first address could have been a manual leak, the systematic takeover of the backup address is a clear indicator of a software-level exploit.
Following the compromise, the Dread team was forced to abandon their long-standing addresses entirely. They have since migrated to a new .onion domain and urged their user base to reset their passwords immediately. In a signed message released on October 7, the operators confirmed the forum had moved "permanently, following onion private key exposure due to a vulnerability in third-party software." They emphasized that while their addresses were hijacked, the forum’s back-end servers remained secure and were never breached by the attackers.
Who Else Is Affected
The full extent of the damage caused by the GoBalance flaw remains difficult to quantify, largely due to the anonymous and secretive nature of the dark web. HugBunter has claimed that several other major dark-web markets and services had their addresses seized during the same period, including some platforms that had already ceased operations but still maintained active .onion addresses. However, the administrator did not provide a specific list of affected entities.
At least one other major service has publicly confirmed its victimization. Omega, a well-known dark-web marketplace, released a signed statement on October 8 acknowledging that it had taken its original address offline "due to an issue caused by the GoBalance bug." Like Dread, Omega was forced to establish a new cryptographic identity and migrate its traffic to a fresh .onion address to regain control over its platform and protect its users from redirection attacks.
 Cybersecurity Basics & Security News
AI vs. AI: How Researchers Used Claude Opus 5 to Breach OpenAI’s Internal Systems
In a sophisticated demonstration of the "double-edged sword" nature of generative artificial...
 Cybersecurity Basics & Security News
Google Pixel 10 and Samsung Galaxy S26 Breached as Ikotas Labs Claims Top Honors at Pwn2Own Ireland 2026
The competitive landscape of cybersecurity research reached a fever pitch this week...
 Cybersecurity Basics & Security News
Russia-Aligned Cyber Espionage Group UAC-0099 Deploys New ASHVEIN Malware in Sophisticated Campaign Against Ukraine
The landscape of cyber warfare in Eastern Europe continues to shift as...







