
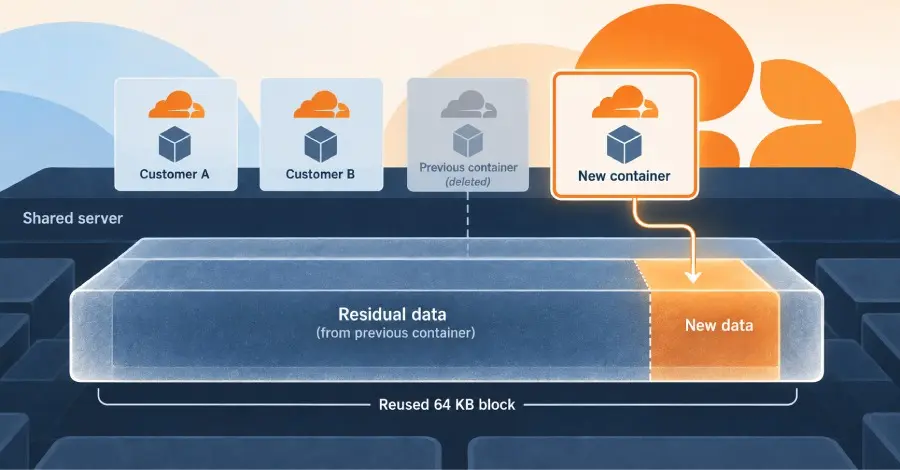
Following the fix, Cloudflare conducted a forensic investigation to determine if the vulnerability had been exploited by any malicious actors prior to the researchers’ report. The company’s security team developed detection signatures based on the researchers’ proof-of-concept and their own internal reproductions of the attack. They then scanned their historical disk-activity records for any signs of similar behavior. According to Cloudflare, this audit revealed only the authorized testing performed by the Accomplish researchers and Cloudflare’s own engineers. No evidence was found to suggest that any other party had discovered or utilized this specific method of data extraction.
While the investigation found no evidence of prior abuse, the total duration of the exposure remains somewhat unclear. Cloudflare’s audit was limited by the retention period of its disk-activity logs, and the company did not specify exactly when the unsafe configuration was first introduced into its production environment. This leaves a question mark over how long the "skip wiping" setting had been active before it was caught by the bug bounty program.
The researchers at Accomplish noted that this discovery is part of a broader trend in cloud security research focusing on sandbox escapes and cross-tenant isolation. This particular flaw marks the sixth time since July that the firm has successfully identified a way to escape or compromise a code sandbox. Their previous findings include vulnerabilities in Anthropic’s Claude Cowork and Claude Code, the command-line tool for the Cursor AI editor, Docker, and OpenAI’s Codex. The researchers also mentioned that the same disk configuration issue affected Cloudflare’s "Browser Run" product, though Cloudflare’s official post specifically highlighted Containers and Sandboxes as the impacted services.
As of the time of disclosure, Cloudflare has stated that the vulnerability is fully patched and that customers do not need to take any action, such as rotating keys or changing passwords, unless they have specific reasons to believe their data might have been exposed through other means. The incident serves as a stark reminder of the technical intricacies involved in cloud isolation. In the world of high-performance computing, where every microsecond and every kilobyte of overhead counts, a seemingly minor optimization—like skipping the zeroing of a disk block—can inadvertently create a significant security gap. Through the collaboration between independent researchers and the company’s internal security teams, the flaw was identified and mitigated before it could be exploited by malicious actors, demonstrating the ongoing value of the bug bounty model in securing global internet infrastructure.
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...
 Cybersecurity Basics & Security News
Google Pixel 10 and Samsung Galaxy S26 Breached as Ikotas Labs Claims Top Honors at Pwn2Own Ireland 2026
The competitive landscape of cybersecurity research reached a fever pitch this week...
 Cybersecurity Basics & Security News
Critical Check Point Flaw Grants Unauthenticated Root Access to Management Servers
A severe security vulnerability has been identified within Check Point’s Security Management...







