
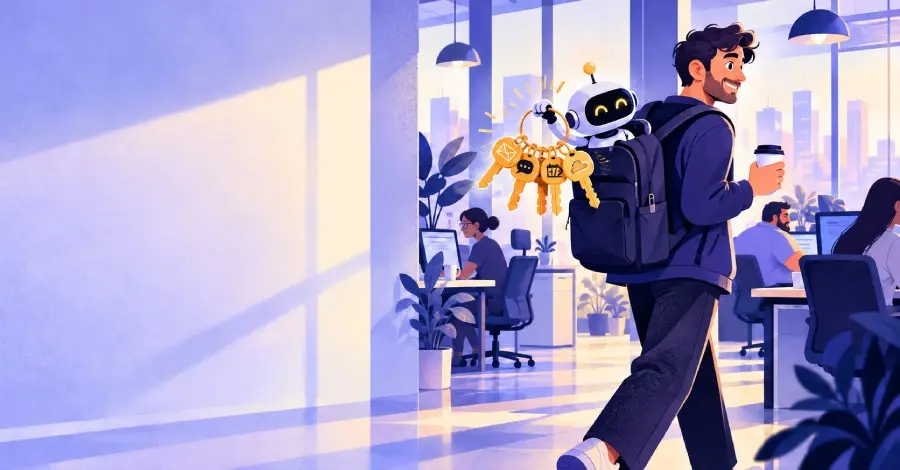
The problem, however, is that these controls only apply to corporate-sanctioned accounts. Truly personal AI agents—those owned by the individual and used across their entire life—do not appear in the corporate admin console. This creates a dilemma for leadership: the instinct may be to block these "unauthorized" agents entirely, but doing so risks stifling the significant productivity gains that employees are beginning to realize.
A more pragmatic approach is to treat the personal agent as an external entity. In this model, the workplace acknowledges that the agent is run by a third-party vendor and owned by the employee, but focuses its control on the "other end" of the connection: the accounts, permission grants, and active sessions within the company’s own systems.
This distinction is critical when comparing cloud-based agents to local ones. Cloud agents, like Muse, often run in a dedicated virtual machine. Muse employs a guard called "Sentinel" to check outbound requests and handle tokens, ensuring the agent itself never touches raw credentials. While this architecture is thoughtful, it enforces the user’s personal policy rather than the employer’s, and it results in corporate session tokens residing on a third-party vendor’s server. Local agents, like OpenClaw, keep credentials on the user’s laptop, but they offer no way for the corporate network to distinguish between the actions of the employee and the actions of the bot.
Enabling the Agent through Identity Governance
The ideal solution for the modern enterprise is not total prohibition, but a strategy of "safe enablement." This involves allowing employees to reap the benefits of their personal agents while the workplace maintains control over the reach of those agents through the identity layer.
To achieve this, organizations must move toward a model where identity serves as the primary control plane. This requires the ability to distinguish between a human login and an agent login, even when they share the same credentials. It also requires a more granular approach to "compartmentalizing" knowledge. One of the greatest risks of BYOAI is that a personal agent may retain sensitive corporate information long after an employee has left the company. Currently, the industry lacks a standardized way to ensure that an agent "forgets" specific work-related knowledge during the offboarding process.
Furthermore, the challenge of agent-to-agent communication remains largely unsolved. As corporate agents begin to interact with personal agents to negotiate schedules or exchange data, the potential for "prompt injection" or unauthorized data egress increases.
While vendors continue to develop the "connective tissue" needed to bridge personal AI and the workplace, organizations do not have to wait for the market to mature. Solutions like Token Security are already beginning to fill this gap by identifying personal agents connected to corporate systems and tying them back to their human owners. By trimming unnecessary access and ensuring that agent sessions are terminated when an employee departs, these tools allow identity to function as the necessary safeguard.
In the coming months, the ability to govern the digital identities used by AI will become the defining characteristic of a secure enterprise. Personal agents are no longer a future prospect; they are an active presence in the modern workforce. Managing them requires a shift in perspective—from seeing them as "rogue bots" to recognizing them as a new class of identity that must be observed, managed, and secured.
 Cybersecurity Basics & Security News
Critical Cryptographic Flaw in GoBalance Load Balancer Exposes Dark Web Sites to Takeover Attacks
A significant security vulnerability discovered in GoBalance, a specialized load-balancing tool widely...
 Cybersecurity Basics & Security News
The Invisible Attack Surface: Why Comprehensive Detection is the New Baseline for Credential Security
In the modern enterprise, credentials have become the fundamental currency of operations....
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...







