
In a significant blow to state-sponsored cyber espionage operations, the United States Department of Justice and the Federal Bureau of Investigation (FBI) have announced the successful seizure of several domains used by a prominent Chinese cyber-espionage contractor. The operation targeted the digital infrastructure of Integrity Technology Group, a firm deeply embedded within the Chinese government’s offensive cyber ecosystem. By taking control of these domains, federal authorities have effectively disrupted access to a pair of sophisticated hacking tools that have been instrumental in compromising critical infrastructure and corporate networks on a global scale.
The disruption marks a pivotal moment in the ongoing effort to dismantle the technical foundations used by the "Flax Typhoon" cybercrime group. Also known by various aliases such as Ethereal Panda and Red Juliett, this threat actor has long been a primary concern for Western intelligence agencies. The group is characterized by its systematic targeting of high-value sectors, including telecommunications, energy, and government services, often acting on behalf of the People’s Republic of China (PRC) to facilitate intelligence gathering and maintain a persistent presence within foreign networks.
Central to the FBI’s operation were two primary tools: Microscan and FishHub. According to investigators, these utilities were the "bread and butter" of the group’s operations, providing the means to both identify vulnerabilities and maintain unauthorized access to victim systems. The seizure of the domains associated with these tools is expected to significantly hamper the group’s ability to conduct large-scale reconnaissance and manage its sprawling network of compromised devices.
The Role of Integrity Technology Group
Integrity Technology Group, the entity at the heart of this disruption, represents a growing trend in the landscape of international cyber warfare: the state-sponsored contractor. Based in China, the company maintains formal contracts with the Chinese government, acting as a private-sector arm for state-level espionage. This model allows the PRC to scale its operations rapidly, leveraging the expertise of private security firms to conduct widespread campaigns while maintaining a degree of plausible deniability.
The activities of Integrity Tech have been tracked across multiple major campaigns. Security researchers have linked the company’s infrastructure to several high-profile Advanced Persistent Threat (APT) groups. While "Flax Typhoon" is the most prominent name associated with this activity, the group’s footprints are also found in operations labeled as Ethereal Panda and Red Juliett. These groups are known for their technical agility, moving between different sets of tools and infrastructure to evade detection.
Assistant Director Brett Leatherman of the FBI’s Cyber Division highlighted the strategic importance of targeting these contractor-led operations. "Integrity Technology Group provided China-linked threat actors with capabilities used to conduct widespread vulnerability scanning and, in some cases, intrusions targeting US and foreign critical infrastructure," Leatherman stated. He emphasized that the PRC’s reliance on these enabling companies is a vulnerability that Western law enforcement is increasingly keen to exploit. "By exposing and disrupting these enablers, we make it harder for the PRC to target American networks and infrastructure."
A Multi-Faceted Tactical Approach
 Helpdesk & IT Service Management (ITSM)
Omdia Research Highlights Significant Cost Savings and Operational Gains for MSPs and IT Teams Adopting Unified Management Platforms
In an era defined by tightening budgets and an explosion of digital...
 Helpdesk & IT Service Management (ITSM)
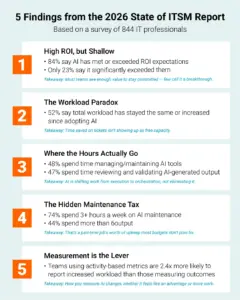
The Paradox of Efficiency: SolarWinds 2026 Report Highlights the Growing Pains of AI Integration in ITSM
The promise of artificial intelligence within the IT Service Management (ITSM) sector...
 Helpdesk & IT Service Management (ITSM)
The Evolution of Service Delivery: Understanding the Strategic Shift Toward Enterprise Service Management
In the modern corporate landscape, the efficiency of an organization is often...







