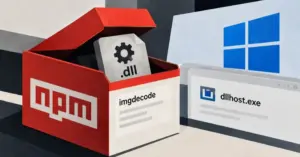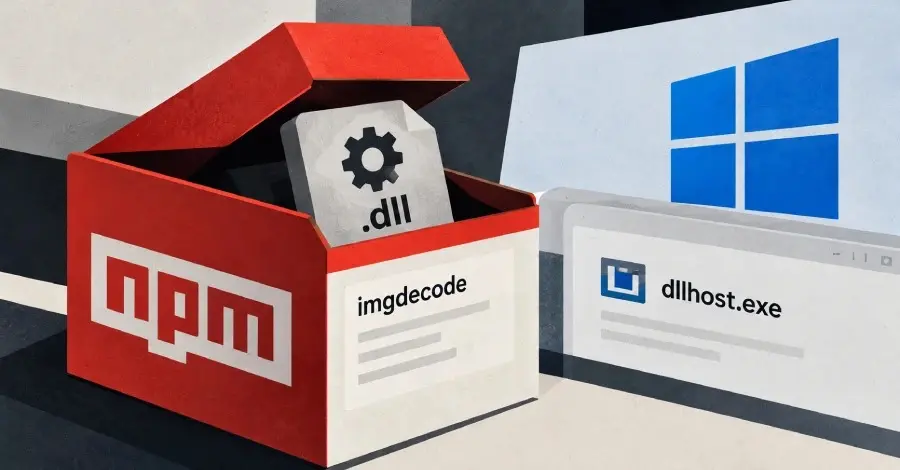
Cybersecurity researchers have identified a sophisticated new entry in the ongoing software supply chain attack campaign known as MALFEX, marking a significant escalation in the threat actor’s technical approach. The discovery involves a malicious npm package titled "imgdecode," which leverages native Node.js addons to bypass traditional security scans and compromise Windows environments. This latest development underscores the persistent nature of the MALFEX threat actor, who has been actively targeting the JavaScript ecosystem for over three years with a rotating arsenal of malicious packages designed to exfiltrate sensitive data and establish remote control over infected systems.
The package in question, "imgdecode," was first uploaded to the npm package registry on September 30, 2026, by a user operating under the handle "malfexteste8." Despite its malicious intent, the package managed to garner 979 downloads before being flagged by security professionals. As of the latest reports, the package reached version 1.0.3, demonstrating a rapid development cycle as the attacker refined the delivery mechanism to evade detection. The campaign’s longevity and the actor’s ability to quickly replace removed packages highlight a systemic challenge in securing open-source repositories against determined adversaries.
According to a detailed analysis by security firm SafeDep, the "imgdecode" package represents a departure from simpler, script-based malware. It utilizes a compiled Node.js native addon to hide its malicious loader, a tactic that significantly complicates static analysis. While the package includes a deceptive nine-line JavaScript file, its primary function is to load a Windows dynamic-link library (DLL). When a developer or an automated system executes a Node.js program that calls the "require(‘imgdecode’)" command from a Windows console, the underlying DLL is triggered. Once active, this DLL attempts to communicate with a GitHub repository to download encrypted shellcode, which it then decrypts and injects into a legitimate system process, specifically "dllhost.exe," to mask its presence on the host machine.
The MALFEX campaign is not a new phenomenon in the cybersecurity landscape. It was first documented by researchers at Checkmarx and CloudSEK, who identified it as a long-running operation aimed at compromising Windows-based development environments. Since at least August 6, 2023, the unknown threat actor behind MALFEX has been systematically publishing malicious packages to npm. These efforts have been distributed across a variety of publisher handles, including malfexkkj, malfex_user, malfexteste2, malfexteste3, and malfexteste4. This multi-account strategy allows the attacker to maintain a presence on the registry even after individual accounts or packages are reported and removed.
The broader campaign has utilized several distinct infection pathways. In earlier iterations, researchers identified eight specific packages, three of which served as loaders for the Overlord Remote Access Trojan (RAT). Another set of three packages—"cdn-img-fetch," "img-to-native," and "native-runner"—operated in a coordinated chain to download and execute a Node.js-based stealer. A third, more traditional method involved the use of npm "postinstall" hooks, which automatically execute JavaScript code upon installation to contact external servers and retrieve secondary malicious binaries.
 Cybersecurity Basics & Security News
Unmasking Lunex: The Rapid Expansion of a Sophisticated Malware-as-a-Service Platform Targeting Ukraine
The cybersecurity landscape is witnessing the emergence of a highly sophisticated Malware-as-a-Service...
 Cybersecurity Basics & Security News
OpenAI Dismisses Safety Researchers Following Leak of Confidential Infrastructure Data Amid Growing Security Concerns
OpenAI has terminated the employment of three prominent members of its safety...
 Cybersecurity Basics & Security News
The Silent Proliferation: Enterprise Security Grapples with the Rise of Invisible AI Agents
As the enterprise landscape prepares for the full-scale integration of artificial intelligence,...